Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

In Modern AppSec, DevSecOps Demands Cultural Change

This is the final of a six-part blog series that highlights findings from a new Mend white paper, Five Principles of Modern Application Security Programs. When thinking of adjectives to describe cyberattackers, it’s doubtful that many people would choose to call them innovative – a term we’re more likely to ascribe to things we enjoy. But the reality is that adversaries are innovative, constantly finding new ways to launch attacks that result in greater rewards for less effort.
Why tool consolidation matters for developer security

With threats to cloud native applications rising, security leaders feel more pressure than ever to counter an ever-changing risk landscape. But thanks to a rapidly expanding security solutions market, many respond to these growing demands by adding more products. With so many new tools arising to tackle security challenges, it sometimes seems like the right answer is always “one tool out of reach”.

DevSecOps: The What, Why, Who, and How

By way of a brief introduction, I have had a 25+ year career in technology, and this has come with some wonderful experiences and opportunities along the way. One constant throughout my journey has been a need to increasingly leverage data, enabling informed decisions (even automated) at all levels to ensure: secure, high performing and observable products and services are available to the customers and partners I’ve been supporting.

Hackathon! How can blockchain solve supply chain visibility challenges?

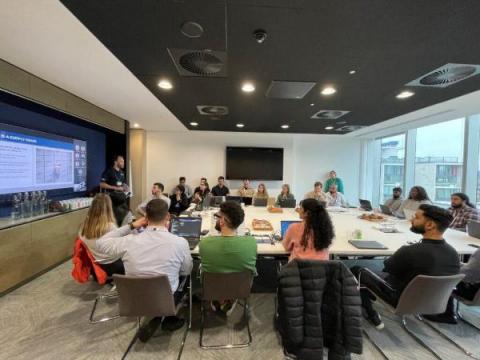
PA Consulting recently joined forces with RKVST to host a Hackathon, looking to identify new and innovative propositions for digital supply chains. Could the teams of PA consultants and analysts identify opportunities to help their clients using RKVST technology? Short answer: YES! Many of today’s business challenges can be addressed with a reliable evidence ledger. If you want the long answer, read on.

What is DevSecOps: A Comprehensive Guide

The rise of cloud, containers, and microservices has shifted the way software developers work for good. Whereas traditionally, software developers would release a new version of an application every few months, today’s platforms allow teams to work faster and more streamlined. These advancements have led to the rise of “software, safer, sooner” — also known as DevSecOps.

RKVST supply chain evidence management platform now available to the public sector through UK Government G-Cloud

RKVST™ announces its award-winning enterprise SaaS solution is now available as an assured cloud service through G-Cloud 13, the UK Government's cloud services procurement framework.
Featured Post

Bridging the DevSecOps Application Connectivity Disconnect via IaC

Anat Kleinmann, AlgoSec's Sr. Product Manager and IaC expert, discusses how incorporating Infrastructure-as-Code into DevSecOps can allow teams to take a preventive approach to secure application connectivity.

How to take DevSecOps to the next level: A conversation with SecOps and DevOps leaders from NielsenIQ, ARA Security and Techstrong Group

When delivering customer experiences from the cloud, defending the app includes the data it houses and the business it represents. The DevSecOps mindset, “You build it, you run it, you secure it” helps, but only when all teams are empowered with the info they need to see a threat, regardless of where it is.