Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Explaining PHP2Shell | Arctic Wolf Threat Brief

In this explainer from Arctic Wolf's Peter Ingebrigtsen, we break down what the PHP2Shell vulnerabilities are, how attackers are exploiting them, and the steps organizations should take now to reduce exposure. Arctic Wolf customers can use Aurora Exposure Management to identify affected assets and prioritize remediation, while the Aurora Agentic SOC helps detect and respond to post-exploitation activity such as webshell deployment, unauthorized command execution, persistence, and lateral movement.
AI SOC Adoption: Where to Start in the First 90 Days

John White is the Field CISO for EMEA at Torq. A respected security executive with more than 20 years of leadership experience, John previously served as CISO at Virgin Atlantic, where he led a multi-year transformation deploying the Torq AI SOC Platform to modernize cyber operations. Prior to Virgin Atlantic, he built and transformed security functions for global organizations, including ASOS, Liberty Global, AEG Europe, and KPMG. You’ve signed the AI SOC contract.

Everyone Says Context Matters. I Wanted Proof.

Amir Kessler is Director of Product Management at Torq, where he leads the Context Engine and Data Fabric, the layer that gives the AI SOC Platform the organizational context it needs to investigate and act. He joined Torq with its acquisition of Jit, where he was VP of Product. Amir has spent more than 15 years in cyber, starting in IDF intelligence and going on to lead product teams at several security companies. Before Jit became part of Torq, we built our product on one bet.

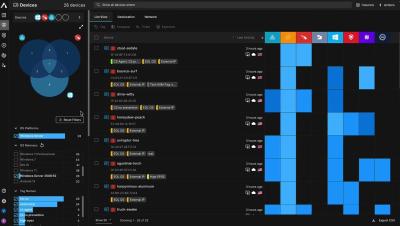
How to Find Security Gaps Using the Aurora Attack Surface Management Venn Diagram

How do you find devices that your security tools don't cover? The Integration Venn Diagram in Arctic Wolf Aurora Attack Surface Management (ASM) compares data from Active Directory, CrowdStrike, Automox, SentinelOne, and Qualys in one view, so you can see coverage gaps, unmanaged devices, and blind spots that no single tool reveals. In this demo, we start with 3,631 devices and layer in data sources one at a time to find.

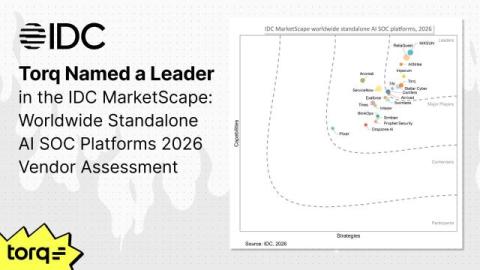
Torq Named a Leader in IDC MarketScape: Worldwide Standalone AI SOC Platforms 2026 Vendor Assessment

Chris Kissel, Vice President of IDC Security & Trust, just drew a line in the sand for the AI SOC category with one simple sentence: “Vendors that can show their agents reason transparently, act within defined guardrails, and improve with each investigation will define this category. The rest will be measured against them.” We couldn’t agree more.

What Is SOC (Security Operations Centre) and Does Your Business Need One?

A security operations centre (SOC) is the team that watches your systems around the clock and steps in when an attacker gets past your defences. Its job is to find intruders quickly and contain them before reaching anything critical. Few businesses have their own in-house SOC. Most get the same 24/7 cover from a managed SOC, run by a specialist provider. Either way, what happens in the first few hours of an attack determines how much damage is done.

AW Chief Revenue Officer Will May on AI, Security Operations and Cyber Resilience | MTS Live

Everything is accelerating, and so simply put, if your technologies and your teams aren’t accelerating at the same rate that the threat landscape is, you’re in trouble.” Live from the 2026 Security Operations Summit, Arctic Wolf Chief Revenue Officer Will May joined Monitor the Situation to discuss how security operations are evolving in the age of AI.

The Autonomous SOC Was a Promise SOAR Never Kept

David Melamed is Head of Emerging Technologies at Torq. He joined through Torq’s acquisition of Jit, which he co-founded and has led as CTO since 2020, building agentic security on a production Context Graph. A cloud security veteran with 20+ years of experience, David previously held senior technical roles at Cisco (via the CloudLock acquisition) and MyHeritage. For all the gods and monsters in The Odyssey, the ship mostly moves for one reason: men row it.

Why SOC Teams Need Runtime Visibility From Their CNAPP

Many companies run their software on cloud servers that come and go on their own. When traffic spikes, new ones switch on automatically. When it drops, they shut down, sometimes less than an hour after they started. That flexibility saves money, but it creates challenges for the people whose job is to investigate attacks.

Three AI SOC Differentiators That Separate Real From Marketing

Every vendor in this category now says the same word: agentic. I understand why. It’s what the market wants to hear. But when you’re the one signing the contract, “agentic” tells you almost nothing. I’ve sat on the buying side of enough of these conversations to know that the label and the capability are often two very different things.