Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

SOC metrics that prove your security actually works

SOC metrics are quantifiable measures of how well a security operations center detects, investigates, and contains threats. The metrics that matter most are mean time to detect (MTTD), mean time to respond (MTTR), and incident closure rate, because together they show speed, effectiveness, and reliability, not just activity.
Buying an AI SOC Isn't Like Anything You've Bought Before

John White is the Field CISO for EMEA at Torq. A respected security executive with more than 20 years of leadership experience, John previously served as CISO at Virgin Atlantic, where he led a multi-year transformation deploying the Torq AI SOC Platform to modernize cyber operations. Prior to Virgin Atlantic, he built and transformed security functions for global organizations, including ASOS, Liberty Global, AEG Europe, and KPMG.

Build the Self-Driving SOC with Tanium Security Operations

Attackers don't wait for humans, and neither should your SOC. Tanium Security Operations brings detection, investigation, hunting, and response together on one platform that moves at machine speed. See how Tanium Atlas works as an extension of your team: pulling live telemetry, historical activity, and the full process tree the moment a threat surfaces, hunting a hypothesis across every endpoint in your fleet, and containing threats from one endpoint to hundreds of thousands. When the hunt needs to go deeper, HuntIQ's hands-on experts take it from there, inside your environment.

Announcing LimaCharlie Email Security: Natively Integrated Into Your SecOps Stack

Co-founder & CCO LimaCharlie Email Security is generally available today. It protects Microsoft 365 and Google Workspace mailboxes from inside the same tenant, permission model, and data lake as the rest of LimaCharlie. A phishing email and the endpoint activity it causes can now be detected, investigated, and remediated in one place.

Beyond Triage: How the Aurora Agentic SOC Enhances the Concierge Experience

A lot of the current conversation about agentic SOCs is about triage. Faster detection, faster investigation, alerts resolved in minutes instead of hours. When we set out to build the Aurora Agentic SOC, we didn’t just want to make triage faster. We fundamentally re-engineered our SOC to strengthen every job it does, and enhancing the Concierge Experience for our customers was a key part of that.

How Security Orchestration Protects DevOps Environments at Scale

DevOps moves fast by design. Continuous integration, automated deployments, and infrastructure-as-code let development teams ship features in hours rather than weeks. Security teams have a real opportunity here: when they build workflows that integrate directly into the development process, they gain coverage and response speed that manual, disconnected approaches leave on the table.

How to Use Aurora Security Assistant for Deeper Security Expertise and Context

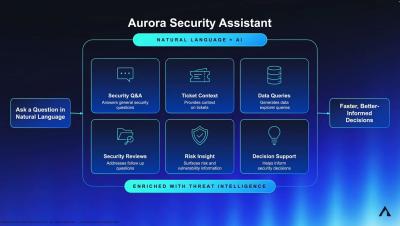
In this demo, we will look at different use cases for the Aurora Security Assistant including the data explorer queries, organizational risk and vulnerability information, and quick answers around self-service and product documentation.

How the Arctic Wolf Agentic SOC Delivers Faster, More Accurate Security Outcomes

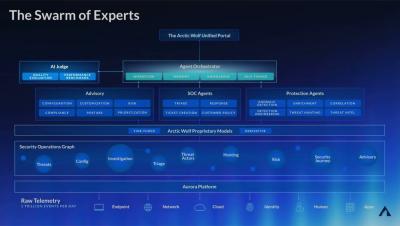
Learn how Arctic Wolf Superintelligence Platform and the Swarm of Experts work together to deliver faster, more accurate outcomes for customers by leveraging unmatched telemetry, deterministic models, our golden data set and human expertise.