Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Cyber Risk in the Wild: The Shadow AI User UpGuard

The shadow AI user is notoriously hard to observe. This elusive creature hunts in incognito tabs and leaves almost no trace on the approved tools list. In this episode of Cyber Risk in the Wild, a looming deadline draws one employee into the open, and the pride’s AI policy is put to the test. UpGuard User Risk uncovers the shadow AI and unsanctioned SaaS your teams are using, blocks risky uploads and pastes in the browser, and redirects people to approved AI tools in the moment.
The shadow AI user has one weakness... UpGuard

The shadow AI user is notoriously hard to observe. This elusive creature hunts in incognito tabs and leaves almost no trace on the approved tools list. In this rare footage, a looming deadline draws one employee into the open, and an unapproved AI tool is only a few keystrokes away. Even the stealthiest hunter can be stopped, though. UpGuard User Risk uncovers shadow AI across your workforce and redirects people to approved tools in the moment.

OpenMatter Network Positions Decentralized Computing as an Alternative to Data Centers for AI

OpenMatter Network, a pioneer in decentralized infrastructure for agentic artificial intelligence, is positioning its decentralized computing platform as an alternative to massive, centralized data center development amid growing public opposition to new facilities. The company says its approach can support continued AI adoption by enabling computing workloads to run across distributed resources rather than relying primarily on large-scale data center infrastructure.

Agentic AI Security: The Risks Every Business Must Know | Erich Kron (KnowBe4)

AI agents don't just answer questions; they take action. And when an AI agent gets bad information, a wrong answer can quickly become a security incident. In this 403 Circle webinar powered by Astra Security, Erich Kron (CISO Advisor at KnowBe4, 30 years in cybersecurity, former Security Manager of the U.S. Army's Second Regional Cyber Center) breaks down why agentic AI is going to change the way we do business and what security leaders need to do before handing autonomous AI agents the keys.

AI transformation means reaching the point of no return

There’s a simple way to know when technology has been truly transformative. It’s when your work would fall apart if you took it away. Think about electricity, the internet, personal computers — we’re pathetically helpless when they break, and we’d struggle to redesign work without them. Very few teams have reached this point with AI. Software engineers are the exception — AI has radically changed how they build and ship software.

Agents aren't humans (but they kinda are)

AI Agents now act on the web for millions of people. To a Site, an Agent can take many forms. It may be indistinguishable from a human user carrying out a task, or it might look like one visitor carrying many Users. This removes the ability for the Site to recognize, serve, and hold accountable the user or users behind the Agent, and causes the Site to face the costs when something goes wrong.

Stop Destructive AI Agent Commands Before They Run | Cato AI Security

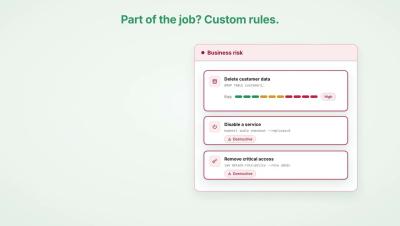
Coding agents now have real access to cloud resources, code repositories and identity systems. That access brings a new kind of risk: a single unclear request, or an attacker who takes over the agent, can trigger actions that are hard or impossible to undo. That’s why Cato now detects destructive commands before they execute.

How to Vet AI and SaaS Tools Before They Become a Security Risk

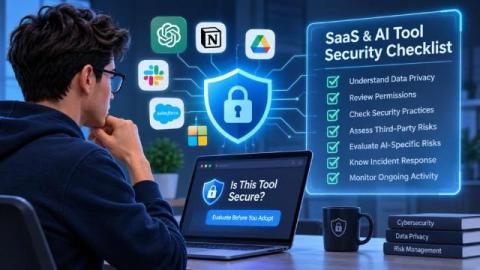
Businesses are adopting new software faster than ever. From AI-powered assistants and automated workflows to cloud-based project management platforms, there is a tool for almost every business function. While these applications improve productivity, they also introduce security risks that organizations often overlook. Every new SaaS platform creates another potential entry point into your organization's digital environment. It might process customer information, store confidential documents, connect to internal systems, or receive access to employee accounts.