Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

From Encrypted Mobile Traffic to Payment Manipulation

How KomodoSec’s AigentX Penetration Tester reverse engineered client-side encryption, turned the bypass into reusable Burp tooling, and used that access to validate a real business-logic flaw in a production mobile application. Client-side secrecy failed. Server-side trust became the real vulnerability. THE CHALLENGE A mobile app with TLS, certificate pinning, and a second encryption layer.

Why Buy a Mobile AppSec Platform Instead of Building With AI?

AI has lowered the cost of building mobile security tooling to near zero. However, it has not lowered the cost of operating it. Building a scanner is now a weekend project, while sustaining detection accuracy, threat research, real-device infrastructure, and developer trust across years remains a full organizational commitment. That distinction is the entire build-versus-buy question in 2026, and most evaluations get it wrong by measuring the wrong thing.

How to Hide the Status Bar and the Notification Bar on Android Devices?

Android devices are designed for flexibility. Employees can check notifications, adjust connectivity, open settings, and move between apps with a few taps. That flexibility works well for personal use, but it can introduce distractions, security gaps, and usability issues when a device is dedicated to business tasks.

Board Foot Calculator Apps for Android

This is a working comparison of five Android options, written for people who bid, order, and take delivery on lumber for a living. No formula refresher, no explanation of what a quarter is. The question here is narrower: which board foot calculator app for android holds up when the tape says 6' 2-13/16", the crew is waiting, and a rounding error becomes a short order or a return trip.

Aikido launches agentic pentesting for Android apps

TL;DR: Aikido now pentests Android apps. The same agents that test your web apps and APIs can now work through your APK, log into the app, and reason through it, alongside the backend it talks to, in a single assessment. Findings come back with reproduction steps and are ready for an AutoFix, the same as any other Aikido pentest. Aikido has been running autonomous pentests against web apps and APIs since November 2025.

How Mobile App Agencies Use GPS and Fintech Expertise to Build Smarter Apps

What happens when an app knows not just who a user is, but where they are and how they'd prefer to pay? Location and financial technology stop behaving like separate features and start functioning as one connected layer of the experience. In a market like Melbourne, where mobile products increasingly need to work across commuting, retail, delivery, and everyday payments, that combination is often the difference between an app that feels genuinely useful and one that just checks boxes.

Why Annual Mobile App Security Testing Is Not Enough on Its Own

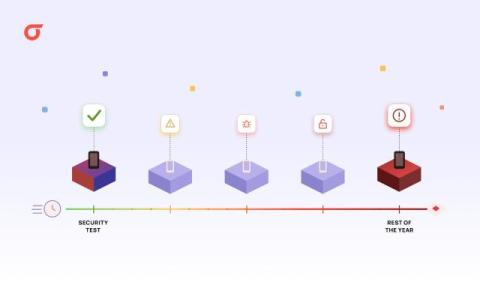
Annual testing secures a moment. Your app keeps changing. Here is how to cover the interval between assessments. An annual penetration test answers a precise question. Was this version of this application secure when a skilled tester examined it? That answer has real value. It is independent, deep, and finds business logic flaws that no scanner will ever surface. It is also a photograph.

How to Choose a React Native Development Company for AI-Driven Mobile Projects

AI-driven mobile apps grow more complex every month. The gap between a team that can actually ship one and a team that merely claims they can is wider than most product managers expect. Wrong hires cost you four to six months of rework on top of the initial build, a brutal, avoidable tax. So if you're planning a mobile product that uses machine learning, on-device inference, or real-time AI features, vendor selection deserves far more rigor than skimming a portfolio and firing off a request for proposal.

4 Easy Steps To Secure Mobile Field Work

A field tech at a customer site can log into a scheduling app, pull up an invoice, and snap a site photo in under five minutes while connected to open Wi-Fi. That mobile device holds customer addresses, signed work orders, access codes, account credentials, and job-site photos. Unlike an office workstation that sits behind a firewall and never leaves the building, a field device moves through unfamiliar networks and high-risk physical spaces daily.