Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

The latest News and Information on Security Incident and Event Management.

Is "SIEM-less" really what it sounds like?

SIEM-less security may sound like an escape from traditional SIEM complexity and costs, but the underlying capabilities still have to exist somewhere. A SIEM is a multipurpose tool. It brings together cyber and physical security use cases; drives threat detection, investigation, and response (TDIR); serves as a system of record for governance, regulatory, and compliance needs; and supports observability use cases tied to resilience and service degradation. The list goes on.
How to investigate PHP2Shell-related activity with Sumo Logic

PHP2Shell is a pair of critical flaws in the PHP interpreter itself, each with a CVSS v4.0 score of 9.2. Both let an unauthenticated attacker run code on a web server with a single crafted web request, or a pair of them, before any application code runs. Because the bug lives in PHP, not in WordPress, Drupal or Magento, every reachable PHP endpoint on an affected server is exposed, including login pages, static forms, and health checks. Every PHP release from the last decade is affected (back to 5.4).

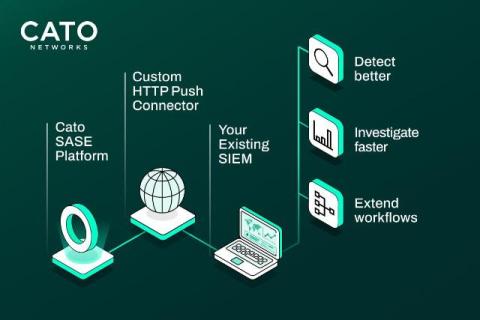
Make Your SIEM Smarter with Cato

Effective security operations require more than isolated alerts. Analysts need context from across the environment to understand what happened, assess its significance, and decide what to do next. That is why accessing insights and telemetry from across your networking and security stack is critical to teams using a SIEM tool.

Access Isn't Trust: A Behavioral Risk Framework for People, Service Accounts, and AI Agents

Risk in the agentic enterprise spans people, service accounts, and AI agents. All three act with legitimate credentials, so access controls alone can’t show whether their activity is safe. A behavioral risk framework applies one model to every actor: Verify expected behavior before access goes live, observe activity once it does, analyze behavior for risk and drift, and improve detection coverage over time.
Sponsored Post

Windows Hardening & Continuous Compliance: Keeping 200+ Security Settings Secure 24/7

Every Operating System – not even counting the software installed on top of it – has a myriad of configuration settings that affect security. Windows Server alone has 4000+ configurable options, out of which 200+ are important for security & compliance efforts. They include: These settings are at the very core of all of your security & compliance efforts – and they are surprisingly often ignored.

Elastic Security integration with Google Distributed Cloud: Closing the velocity gap in air-gapped environments

The rules of cyber defense have shifted. Threat actors are increasingly using advanced automation to accelerate reconnaissance, evade static signatures, and orchestrate rapid intrusions across critical infrastructure, software supply chains, and insider pathways. This has created a critical velocity gap: when adversaries compress attack timelines from days to minutes and defenders rely on manual triage across fragmented legacy tools, the defense falls behind.

What are the 5 pillars of Zero Trust? [Quick Question Ep. 4]

What are the five pillars of Zero Trust? Across Zero Trust frameworks, five control points remain consistent: users, devices, networks, applications, and data. In this episode of Quick Question, we cover how each pillar generates critical security data, and why that data often lives in disconnected tools, leaving organizations with a fragmented view.

Why SOC Teams Need Runtime Visibility From Their CNAPP

Many companies run their software on cloud servers that come and go on their own. When traffic spikes, new ones switch on automatically. When it drops, they shut down, sometimes less than an hour after they started. That flexibility saves money, but it creates challenges for the people whose job is to investigate attacks.