Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

XWorm Malware: Worming Its Way From Entry to Exploitation

XWorm is a versatile modular malware that presents a multifaceted threat landscape. This malware can be employed for various malicious purposes, including remote access, data theft, ransomware delivery, and botnet creation. Despite being relatively new in the cyber threat landscape, XWorm has rapidly gained notoriety, largely due to its association with the DDGroup cybercrime group, renowned for its utilization of advanced malware techniques.
The first 72 hours of a ransomware attack: Why restored isn't recovered

You start the day with reports that your employees cannot access critical systems. A ransom note soon explains why: attackers have encrypted them and demand $2 million in bitcoin for a decryption key. Your team contains the attack and confirms that the backups are safe, yet this is only the beginning. Restoring your servers can take weeks, but recovering the business can take much longer.

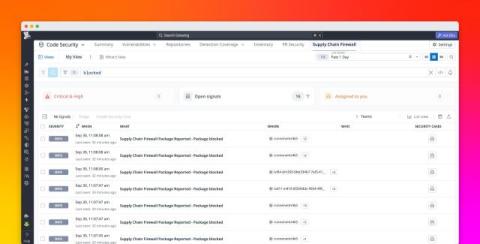
Block malicious packages across your organization with Supply Chain Firewall and Datadog Code Security

Campaigns such as Shai-Hulud 2.0 have demonstrated how quickly package malware can propagate through npm and then harvest credentials. Traditional dependency scanning can identify known risks in code once a package is added to the code, but security teams also need a check before installation.

Recover OT Systems After Ransomware with Acronis Cyber Protect

When ransomware disrupts a manufacturing site, every minute of downtime matters. See how Acronis Cyber Protect supports the controlled recovery of engineering servers, SCADA systems and manufacturing databases from a last known good state, helping OT and IT teams verify system integrity and resume production with confidence.

SalatStealer Malware: Inside a Credential Stealer Built for Repeat Use

SalatStealer is a Go-based infostealer family first observed in August 2026, built for x86 Windows environments and focused on credential theft. Its documented capabilities include stealing authentication credentials, hiding executing code, and degrading security software.

Rubrik MSP Unscripted Episode 7 - Featuring Rajat Shah

In this episode of MSP Unscripted, Nawaz Ali sits down with Rajat Shah, Product Manager at Rubrik, to talk about the launch of multi-tenancy and what it means for managed service providers. Nawaz and Rajat discuss how shared infrastructure can help MSPs improve service economics while maintaining strong tenant isolation, expand opportunities across SMB and mid-market customers, and make services such as Backup as a Service, Disaster Recovery as a Service, isolated recovery environments, and advanced cyber recovery capabilities more scalable.

Graphalgo campaign spreads to Terraform providers and Go Modules

We’ve identified Go malware distributed via at least two Terraform providers and at least two Go Modules. This is the first time we’ve observed malware distributed via Terraform providers. The following packages contain the malware: The malware overlaps with the Graphalgo NPM malware campaign, first reported by ReversingLabs in February 2026, and also reported on in the last week by Safedep, CheckMarx, and JFrog.

How to Protect Backups from Ransomware

Ransomware crews go after backups first. Before any production file gets encrypted, they hunt down your backup catalog, snapshots, and repository credentials. The real question is whether your backups can survive an attacker who is actively trying to destroy them. This guide covers how to protect backups from ransomware with specifics: immutable and WORM storage, the 3-2-1-1-0 rule, air-gapping, network segmentation, encryption, and access controls that hold up under pressure.

CISA: Ransomware Gangs Now Exploit Critical VMware vCenter Flaw

The U.S. Cybersecurity and Infrastructure Security Agency has warned that ransomware groups are now exploiting a critical VMware vCenter Server bug that Broadcom patched on 29 July 2026. The issue is CVE-2026-59310. It is a directory traversal flaw in the vCenter Syslog server. An attacker who can reach the server on the network does not need a password. Successful use can lead to remote code execution. The published severity score is 9.8.