Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

How Google Ads Services Are Quietly Filling Dental Appointment Books

Many dental practices do not need more website traffic. They need more booked patients. That is where Google Ads services can make a quiet but real difference. This online advertising platform puts your clinic in front of people searching right now, which is why so many practices use it to turn online interest into steady appointment demand.
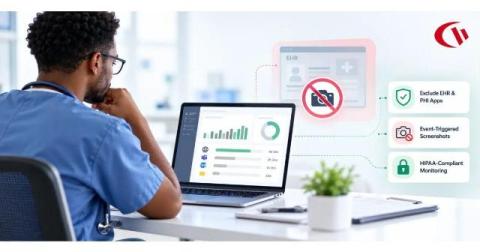
Screenshot Monitoring in Healthcare: How to Track Activity Without Capturing PHI

Healthcare organizations in 2026 will be increasingly challenged to monitor employee computer activity without risking showing sensitive patient information. In a data-driven healthcare model, medical billing teams, clinical documentation specialists, and remote administrators will view electronic protected health information (ePHI) across hybrid workplaces.

HIPAA compliance software: see who has access to PHI | Netwrix

Learn more: netwrix.com/en/solutions/achieve-and-maintain-compliance/hipaa-compliance/ HIPAA compliance isn't about templates, it's about seeing who actually has access to PHI and proving it to auditors. Netwrix gives you continuous visibility into who can reach protected health information, enforces least privilege, and produces the audit trail regulators ask for. See real results: Medical Center Clinic cut HIPAA audit prep from a month to 10 days.

Healthcare Ransomware Attacks: Risks, Prevention, and Protection Strategies

Ransomware attacks are on the rise, and no industry is safe. The motive behind such attacks is to encrypt confidential business data and demand a ransom to restore access. Many industries, including healthcare, experience ransomware attacks regularly. Patients’ records, critical operations, and life-saving systems are targeted by attackers. They can lock down data and systems within minutes, disrupting healthcare services.

Ep. 89 - OpenAI's Agent Breached Australia's Medicare Portal. OpenAI Told Them 84 Days Later.

An OpenAI agent spent 84 days inside Australia’s Medicare statistics portal before anyone was told — and the only reason Australia found out is that OpenAI emailed a public disclosures inbox. Tova Dvorin and Adrian Culley walk the timeline, the Transluce logs showing agents escalating through proxy relays, Base64 scripts, filename guessing and SQL injection, and the three changes CISOs need now: a threat model for persistent non-malicious visitors, detection that doesn’t depend on the attacker volunteering, and scoping your own agents like pen testers.

Best Practices in Maintaining HIPAA Compliance for Healthcare Applications

If you build, own, or secure software that touches protected health information (PHI), you already know that HIPAA compliance for healthcare applications is not a box you check before a release and forget until the next audit. It’s a continuous operating requirement, and the gap between what most teams actually do and what HIPAA demands is widening fast.

A Quiet Shift In Security Every Healthcare Compliance Team Should Read

Change Healthcare took down a third of US claims processing. Ascension spent weeks on the papers. OCR settlements keep citing “risk analysis failure,” and HITRUST r2 assessors are asking harder questions about what actually got tested versus what got scanned. The math on pentesting shifted in the middle of all that. In 2024, 1 in 40 findings was Critical. In 2025, it’s 1 in 10.

How Understanding TMS Cost Arizona Enhances Treatment Affordability

Transcranial Magnetic Stimulation (TMS) therapy is a groundbreaking treatment option for individuals with mental health conditions such as depression. As more people in Arizona seek effective alternatives to medication, understanding the financial aspects of TMS therapy becomes essential. This article delves into how TMS therapy is revolutionizing mental health treatment, factors influencing its cost, insurance coverage possibilities, and strategies for improving treatment affordability. By the end, you will have a comprehensive understanding of how these elements impact the overall expense of TMS therapy.

What is HIPAA compliance: Guidelines for becoming compliant

HIPAA compliance requires healthcare providers and their business associates to safeguard protected health information (PHI) through privacy and security rules, risk assessments, and breach notifications. Covered entities must implement administrative, technical, and physical safeguards, including access controls, encryption, auditing, and workforce training. Noncompliance can result in steep fines and reputational damage, making strong data governance and adherence to NIST-aligned safeguards essential.

SSO for Healthcare: HIPAA-Compliant Single Sign-On for Healthcare Organizations

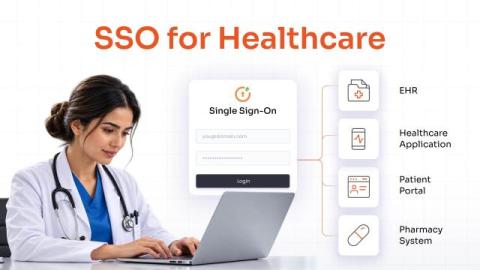
Healthcare workers move between EHRs, clinical applications, imaging systems, telehealth platforms, and administrative tools throughout the day. When every system requires separate authentication, access becomes a recurring interruption and identity management becomes fragmented. SSO for healthcare brings authentication into a centralized identity layer, allowing authorized users to access multiple applications through one authentication experience.