Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

The latest News and Information on Application Security including monitoring, testing, and open source.

State of Application Security

Our View from the Front Lines of Technical Assessments Kroll analyzed five years of penetration testing data. Of the trends that emerged, we focus on three in this report: the static application security testing (SAST)/software composition analysis (SCA) plateau, the need for more attention around authentication and authorization, and the security health divergence, which shows that regulation is not a reliable predictor of attack surface health.
AI is building your software. Who's making the security decisions?

AI coding assistants are changing how software gets built. Traditional AppSec tools focus heavily on scanning the final code artifact, but as AI agents move from simple code dependencies to autonomous decision-makers and execution paths, traditional security controls enter the process too late.

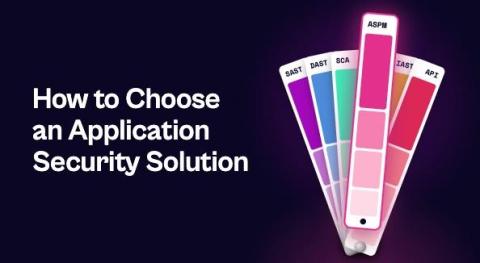
How to Choose an Application Security Solution

Most teams need a combination of application security tools rather than a single one. Common categories are SAST, DAST, IAST/RASP, SCA, API and container security, and ASPM, and each covers a different stage of development. When you evaluate options, look for coverage that matches your stack, integration with developer workflows, accurate findings, risk-based prioritization, and actionable remediation guidance.

Why Application Security Testing Isn't Disappearing - and How Veracode is Shaping What Comes Next

Application security testing (AST) is the practice of scanning software for vulnerabilities using static, dynamic, and component-level analysis – then managing those flaws through remediation, validation, and certification. A new independent report from FOURCASTERS and Lionfish Tech Advisors confirms that AST is not becoming obsolete. AI and cloud platforms are changing how testing gets delivered, but the need for independent testing, flaw lifecycle management, and validation has only grown.

Mobile App Security: Reverse-Engineering APKs and IPAs to Uncover Hidden Attack Vectors

Buried in OpenAI’s evaluations of its GPT-6 Astra model sits a finding that mobile teams should sit with for a minute. The model reverse-engineered compiled software well enough to escape a browser sandbox and chain privilege-escalation flaws on a hardened operating system, according to the company’s published evaluations. Reading compiled binaries used to be specialist work priced in weeks, and now it’s something machines do quickly and well.

How attackers use AI models to find code vulnerabilities

AI models accelerate software development, but attackers use those same capabilities to hunt for pipeline vulnerabilities. Asaf Saar (EVP and Chief Product Officer, Mend.io) and Christian Jensen (VP Engineering, Tricentis) break down why full visibility is required to secure AI-native software.

Cyber Resilience Act is here! Myth busting and first impressions

The first deadline of the Cyber Resilience Act went live last week. The Cyber Resilience Act (CRA) is the new EU regulation that defines minimum cybersecurity requirements for all products with digital elements, including their building blocks (hardware and software). It applies to anyone placing products on the EU market, not just companies based there. The full requirements won’t go into effect until the end of next year.

Graphalgo campaign spreads to Terraform providers and Go Modules

We’ve identified Go malware distributed via at least two Terraform providers and at least two Go Modules. This is the first time we’ve observed malware distributed via Terraform providers. The following packages contain the malware: The malware overlaps with the Graphalgo NPM malware campaign, first reported by ReversingLabs in February 2026, and also reported on in the last week by Safedep, CheckMarx, and JFrog.