Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

The latest News and Information on Insider Threats including employee monitoring and data privacy.

Insider risk starts with who can read the data

Insider risk is often framed as an external attacker problem, but a real blind spot sits closer to home: who inside your own security stack can open sensitive files they never needed to see. Classification tools that require broad scanning access often hand that same access to every admin who configures them, turning the tool meant to reduce exposure into another path to it. The people with the least oversight, your own admins, can end up with the most unchecked visibility into regulated data.
Who's Behind Your AI Agent? | Teramind AI Usage Control

An AI agent can summarize, classify, and move customer data in seconds. An activity log can tell you what happened, but not why a person set it in motion. Teramind AI Usage Control connects the human action to the AI tool, the data involved, and the behavior that follows, across devices, apps, and workflows. With Teramind, security and IT teams can.

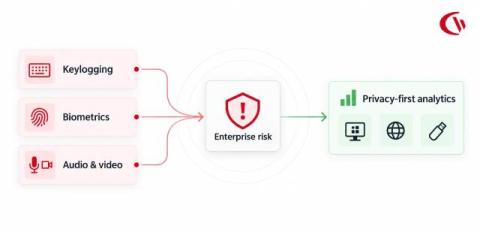
Workplace Biometrics, Keylogging & Wiretapping Laws: Enterprise Risk Assessment Guide

For years, employers assumed that owning the laptop and the network meant unlimited monitoring rights. In 2026, that assumption no longer holds. Federal wiretap law, state biometric statutes, all-party consent requirements and the EU Artificial Intelligence Act each limit what an employer can collect and how. Most workplace surveillance software must weigh the competing goals of safeguarding corporate resources and respecting employees’ right to privacy.

AI Agent Security: The Hidden Threat Your Firewall Can't Stop

If your AI security strategy is focused on stopping copy-pastes into chatbots, you're fighting yesterday's war. AI agent security is now the real endpoint challenge — autonomous agents operating with your users' credentials. Traditional firewalls, CASBs, and DLP weren't built for agentic AI. They can't see delegated credentials, multi-step tool calls, or live runtime execution across IDEs, browsers, and local apps.

Next-Gen Web Filtering for Remote & Hybrid Workforces: Category Enforcement, DoH Defense & SafeSearch

Today, laptops are rarely connected to the corporate network – more often they’re connected to wifi at home, mobile wifi on the road, and a coffee shop hotspot the IT team never set up. Office perimeter firewalls have nothing to analyze when the device leaves the building, and cloud DNS filtering doesn’t work unless the DNS traffic actually reaches the cloud. That’s why more IT teams are moving web filtering to the device itself.

Remote Employee Productivity Tracking: The Non-Invasive Playbook for Hybrid Teams

Hybrid and remote work have forever changed the way organizations structure their approach to people, technology, and performance. In Gallup’s 2026 Workplace Indicators, 52% of U.S. employees who can work remotely are in a hybrid model, and 26% are fully remote. As distributed work is here to stay, organisations need a trusted way to understand how employees use business applications, access resources, and do their work, without turning the workplace into a surveillance operation.

Remote Work Security & Endpoint DLP: How to Prevent Exfiltration on Distributed Laptops

The corporate security perimeter has changed. An employee’s company laptop could easily arrive at work on a Monday morning connected to a home Wi-Fi network, then land in a hotel or workspace at noon on a Tuesday and work away from a hotspot on Wednesday. That leaves corporate data outside the reach of traditional IT and security controls.

The Critical Asset Nobody Thought to Protect

Ask an organization about its most critical assets and you'll hear the usual answers: health records, PHI, sensitive data. Then one person said fertilizer. The room laughed until he explained. With large grounds to maintain, the organization kept big stores of it on site, and in the wrong hands, that becomes a serious physical threat. Insider risk isn't only about files. It's about anything that could cause harm if someone misused it.

Employee Investigations: How to Close the Digital Evidence Gap

Your DLP flags a sensitive file transfer. Your SIEM identifies unusual activity. Your EDR detects an event on an employee’s endpoint. Your security tools did their job. They told you something happened. But now comes the harder question: What actually happened? That is where many employee investigations encounter a visibility gap.

Insider Risk Breaks the Frequency Side of the Model

External threat models estimate how often somebody gets in and what they reach afterward. The susceptibility term does most of the work, weighing what an attacker can do against what the controls prevent. ‍ An insider is already inside. The credentials are valid, the access is entitled and the workflow is familiar. None of that makes the model harder to run, it changes which side of it breaks, and the break is on frequency rather than on magnitude. ‍