Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

The Cybersecurity Directive That Reached Ten Times More Entities

The headline change in Europe's network security directive is scope. Directive (EU) 2022/2555 reaches an estimated hundred and sixty thousand entities across eighteen sectors, roughly ten times what its predecessor covered. ‍ The more consequential change is who decides. Under the previous regime a member state identified operators of essential services individually, through an assessment of criticality and dependency.
The AI Act Duty That Applies Regardless of Risk Tier

Almost every obligation in the AI Act is keyed to a risk classification. Work out which tier a system falls into and the duties follow. ‍ Article 4 is not. It applies to providers and deployers of any AI system whatever it does, its subject is people rather than systems, and national authorities began supervising and enforcing it from 2 August 2026 while the high-risk regime moved to December 2027. It is the live one, and it sits outside the structure most governance programs are built on. ‍

Cyber Resilience Act is here! Myth busting and first impressions

The first deadline of the Cyber Resilience Act went live last week. The Cyber Resilience Act (CRA) is the new EU regulation that defines minimum cybersecurity requirements for all products with digital elements, including their building blocks (hardware and software). It applies to anyone placing products on the EU market, not just companies based there. The full requirements won’t go into effect until the end of next year.

DPDP Readiness for Indian Businesses From Compliance Requirements to Data Protection

India’s Digital Personal Data Protection (DPDP) framework is changing how businesses need to manage and protect personal data. In this video we explore what DPDP readiness means in practice and how organizations can strengthen their approach to protecting personal data throughout its lifecycle. The session covers: The webinar also discusses how backup and recovery capabilities can support a broader data-protection and compliance strategy, including encryption, access control, immutable storage, policy-based retention, centralized management, and recovery.

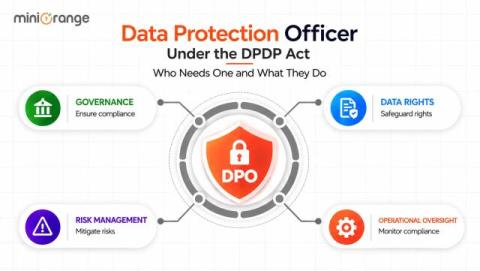
Data Protection Officer Under the DPDP Act: Who Needs One and What They Do

Not every organization that processes personal data has to appoint a Data Protection Officer. Under India's Digital Personal Data Protection Act, 2023, this duty applies only to Significant Data Fiduciaries (SDFs), a category the government assigns based on the scale and sensitivity of the data an entity handles. So before you assume your business needs a data protection officer, it helps to know exactly where this obligation begins and ends.

The EU Cyber Resilience Act Has Global Implications - Who Needs to Prepare and How?

The European Union has made great strides to enhance cybersecurity over the past few years, with a comprehensive framework of core legislative acts designed to protect critical infrastructure. The EU Cyber Resilience Act, originally published as Regulation (EU) 2024/2847 on 20 November 2024, and entered into force on 10 December 2024, shifts the burden of proof so that manufacturers must now show their software is secure, not just claim it.

Cyber Resilience Act Preparedness: Who's Ready, and Who Can't Be Reached

Computers are not safe. Even the best hardware and software products have the potential to conceal as-yet unknown vulnerabilities. And they aren’t all made that well. Many are shuffled into the world without a plan to detect, remediate, and notify users of those vulnerabilities. The EU’s Cyber Resilience Act aims to improve that situation.

December 2026 Is Closer Than You Think: What the UK's Defence Cyber Directive Means for Your Organisation

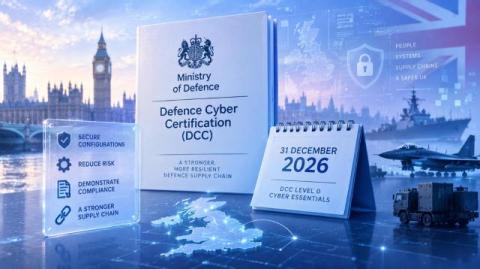
The UK’s Ministry of Defence has sent a clear message to organisations within the Defence supply chain. By 31 December 2026, all Defence industry partners are expected to achieve Defence Cyber Certification (DCC) Level 0, including Cyber Essentials for all applicable business-critical systems within scope. This represents a significant step in strengthening cyber resilience across the Defence ecosystem and raising the baseline for cyber security throughout the UK’s supply chain.

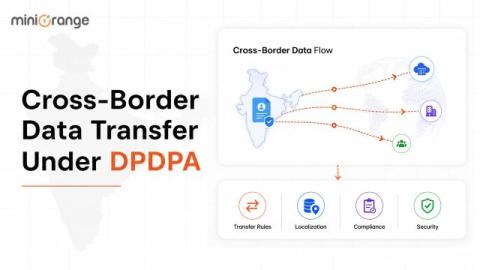
Cross-Border Data Transfer Under India's DPDPA

Businesses operating across countries routinely move personal data between India and overseas systems. Customer information may be stored by a global cloud provider, employee records may be accessed by an international headquarters, or an Indian business may use SaaS platforms whose infrastructure is located outside the country.

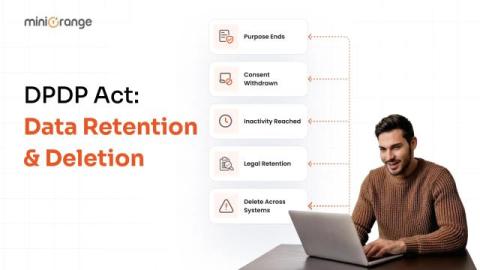
Data Retention Policy Under the DPDP Act: How Long You Can Keep Data and When to Delete It

How long should an organization keep personal data? Under the DPDP Act, the answer is not simply one year, three years, or any other fixed period. The right retention period depends on why the data was collected, whether that purpose still exists, and whether another law requires the organization to keep it.