Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Oops, OpenAI Hacked Australia's Health System - The 443 Podcast - Episode 389

This week on the podcast, we cover yet another rogue AI security incident that Australia's Prime Minister disclosed in front of the United Nations last week. Before that, we discuss an FBI alert on WaterPlum, a North Korean threat actor targeting IT professionals. Then, we cover the FBI themselves becoming a victim of cyberattack, this time by ShinyHunters.

4 Simple Habits To Stop Email Hackers

Stopping email hackers requires adopting four specific habits: letting AI filter inbound messages, identifying manufactured urgency, verifying requests through second channels, and locking accounts with passkeys. These zero-skill routines block the credential-harvesting tactics that compromise shopping, streaming, and financial profiles. Consider a content creator receiving a brand partnership offer from a recognizable sportswear company. The logo perfectly matches the corporate website, the tone sounds professional, and the message includes a simple link labeled to review the contract.

No Hackers Required: 10 Shadow AI Leaks Hiding in Plain Sight

“The call is coming from inside the house.” It’s one of horror’s oldest lines, and you already know how the scene goes. The team scrambles, rechecks every firewall, audits every login, hunting for an intruder. Then the trace comes back, and there isn’t one because there is no malware or forced entry. Just an employee, at their own desk, with their own login, who pasted a confidential spreadsheet into an unapproved AI tool to save 10 minutes before a deadline.

Jason Chan has 26 minutes to shut down a hacker hidden in plain sight (Live Tabletop Exercise)

What do you do when an attacker doesn’t break into your network, but simply walks in by turning your own multi-factor authentication against you? In this episode of The Tabletop, Jason Chan takes the hot seat and works the problem in real time.

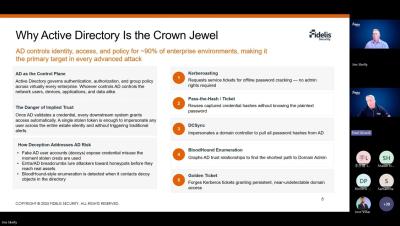
The Real Reason Hackers Target Active Directory First

Active Directory controls access to nearly every application, file, and system in your network. That's exactly why it's the first thing attackers go after. Get privileged access to AD, and an attacker doesn't need to break into ten different systems. They just need one path in, and from there they can move freely, escalate privileges, and sit undetected for weeks. AI is making this worse. Faster reconnaissance, sharper phishing, quicker lateral movement, all pointed straight at identity infrastructure.

AI hacking makes password spraying faster. Here's how to close the gap

AI hacking tools are compressing the time between finding a target and logging in as them. Password spraying, already responsible for the vast majority of identity attacks, is the technique benefiting most. Attackers use AI hacking methods to optimize timing, rotate infrastructure, and personalize lures at a scale no human operator could match manually.