
Seattle, WA, USA
1996
  |  By Mick McCarter
Cloud applications are constantly evolving to accommodate new users, tools, and ways of working. However, every adjustment can also alter who has access to resources and what they can do with them. A misconfiguration occurs when an active setting fails to meet established security criteria. It can grant more access than necessary, keep an insecure protocol enabled, allow certain actions for too many users, or open a pathway for information to leave the organization.
  |  By Euler Neto
MSPs are used to blocking malicious domains, detecting suspicious IP addresses, and continuously updating their defenses against emerging threats. However, what happens when attackers can shift their infrastructure in near real-time without interrupting the campaign? The ErrTraffic campaign, analyzed by the WatchGuard Threat Lab, provides an example of how malware distribution techniques are evolving.
  |  By Iratxe Vazquez
Security teams are managing more endpoints, identities, networks, and security events than ever. Each control adds valuable protection, but the work of connecting its signals, explaining incidents, and deciding what needs attention often falls to analysts. That is why the next evolution of WatchGuard ThreatSync and Rai Analyst matters. ThreatSync provides the foundation for cross-product detection, correlation, incident management, and coordinated response.
  |  By Mick McCarter
The rise of AI tools in the workplace has put Shadow AI firmly on the cybersecurity agenda. Employees are increasingly adopting AI services without IT or security approval, potentially creating security, privacy, and compliance risks. But focusing on Shadow AI alone misses the bigger issue. The real question is not just which AI tools employees use, but whether organizations understand what is happening across their entire SaaS environment.
  |  By Carlos Arnal
Every MSP has heard the question in some form: how do you know this actually works? For most security products, the honest answer is a mix of vendor documentation, analyst reports, and your own experience. All useful, but none of it is a verdict from someone with no stake in the result. Spain’s public sector works differently. When government agencies there buy security products, they look to CPSTIC, a catalog run by Spain’s National Cryptologic Centre (CCN).
  |  By Kim Maibaum
When MSPs evaluate MDR services, the conversation usually starts in the same place: Tell me about your SOC and how quickly you respond. Those are good to know, but they don't tell you one thing that determines whether the service works: how much of your clients' environments the provider can see and act on. A SOC that's available 24/7 but only watching half the environment isn't protecting your clients. It's giving your clients a false sense of security.
  |  By Matthew Terry
If you're an MSP or MSSP, you've probably had some version of this conversation with a customer: “We just found out we need to comply with NIS2, DORA , HIPAA, PCI DSS... What do we need to buy?” It's a fair question. It's also usually the wrong first question — and answering it well is where you create real value for your customers.
  |  By Sarah Smith
For years, companies treated shadow IT primarily as a policy and control problem. Employees have always found and used technology outside the approved IT stack, from unauthorized endpoint applications and browser extensions to personal cloud services. It left a trail: an install, a device on the network, something a scan or an agent could eventually catch. From there, an analyst had to investigate the finding and assess the risk before deciding how to respond.
  |  By Corey Nachreiner
Security is built on the small decisions we make each day. That’s why Cybersecurity Awareness Month 2026 focuses on the habits that make life harder for attackers—such as using strong passwords, enabling multi-factor authentication (MFA), recognizing and reporting scams, and keeping software updated. However, security awareness must also address the risks that arise when employees introduce new applications and services into their work.
  |  By Iratxe Vazquez
At IMPACT North America, WatchGuard showcased a simple idea with significant implications for managed security: the next phase of cybersecurity AI is not only about helping people work faster. It is about expanding what the security operation itself can do. Today, that next evolution of Rai is generally available. Rai is WatchGuard’s agentic AI Digital Workforce, built specifically for MSPs and embedded in WatchGuard Cloud.
  |  By WatchGuard Technologies
This week on the podcast, we cover the $6 billion cryptocurrency theft from Binance. Before that, we give an update on PHP2Shell and one active exploit campaign targeting Palo Alot devices. Additionally, we discuss a compromised Claude Code extension on the Cursor AI marketplace.
  |  By WatchGuard Technologies
Join WatchGuard’s Corey Nachreiner and Marc Laliberte for a deep dive into Shadow AI breaches from 2025 and 2026. You’ll hear about an AI coding agent that wiped a live database during a code freeze and a hiring chatbot whose admin login was 123456. Then they'll show you how to find the same risks across every client you manage with WatchGuard Cloud Detection and Response (CloudDR).
  |  By WatchGuard Technologies
Network Detection and Response (NDR) has traditionally come with a heavy price tag, including complex deployments, expensive infrastructure, constant tuning, and skilled analysts to manage the workload. That model was built for enterprise SOCs, not MSPs protecting dozens or hundreds of customers.
  |  By WatchGuard Technologies
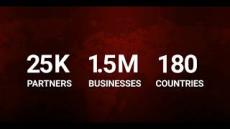
For nearly 30 years, WatchGuard has had one mission: making enterprise-grade cybersecurity accessible to every business. Founded in Seattle in 1996, WatchGuard now protects more than 1.5 million businesses in 81 countries through a network of 25,000 partners.
  |  By WatchGuard Technologies
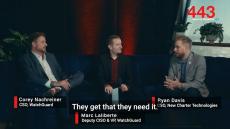
Are you preparing for the threats your region faces, or just the ones making headlines? Cybersecurity risks vary by region. Is your strategy keeping up? In this episode of the Red Cell podcast, Ryan Davis, CISO at New Charter, explores emerging threats and regional security priorities.
  |  By WatchGuard Technologies
This week on the podcast, we dive into a pair of PHP vulnerabilities dubbed PHP2Shell and the chaos they caused through uncoordinated disclosure. After that, we discuss a certificate authority who's random number generator only goes to three digits before ending with law enforcement action around ShinyHunters ransomware negotiators.
  |  By WatchGuard Technologies
Weak or reused passwords can give cybercriminals access to your accounts, often at your expense. As a proud Cybersecurity Awareness Month Champion with the National Cybersecurity Alliance, we're reminding everyone that stronger passwords and smarter security habits make a difference. Don't make it easy for attackers.
  |  By WatchGuard Technologies
New Charter Technologies CISO, Ryan Davis joins The 443 to discuss the evolving cybersecurity landscape across different regions, the unique challenges organizations face, and the trends shaping the future of security. Tune in for insights into emerging threats, regional priorities, and how businesses and partners can stay ahead of an ever-changing threat landscape.
  |  By WatchGuard Technologies
Your clients rely on a growing security stack to protect their business. Endpoint protection, firewalls, identity security, cloud controls, and detection tools all play an important role in reducing risk. But those investments generate a constant stream of alerts, events, and telemetry that need to be monitored, investigated, and acted on. That's where the challenge begins.
  |  By WatchGuard Technologies
In this episode, WatchGuard CSO Corey Nachreiner sits down with Andrew Morgan, founder of Right of Boom, to discuss the evolving role of MSPs in cybersecurity live from Impact Partner Conference in Nashville. From common security gaps and lessons learned from real-world incidents to the impact of AI, Andrew explores what it takes for MSPs to move beyond selling security tools and become true security providers. Tune in to learn how MSPs can better protect themselves and their customers while preparing for the challenges ahead.
  |  By WatchGuard
Ransomware is one of the most talked about and publicized security threats in the modern era. What started as a few high-profile attacks caused by a handful of malware variants has developed into a virulent threat landscape in which increasingly unskilled attackers are able to execute highly effective ransomware campaigns against organizations of all sizes and levels of complexity. Small-to-midsize businesses disproportionately fall victim to ransomware, as they often lack the technical skills and tools needed to prevent infection.
  |  By WatchGuard
Risk-based authentication both enhances security and user experience by allowing you to rank the resources you want to protect based on risk level and type of user. This gives you the power to create rules that are unique to the security structure in your organization, therefore enabling more flexibility or higher protection only when necessary.
  |  By WatchGuard
Cyber attacks grab headlines almost daily. WatchGuard's award-winning network security platform not only provides one of the most complete suites of unified security controls on the market today to detect and prevent these attacks, but our strategy of sourcing the best scanning engines to integrate with our built-in defenses boosts security in critical attack areas. Take a closer look at the WatchGuard security platform's all-star team of best-in-class threat management services.
  |  By WatchGuard
In this eBook we provide you with suggestions on how to start providing some basic but vital security services that will improve the security posture of your customers while increasing your Average Revenue (ARPU), such as endpoint security set-up and monitoring.
  |  By WatchGuard
If you are in the retail or hospitality industries, it's important to know exactly how your network security solution maps to PCI DSS standards. This white paper presents a straight-forward review of PCI requirements and how the WatchGuard platform delivers the capabilities you need to ensure mandates are met.
  |  By WatchGuard
The coronavirus pandemic has exposed business continuity inadequacies at many organizations, and highlighted the slow pace of progress in digital transformation. This new reality necessitates a departure from a traditional network-centric security model that assumes every device and user within the network should be trusted. In this eBook we will explore how the dynamics of COVID-19 have impacted security, outline the importance of a zero-trust approach, and discuss how WatchGuard can help your business deliver the security you need during these trying times.
  |  By WatchGuard
Respected PCI-Qualified Security Assessor Coalfire recently completed a technical assessment of the WatchGuard Threat Detection and Response (TDR) solution, validating it for PCI DSS anti-malware use cases. Download the whitepaper to learn more!
  |  By WatchGuard
The coronavirus pandemic has exposed business continuity inadequacies at many organizations, and highlighted the slow pace of progress in digital transformation. This new reality necessitates a departure from a traditional network-centric security model that assumes every device and user within the network should be trusted.

WatchGuard has deployed nearly a million integrated, multi-function threat management appliances worldwide. Our signature red boxes are architected to be the industry's smartest, fastest, and meanest security devices with every scanning engine running at full throttle.

For 25 years, WatchGuard has pioneered cutting-edge cybersecurity technology and delivered it as easy-to-deploy and easy-to-manage solutions. With industry-leading network and endpoint security, secure Wi-Fi, multi-factor authentication, and network intelligence products and services, WatchGuard enables more than 250,000 small and midsize enterprises from around the globe to protect their most important assets including over 10 million endpoints.

The WatchGuard Difference:

  • Intelligent Protection: Effective protection against today’s vast number of evolving threats requires multiple services working intelligently together. Prevent, detect, and instantly respond to cyber attacks with automated policies.
  • Simplified Management: Managing security across your organization has never been simpler. Use out-of-the-box tools to quickly and easily deploy, configure, and maintain your security with the granularity of your choice.
  • Actionable Visiblity: Monitor and report on the health of your IT infrastructure. Actionable visibility tools enable you to proactively identify threats, while providing corrective action against known issues.

In a world where the cybersecurity landscape is constantly evolving, and new threats emerge each day, WatchGuard makes enterprise-grade cybersecurity technology accessible for every company.