
|
By Vinay Kumar Rasala
In this blog, I'll explain how I found the LinkPresentation out-of-bounds write, later assigned CVE-2026-112621 and fixed in iOS 27.2 and macOS Golden Gate 27.2. LinkPresentation is the framework Apple uses to build link previews, and on an unpatched Mac, one crafted preview in Messages was enough to crash it. That fix shipped on October 26, 2026, and Apple credited me, Vinay Kumar Rasala (Xplo8E) of Appknox, alongside an anonymous researcher.
|
By Dhruv Pandya
KnoxIQ is the agentic triage layer in Appknox. It takes the findings from your SAST and DAST scans, filters out the ones that aren't real and ranks the rest by how exploitable they are in your build. For each one, it shows you how to reproduce it and writes a fix for your app, including a prompt for Claude Code, Cursor, Github Copilot or any AI coding agent.
|
By Samartha J V
On October 21, 2026, PHP shipped emergency fixes for two flaws that let anyone on the internet run code on a PHP web server, with no login. The weakness behind them had been flagged in 2024 and then sat, partly because nobody had proved it was exploitable. In 2026, researchers working with AI models proved it within days. Exploit attempts started before the fix shipped, and details leaked a day ahead of schedule. That sequence is the real story of PHP2Shell. The bug matters, but speed matters more.
|
By Dhruv Pandya
Appknox MCP agent connects your AI coding agent to your Appknox scan results and KnoxIQ analysis. Your agent triages findings by exploitability, fixes the code in your repo and verifies each fix with a re-scan, inside Claude Code, Cursor, GitHub Copilot, Codex or Windsurf. Your AI coding agent already writes features, refactors code and fixes bugs. It can't see your security findings. So when a scan flags a vulnerability in your mobile app, the fix still starts by hand.
|
By Sahana Ananth
Since 11 September 2026, an actively exploited flaw in your app starts a 24-hour reporting clock under the EU's Cyber Resilience Act. That's expensive if you don't know what's running, and an edge if you do. For most companies, an app is a channel. For a mobile-first company, it is the business: the bank branch, the checkout counter, the boarding gate, the clinic waiting room. Until this year, however, the law mostly treated it like a channel.

|
By Rishika Mehrotra
AI has lowered the cost of building mobile security tooling to near zero. However, it has not lowered the cost of operating it. Building a scanner is now a weekend project, while sustaining detection accuracy, threat research, real-device infrastructure, and developer trust across years remains a full organizational commitment. That distinction is the entire build-versus-buy question in 2026, and most evaluations get it wrong by measuring the wrong thing.
|
By Harshit Agarwal
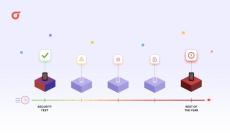
Annual testing secures a moment. Your app keeps changing. Here is how to cover the interval between assessments. An annual penetration test answers a precise question. Was this version of this application secure when a skilled tester examined it? That answer has real value. It is independent, deep, and finds business logic flaws that no scanner will ever surface. It is also a photograph.

|
By Rishika Mehrotra
DORA compliance for mobile applications is the process of identifying, testing, and documenting mobile ICT risks in line with Regulation (EU) 2022/2554, covering Articles 8, 9, 10, 24, and 25, through vulnerability assessments, security testing, and audit-ready evidence generation that financial institutions can present to regulators, auditors, and internal governance bodies.

|
By Rishika Mehrotra
Your mobile app ships as a compiled binary to millions of devices you do not control. Anyone can decompile it, extract hardcoded secrets, reverse-engineer the logic, and exploit business-logic flaws that no automated scanner catches. Yet most security programs still treat mobile as an afterthought, running a web-focused SAST tool against mobile source code and calling it done. That approach misses platform-specific risks.

|
By Rucha Wele
Frida hooks into your app's running process in seconds. It intercepts API calls, dumps the keychain, bypasses SSL pinning, and reveals exactly what the app does at runtime. Frida is also the tool attackers use to do the same things to your users. Runtime testing tells you what happens when an app runs under test conditions. It does not tell you whether the app can resist those same tools when an attacker uses them in production. That answer is not in the runtime session. It is in the binary.
|
By Appknox
In the rapidly evolving world of Fintech, trust, and security are of paramount importance. We have gathered an exceptional panel of industry experts who will delve into the challenges faced by Fintech companies in maintaining the trust of their customers and ensuring the security of their banking apps. Join our industry leaders comprising of Subho Halder Majorie Labindao Salinawati Salehuddin Md. Abul Kalam Azad,CISSP,CISA,CISM, CRISC.
|
By Appknox
It's #DataPrivacyWeek. Are you ready to build a secure organization and keep your data safe? Join Appknox's panel discussion with Subho Halder, Raghunath Thiyagarajan, Rajkumar P, and Vijayta Sharma
|
By Appknox
Through this webinar, we aim to help enterprises & individuals understand about cloud security and I-AM policy can play a role to build safe and secure mobile apps that garner trust. It will help you to prevent sensitive data loss and infrastructure exposure, resulting in fraud, reputation damage, and regulatory penalties.
|
By Appknox
About The Webinar: The cybersecurity landscape is constantly evolving, making it a challenge to stay ahead of attackers. They are always looking to exploit & gain access to control sensitive information. This can lead to serious consequences, such as ransomware attacks. This means integrating security as a core part of the development process is becoming even more essential by the day.
|
By Appknox
About The Webinar: Today’s cybersecurity threat landscape is highly challenging. Attackers are constantly on the lookout to exploit security vulnerabilities in applications and systems to gain access to or control sensitive information and launch cyberattacks such as ransomware. With companies spreading sensitive data across different platforms, software as a service (SaaS) platforms, containers, service providers, and even various cloud platforms, it’s essential that they begin to take a more proactive approach to security.
|
By Appknox
Join us in an exciting webinar by Appknox's CISO & Co-Founder, Subho Halder and Vaishali Nagori, Penetration Tester at Appknox on Payment Gateway Related Vulnerabilities. Know how Fortune 500 companies have created superior & secure payment gateways for their customers.
|
By Appknox
Launching a mobile enterprise application is no easy feat and one minor security breach can undo all your hard work in no time. With the right security platform, you can detect and fix security vulnerabilities without losing sleep. Say hello to Appknox, a plug-and-play security solution that secures your mobile enterprise applications in less than 60 minutes. Rated the highest in security products in Gartner and being a high performer on G2crowd for SAST, we set ourselves apart from our competition by allowing you to integrate your SDLC with all project management and CI-CD toolchain.
|
By Appknox
A security-first strategy is a competitive business advantage in today's world. Know how Fortune 500's have created superior and secure digital experiences for their customers.
|
By Appknox
Launching a mobile enterprise application is no easy feat and one minor security breach can undo all your hard work in no time. With the right security platform, you can detect and fix security vulnerabilities without losing sleep. Say hello to Appknox, a plug-and-play security solution that secures your mobile enterprise applications in less than 60 minutes. Rated the highest in security products in Gartner and being a high performer on G2crowd for SAST, we set ourselves apart from our competition by allowing you to integrate your SDLC with all project management and CI-CD toolchain.
|
By Appknox
Unlocking the Secrets of building a secure app Under 60 Minutes Build a culture of Secure Programming in your engineering team . With the amount of (attempted) security breaches and high paced sprint cycles, securing your mobile applications from day 1 is a driving force to ship applications at speed.
|
By Appknox
When you are looking for genuine, inexpensive unbiased information to make your application secure, there is no better source to go to than OWASP. OWASP gives you guidelines to the industry's top threats and security best practices that help ensure your applications are secured. Take a look at this FREE OWASP Guide that covers vulnerabilities from both web and mobile to give you a comprehensive overview of your application's security status.
|
By Appknox
Apple is known to employ slightly more stringent norms as compared to its other counterparts as far as Approving apps is concerned.
|
By Appknox
Detect and eliminate critical threats with the lowest visibility hiding behind the thickest of code. Protect your mobile apps and it's data from malicious attacks.
|
By Appknox
As SaaS businesses continue to evolve in a world of cut throat competition, key decision makers must ensure full accountability of their user's security. Sensitive and personal data should be monitored and kept secure along with innovation and strategic investments. Hence security for SaaS organisations is a critical component as a strategic driver for the growth of business.
|
By Appknox
When we make our way into the ecosystem of security technology and infrastructure initiative, learning about application security trends becomes of utmost importance. The unpredictable COVID-19 situation has made global businesses more vulnerable than ever to cyberattacks and breaches. Be it the Zoom data breach (500k records stolen) or the Marriott (5.2 million records breached), hackers don't seem to miss opportunities to exploit vulnerabilities and gain access to business infrastructures and public records.
|
By Appknox
In public-facing cloud environments with faster than ever deployment and delivery speeds, we need security models that can keep up with the pace. However, security still remains one of the most downplayed affairs in many organizations. While DevOps practices have helped organizations find means to build and react to the market faster, the hurdles of relying on traditional security are still making inroads for more and more threat incidents.
- October 2026 (5)
- September 2026 (1)
- August 2026 (1)
- July 2026 (1)
- June 2026 (8)
- May 2026 (2)
- April 2026 (4)
- March 2026 (5)
- February 2026 (2)
- January 2026 (3)
- December 2025 (10)
- November 2025 (3)
- October 2025 (2)
- September 2025 (6)
- August 2025 (7)
- July 2025 (5)
- June 2025 (6)
- April 2025 (3)
- March 2025 (3)
- February 2025 (6)
- January 2025 (2)
- December 2024 (2)
- November 2024 (1)
- October 2024 (4)
- September 2024 (3)
- August 2024 (1)
- July 2024 (4)
- June 2024 (3)
- May 2024 (1)
- April 2024 (2)
- March 2024 (2)
- February 2024 (1)
- January 2024 (5)
- December 2023 (2)
- November 2023 (1)
- October 2023 (1)
- August 2023 (6)
- July 2023 (2)
- June 2023 (6)
- May 2023 (7)
- April 2023 (2)
- March 2023 (7)
- February 2023 (5)
- January 2023 (6)
- December 2022 (2)
- November 2022 (4)
- October 2022 (2)
- September 2022 (3)
- August 2022 (8)
- July 2022 (5)
- June 2022 (10)
- May 2022 (5)
- April 2022 (4)
- March 2022 (2)
- February 2022 (8)
- January 2022 (7)
- December 2021 (6)
- November 2021 (3)
- October 2021 (4)
- September 2021 (3)
- August 2021 (8)
- July 2021 (2)
- June 2021 (8)
- May 2021 (2)
- April 2021 (7)
- March 2021 (7)
- February 2021 (3)
- January 2021 (4)
- December 2020 (3)
- October 2020 (1)
- July 2020 (1)
- April 2020 (5)
- March 2020 (1)
Appknox is the worlds most powerful plug and play security platform which helps Developers, Security Researchers and Enterprises to build a safe and secure mobile ecosystem using a system plus human approach to outsmart smartest hackers.
Our Products:
- Static Application Security Testing (SAST): With 36 different test cases, Appknox SAST can detect almost every vulnerability that’s lurking around by analyzing your source code. Our tests cover security compliances like OWASP Top 10, PCI-DSS, HIPAA and other commonly used security threat parameters.
- Dynamic Application Security Testing (DAST): Detect advanced vulnerabilities while your application is running. Appknox DAST simulates actual attacks on our test environment to analyze, detect and plug those pesky vulnerabilities that can fall prey to runtime and network attacks like MITM.
- Application Programming Interface (API) Testing: Quite different than SAST or DAST, Appknox's APIT tests the server-side of your application. Appknox API scan captures API's at requested endpoints and runs 15+ tests on each of these API's to detect vulnerabilities that may compromise the security of the app servers.
- Manual Application Security Testing (MAST): Nevertheless, the human mind is much sharper than a machine. Hence MAST in our security testing product that utilizes experienced security researchers to test vulnerabilities in your app.
- Remediation for Mobile Apps: Prioritize remediation with a research-driven security evaluation guided by OWASP security standards. Appknox remediation framework is designed to help development teams understand and remediate vulnerabilities without slowing down on SDLC.
Build and deploy world-class mobile apps for your organizations at scale and leave your mobile app security to us.