Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Proving the Value of Threat Intelligence in 2027: Metrics the Board Will Understand

Cyber attacks on UK retailers and manufacturers have shown boards that cyber risk is business risk. This blog explains why the whole organisation needs to understand the value of threat intelligence, and sets out the metrics that translate intelligence into language the board understands: money, time, exposure and reputation.
Threat Intelligence Demo: From Dark Web Monitoring to Action in Check Point Exposure Management

Threat intelligence only helps when your team can act on it. See how Check Point Exposure Management collects intelligence from the clear, deep, and dark web, adds telemetry from Check Point’s global firewall network, and ties it to what is exposed in your own environment.

Open Banking, Open Doors? API Abuse Through a Threat Intelligence Lens

Open banking drives financial innovation but introduces new cybersecurity risks through APIs, exposed credentials and third-party integrations. Discover how cyber threat intelligence helps financial institutions identify emerging threats, improve visibility and strengthen security.

What to Look for in a Threat Intelligence Tool

Most security teams aren't short of data. The harder problem is turning that data into intelligence they can act on. This guide sets out the seven criteria that separate an effective threat intelligence tool from another unused dashboard: dark web coverage, relevance, human analysis, speed, multi-audience outputs, integration and provider trust. It also covers the red flags to watch for during procurement and gives ten questions to ask every vendor.

Put Threat Intelligence to Work

Threat intelligence is easy to find. Turning it into a detection that works in your environment is harder. A new campaign surfaces. Research lands in an inbox, threat feed, or repository. Then the real work starts. Someone has to identify the behaviors worth detecting, find the right telemetry, map the right attributes, build the logic, validate it, and tune it for the environment. That work takes expertise. And in many SOCs, that expertise sits with a small number of detection engineers.

Open-Source Intelligence Tools for Security Teams

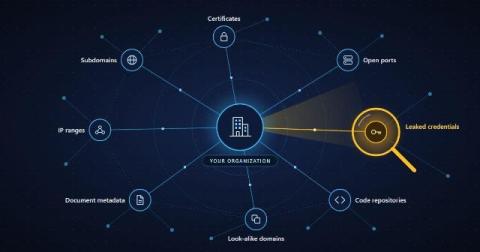
Attackers rarely start with an exploit. They start with a search: which subdomains a company runs, which staff email addresses sit in breach dumps, which forgotten server still answers on the internet. MITRE ATT&CK treats this stage as a tactic of its own, Reconnaissance, and most of it runs on public data.