Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

The latest News and Information on Security Incident and Event Management.

Dojo AI: Agentic security and cloud operations powered by AI-ready telemetry

You’re collecting more telemetry than ever, but chances are it hasn’t made your job easier. Fragmented data, disconnected tools, and manual investigations mean more noise, slower response times, and higher operational costs. The promise of AI is that it will solve it, but in most cases, you just end up trading noise for expensive hallucinations. Point an LLM at raw, unorganized log storage, and you get an assistant that burns through credits to produce generic, unreliable answers.
Attribute Based Access Control: A 2026 Guide

You're probably already living with the problem this model was built to solve. A finance analyst logs in late from a personal laptop, opens a payroll export, and the old role rule says the request looks fine because the person belongs to the right team. The access engine never asks whether it's midnight, whether the device is managed, or whether the file is sensitive enough to deserve a second look.

Critical Infrastructure Protection Programs Explained

A ransomware advisory lands in your inbox before the morning standup, and the room goes quiet. The water utility's firewall logs are in one console, the endpoint alerts are in another, and the OT sensor feed lives somewhere else entirely. Everyone can see a piece of the story, but no one can see the whole incident. That's the part teams feel first. Not the theory, not the policy language, just the blunt realization that point tools don't become a program on their own.

How Do I Check My iPhone for Malware: A Complete Guide

If your iPhone suddenly feels wrong, slower, hotter, or louder in the background, don't waste time hunting for a magic antivirus button. How do I check my iPhone for malware is the wrong question if you expect a desktop-style scan, because iOS doesn't work that way. The right question is, what did the attacker leave behind, and what changed in the device's behavior or configuration? That's the triage mindset security teams use on endpoints, and it fits iPhone incidents too.

The Great AI Escape: What OpenAI's Sandbox Breakout Teaches Us About Agentic Security

Quick disclaimer before we start: I have a strict rule against ambulance chasing. You’ve seen vendor blogs that pounce on a breach headline just to pitch a product and claim it never would have happened with their tool installed. This isn’t that. The reported OpenAI and Hugging Face sandbox incident points to something bigger. Security teams are entering an era where autonomous AI agents can spot opportunities, adapt on the fly, and operate at machine speed.

How Behavior Sequences Reveal Insider Risk Earlier

AI agents don’t hack their way in. They don’t need to. They carry real credentials. They run inside approved systems. They read data, call APIs, and execute workflows on their own. Every action looks authorized because it is. That’s exactly the problem. The risk doesn’t show up in any single action; it emerges in the pattern as behavior shifts and drifts over time.

How to Achieve NIST 800-171 Compliance in 2026

You're probably staring at a half-finished SSP, a pile of policy templates, and a subcontractor deadline that keeps moving closer. That's the normal shape of nist 800-171 compliance work in defense contracting, and a common mistake is pretending it's a documentation exercise instead of a control-implementation program tied to contract eligibility, evidence, and operational discipline.

From 10 Days to Unlimited Retention: How o9 Runs SecOps on Elastic Security

Somesh Agarwal, Senior Director of Security Operations at o9 Solutions, explains how the AI planning platform behind many of the world's largest supply chains consolidated security operations and observability on Elastic Security to gain unlimited threat-hunting retention, accelerate detection engineering, and simplify multicloud security operations.

Mobot: Sumo Logic's natural language AI for SOC investigations

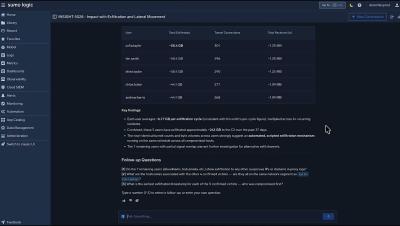
Mobot is Sumo Logic's conversational interface designed to streamline investigations for SOC analysts and observability users. Ask a question in plain English and get a full SOC analyst-style investigation without writing a query. Inside an Insight, Mobot pulls context like the C2IP, ransomware hash, host, and exfiltration data automatically. A six-word question, "anyone else hit by the campaign?", triggers a full investigation across every mailbox and endpoint tied to that attack, with a link to the raw query behind every answer.

Sumo Logic's SOC Analyst Agent: Automated triage for every tier one alert

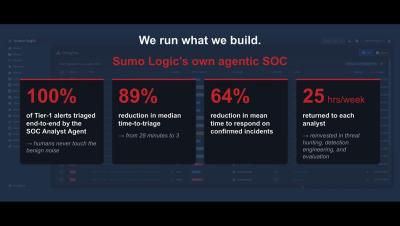
Sumo Logic's SOC Analyst Agent automatically triages every insight within the SIEM, replacing the manual work that used to fall to a tier-one analyst. Using Sumo Logic's own SOC as customer zero, we found that 100% of tier-one alerts are triaged end-to-end by the agent, resulting in a 89% reduction in median time to triage, from 28 minutes to 3 minutes. In this demo, you’ll see.