Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Why AI Red Teaming Belongs at the Core of Your AI Security Program

Enterprises are putting AI applications and agents to work on sensitive data and business workflows, while attackers look for new ways to manipulate the models and exploit the tools connected to them. Security leaders need to know whether those systems will hold up against a real attack, and AI red teaming gives them that answer by testing AI the way an attacker would.

The Azure Administration Skills That Support a Stronger Cloud Security Posture

Using Microsoft Azure securely is not the same as configuring it securely. Although the platform provides a protected foundation, an organization's cloud security posture still reflects routine administrative decisions made across subscriptions and resources. Most incidents are not signs that Azure itself failed. Instead, they often trace back to ordinary configuration choices made during day-to-day work.

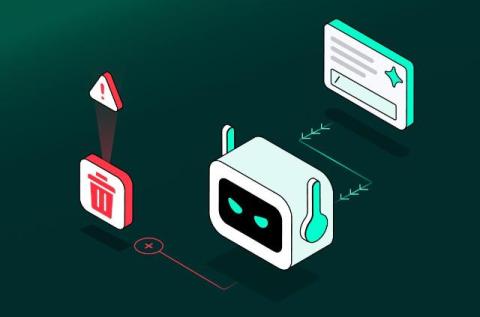
Stopping destructive commands in AI agents

An engineer gives a coding agent a routine task: clean up an old test deployment. The request sounds harmless, and the environment is cluttered with unused cloud resources, stale branches, and temporary credentials that should have been removed weeks ago. The agent gets to work. It lists resources, identifies old infrastructure, and finds a deployment command. Then it sees a naming pattern that appears to connect the test environment to production.

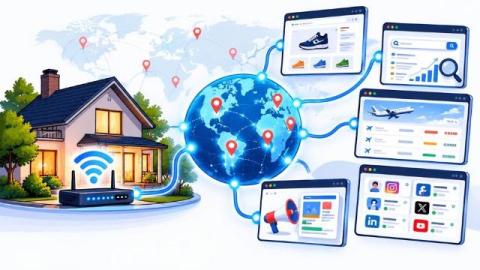
The 5 Top Uses for Residential Proxies

Residential proxies route your traffic through real IP addresses assigned by actual ISPs to actual homes. That's the whole distinction that matters. A datacenter proxy comes from a server farm and looks nothing like normal traffic. A residential IP looks exactly like someone browsing from their living room, because, well, technically it is. That's why websites trust residential traffic more and block it far less. For anyone doing data collection, research, or account management at any real scale, that trust gap is basically the whole reason this category exists.

Corelight in the Black Hat USA NOC: A playlist of attendee mistakes

When I got back from Black Hat USA, I was stunned. Of course, it’s easy to be overwhelmed by Black Hat. There is so much going on. Las Vegas casinos are loud and flashy. Going outdoors feels like standing on the surface of the sun. Everywhere you walk there are strong smells, and you hope it’s a delicious meal, but sometimes it’s not.

Hunting Citrix NetScaler zero-days with Corelight: Part 2

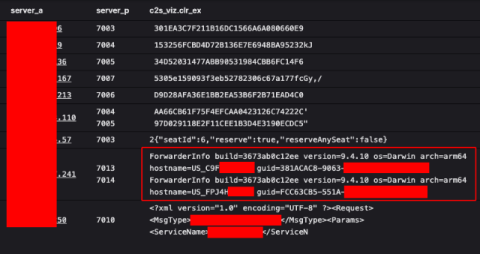
In Hunting Citrix NetScaler zero-days with Corelight, we explored how network evidence from Corelight’s Open Network Detection and Response (NDR) Platform can help identify candidate NetScaler appliances, observe DTLS use and hunt for suspicious activity.

Wait, Did We Just Invent Classifiers Again? Introducing Jev, a new way to do AI.

For the last few years, when somebody says “AI,” what they are usually referring to is a Large Language Model, or LLM for short. You chuck some text in, it has a think, and it gives you some more text back. This is brilliant if you want code written, documents summarised, or quantum physics explained to you in a limerick, but while this is great for humans, most software doesn’t actually want a beautifully written paragraph. Software just wants an answer so it can make a decision.

Beyond Model Access: Frontier AI Defense Needs Runtime Prevention

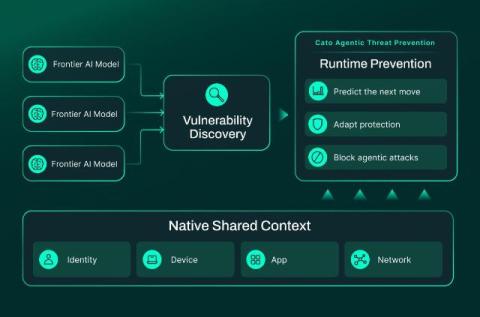
Access to powerful AI models is opening new possibilities for cybersecurity. Models can help uncover weaknesses, investigate threats, and explore how attackers might break into an environment. Using several models can bring different strengths to that work. But model access alone does not answer a critical question: can your defense stop an attack while it is happening? In the frontier AI era, discovery needs to connect to action.

Why a clean firewall policy isn't enough to secure your network

Your last firewall audit came back clean. Every rule documented, every exception justified, every box checked, exactly what PCI DSS and your other compliance frameworks and attestations require. None of that tells you whether a compromised laptop in marketing can actually reach your payment systems right now. The audit verifies your firewall policy. It was never built to verify your network.