
|
By Dr. Guy Waizel
On 21 October 2026, PHP released fixes for CVE-2026-109618 and CVE-2026-109619, a pair of critical runtime vulnerabilities known as PHP2Shell. One day later, we described how our self-evolving CVE mitigation agent turned the patch into reviewed IPS protection in minutes. This report follows what happened next, including how quickly attackers moved, what their attempts looked like, and how Cato’s cloud-delivered IPS protection blocked them on inspected customer traffic.
|
By Dr. Guy Waizel
Eight eMudhra intermediate certificate authority (CA) private keys were compromised after being generated with insufficient randomness. Attackers could use these keys to forge certificates and impersonate legitimate websites or services to clients that still trust them. An attacker able to intercept a connection could potentially read or modify sensitive traffic.
|
By Makiko Yamada
AI is becoming part of everyday work. Employees rely on services such as ChatGPT and Claude to research, create, and solve problems, while developers increasingly use AI-powered tools like Cursor and coding agents in their development workflows. As employees increasingly rely on AI to work more productively, the AI experience is becoming a critical part of the digital experience IT teams are expected to support.
|
By Amad Hussain
When an auditor or an RFP asks how your organization handles AI risk, the OWASP Top 10 lists are often a core part of the checklist behind the question. Cato AI Security is built to address the risks on two lists.
|
By Amad Hussain
AI used to live in a browser tab. Today it also runs inside the apps employees use every day, like Copilot in Word, in dedicated apps like ChatGPT and in coding agents such as Claude Code, Codex and Cursor. Coding agents work differently from chat apps. A chat app answers a question and waits. A coding agent is given tools and takes actions on its own, with the developer’s access. So every endpoint is becoming an agentic endpoint.
|
By Dr. Guy Waizel
CERT-FR’s October 13 update reports compromises of refrigeration controllers, naming Danfoss AK-SM and AK-SC alongside Copeland/Dixell XWEB systems. The entry methods remain unconfirmed. CERT-FR warns that attacks are probably continuing and recommends removing public exposure, checking configurations, and securing remote access. Compromised operational technology (OT) can disrupt cooling, compromise stored products, and threaten cold-chain continuity.
|
By Dr. Guy Waizel
On 21 October 2026, PHP released fixes for CVE-2026-109618 and CVE-2026-109619, two critical vulnerabilities known as PHP2Shell that can enable unauthenticated remote code execution. Cato’s self-evolving CVE mitigation agent helped turn the investigation into concrete research output by creating a proof of concept and generating an IPS signature in minutes. The agent connects vulnerability analysis, controlled lab testing and protection generation.
|
By Makiko Yamada
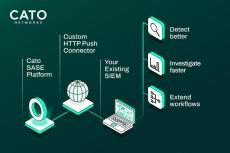
Effective security operations require more than isolated alerts. Analysts need context from across the environment to understand what happened, assess its significance, and decide what to do next. That is why accessing insights and telemetry from across your networking and security stack is critical to teams using a SIEM tool.
|
By Makiko Yamada
When a user says, “the application is slow,” IT has to answer a much harder question: where did the problem actually begin? The issue could be on the endpoint, local network, ISP, the network path, enterprise infrastructure, or application provider itself. That investigation often takes time because teams have to reproduce intermittent problems, collect evidence from separate tools, and hand cases between endpoint, network, and application owners.
|
By Amad Hussain
Many SD-WAN refreshes start with an expiring contract or edge equipment reaching end of life. But replacing the edge should not be the measure of success. For network and infrastructure leaders, the real test is what improves after the refresh. Will the refresh put IT on another appliance cycle, or move the WAN to a cloud service? Can IT keep critical applications performing consistently? Can the WAN respond when network conditions change?
|
By Cato Networks
Introducing our AI Security Innovation Update series with Liron Hakim Bobrov and Amad Hussain. Watch the first episode to see what's new from Cato, from agent guardrails to protecting the AI apps your teams are building.
|
By Cato Networks
When users report slow application performance, where do you start troubleshooting? The Wi-Fi, ISP, network, or application itself? With Cato Digital Experience Monitoring (DEM), IT teams can move beyond guesswork and identify the root cause of performance issues using evidence from across the user-to-application path. In this demo, a user reports slow Zoom performance at a branch location. Watch how Cato DEM Root Cause Analysis investigates the issue, examines latency, jitter, and packet loss, and identifies the branch wireless LAN as the source of the slowdown. See how Cato DEM helps IT teams.
|
By Cato Networks
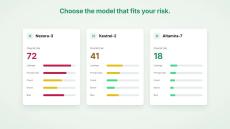
AI-powered applications depend on the models behind them, and those models keep changing. New attack techniques appear every day, model updates can change how safeguards behave, and switching models can leave existing protections behind. Security teams need to know where their AI is exposed before an attacker finds out first.
|
By Cato Networks
Local AI agents are becoming part of everyday work, accessing enterprise data, using tools, and completing tasks directly on employee devices. Security teams need to enable this adoption without losing visibility, control, or governance over agent actions - even when those actions happen locally.
|
By Cato Networks
As an SMB managed SASE business grows, the real challenge is often operational: how to add customers and respond to changing needs without adding licensing friction. Cato SMB FlexPool helps eligible MSPs and service providers managed committed capacity at the partner level, supporting faster growth, better utilization, and control of the managed service experience. Contact your Cato channel representative to discuss SMB FlexPool eligibility and pool sizing.
|
By Cato Networks
AI-powered attacks are moving faster, adapting in seconds, and overwhelming traditional defenses with machine-speed activity. In this video, Jason Wright explains why security teams need Agentic Threat Defense built on customized predictions, automatic adaptation, and cloud-native scale. Watch how Cato Agentic Threat Prevention helps reduce the risk of AI-powered threats, stop adaptive attacks earlier, and scale prevention to stop agentic attacks.
|
By Cato Networks
AI-powered adversaries are accelerating vulnerability discovery and automating attacks. For security teams, the challenge is adaptive attack chains, machine-speed execution, and attack volumes beyond manual workflows. Cato is redefining prevention in the AI era—predicting enterprise-specific attack paths, adapting protections at machine speed, and scaling defense with cloud-native scale. This means enterprises can do more than just react to attacks, they can prevent them.
|
By Cato Networks
Enterprise AI is spreading fast across employees, applications, and agents. Security teams need a way to enable AI adoption without losing visibility, control, or governance. In this demo, see how Cato helps organizations secure AI across three fronts: · AI employees use, including sanctioned and unsanctioned AI tools· AI applications teams build, including LLM apps connected to enterprise data· Agentic AI, where agents can access tools, data, and workflows.
|
By Cato Networks
See how Cato helps stop an Agent Tesla-style malware credential theft attack before it becomes business impact. In this demo, a remote finance user opens what appears to be a routine invoice. Behind that simple action is a common attack path: malware designed to steal credentials, keystrokes, and sensitive business data.
|
By Cato Networks
See how Cato Private Access helps organizations access the app, not the network. In this demo, we show how IT teams can deliver secure access to private applications without routing or firewall changes, while maintaining application-level access control, centralized policy enforcement, and visibility through the Cato Management Application. We also highlight how Cato manages private application access through the Cato SASE platform, enabling a more unified, operationally efficient approach than traditional connector-based architectures.
|
By Cato Networks
Organizations require an understanding of the positive ROI implications of security transformation with a holistic, cloud-delivered security architecture. A well-formed security transformation strategy provides an objective cost analysis of potential savings gained by retiring traditional security tools. Understanding how a single converged software stack provides both a financial ROI and a technical ROI will help organizations uncover hidden savings to be gained with their transformation projects.
|
By Cato Networks
When exploring a revolutionary architecture like SASE, it helps to have specific, relatable examples. SASE overlaps both networking and security spaces, sometimes making it difficult to see the whole picture. In this new eBook, we explore what SASE looks like for 5 different industry verticals: Retail & Hospitality, Manufacturing, Credit Unions, Health & Pharmaceuticals and Technology. Many of the benefits of SASE can provide value to any organization, so even if your specific vertical isn't covered, you should take a look!
|
By Cato Networks
While organizations realize they must deploy zero trust, knowing where to begin and how to deploy has become an impediment for many. The Cybersecurity and Infrastructure Agency (CISA) is one of several zero-trust maturity models that provide organizations with a measurable path to zero trust. The Cato SSE 360 architecture is a secure platform that helps facilitate Zero Trust maturity while delivering complete 360-degree protection for users, applications and data. This white paper will discuss how Cato SSE 360 can help facilitate Zero Trust Maturity.
|
By Cato Networks
Before SASE, network and network security services were delivered through multiple point solutions, including legacy appliances. These legacy appliances operated in silos and required countless IT resources and attention to deploy, manage, maintain, and replace. Today, some enterprises are still trapped using these legacy appliances, despite their shortcomings. In the parallel, modern world, SASE offers a single cloud-native network and security service for all networking and security needs.
|
By Cato Networks
Migrating a branch firewall to cloud? Pretty straightforward.... But enterprise security teams often find it challenging when contemplating moving the datacenter FW to the cloud. Unlike the branch firewall or UTM, the datacenter FW is responsible for providing visibility and control over inbound and outbound internet traffic, WAN traffic, vLAN traffic, and more. In this whitepaper, understand all the challenges that come with migrating your datacenter FW to the cloud, in addition to.
|
By Cato Networks
Your SSE project is right around the corner. Our helpful SSE RFP template allows you to meet both current and future security threats while ensuring that your key business objectives are met. Our template, divided into four sections, provides key questions to incorporate into your SSE RFP. This RFP template will allow you to easily identify.
- October 2026 (18)
- September 2026 (6)
- August 2026 (12)
- July 2026 (13)
- June 2026 (8)
- May 2026 (14)
- April 2026 (18)
- March 2026 (25)
- February 2026 (7)
- January 2026 (6)
- December 2025 (9)
- November 2025 (7)
- October 2025 (7)
- September 2025 (11)
- August 2025 (10)
- July 2025 (13)
- June 2025 (17)
- May 2025 (10)
- April 2025 (17)
- March 2025 (15)
- February 2025 (9)
- January 2025 (8)
- December 2024 (15)
- November 2024 (6)
- October 2024 (9)
- September 2024 (7)
- August 2024 (5)
- July 2024 (15)
- June 2024 (10)
- May 2024 (5)
- April 2024 (6)
- March 2024 (5)
- February 2024 (11)
- January 2024 (11)
- December 2023 (5)
- November 2023 (8)
- October 2023 (8)
- September 2023 (12)
- August 2023 (15)
- July 2023 (13)
- June 2023 (9)
- May 2023 (14)
- April 2023 (14)
- March 2023 (14)
Cato enables customers to gradually transform their networking and security infrastructure for the digital business. You can address one or more of the use cases below at your own pace. No matter where you start, Cato will support you throughout your journey.
Cato SASE Cloud with SSE 360 provides a global converged cloud-native service that securely and optimally connects all branches, datacenters, people, and clouds. Cato can be gradually deployed to replace or augment legacy network services and security point solutions.
Cato SASE Cloud:
- Converged: Cato converges SD-WAN and network security capabilities into a single pass architecture.
- Cloud-native: Cato is built from the ground up as an elastic, resilient, and scalable cloud service.
- Global: Cato is available across 75+ global PoPs to support any business location or user.
- All edges: Cato secures and optimizes traffic from all users, locations, clouds, and applications.
SASE, SSE, ZTNA, SD-WAN: Your journey, your way.