Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Gartner Names Torq as Company to Beat in AI SOC Agents for Threat Investigation in May 2026

See how Torq harnesses AI in your SOC to detect, prioritize, and respond to threats faster. Request a Demo The AI SOC category just got its definitive race assessment, and Torq is at the front. In the May 2026 Gartner report AI Vendor Race: Torq Is the Company to Beat in AI SOC Agents for Threat Investigation (Document ID: G00855833), Gartner names Torq the Company to Beat.
How Aurora Managed Endpoint Defense Combines Experts and Technology to Simplify Security

In this demo, Aurora Managed Endpoint Defense shows how human expertise and EDR work together to rapidly detect, investigate, and respond to threats; giving customers stronger protection, faster results, and improved security posture.

Building SecOps that improve with every frontier AI release

CEO Maxime Lamothe-Brassard made an observation after the RSA conference that security vendors don't typically say out loud: "The frontier models are just better than anything people roll their own. There's no secret sauce these vendors are offering that is better than the latest frontier model release." That's a pointed claim that carries a significant implication buyers may not have fully considered.

This CISO Admitted Their SOC Wasn't Really a SOC

When Klotz was brought in, she assessed Trinseo’s security operations and saw a reactive, single-time-zone model stretched across too many tools. Today, Trinseo runs a modern, 24/7 SOC anchored on CrowdStrike Falcon Complete Next-Gen MDR and the AI-native CrowdStrike Falcon cybersecurity platform.

Security Automation Doesn't Mean What It Used To: A 2026 Practitioner's Guide

Security automation used to mean building a playbook. Someone on the team mapped out a workflow, connected a few tools, and watched it run on the alert types it was designed for. That worked for a while, in a different environment than the one security teams operate in today.

The Blueprint for a True AI SOC

See how Torq harnesses AI in your SOC to detect, prioritize, and respond to threats faster. Request a Demo John White is the Field CISO for EMEA at Torq. A respected security executive with more than 20 years of leadership experience, John previously served as CISO at Virgin Atlantic, where he led a multi-year transformation deploying the Torq AI SOC Platform to modernize cyber operations.

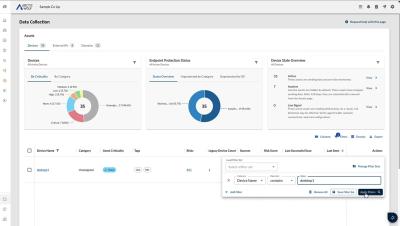
How Aurora Vulnerability Management Provides Asset Visibility, Risk Prioritization, and Remediation

In this demo, we will see how Aurora Vulnerability Management helps organizations discover and categorize assets, prioritize risks, and take action to remediate and patch vulnerabilities.

Agentic AI Security Guardrails: A Deployment Guide for SOC Leaders

See how Torq harnesses AI in your SOC to detect, prioritize, and respond to threats faster. Request a Demo Noam Cohen is a serial entrepreneur building seriously cool data and AI companies since 2018. Noam’s insights are informed by a unique combination of data, product, and AI expertise — with a background that includes winning the Israel Defense Prize for his work in leveraging data to predict terror attacks.

How Arctic Wolf Aurora Mobile Threat Defense Protects the Mobile Attack Surface

How Arctic Wolf Aurora Mobile Threat Defense secures the full mobile attack surface—devices, apps, networks, phishing, and privacy—in one unified platform. This demo highlights real‑time visibility, actionable insights, and automated response to reduce mobile risk.

Arctic Wolf: A Higher Standard

Powering modern security operations with AI is no longer optional. It’s essential. The Aurora Superintelligence Platform is built for the AI era, combining specialized AI agents, real-world security data, and human expertise to deliver outcomes security teams can trust. At its core, the Swarm of Experts, Security Operations Graph, and AI Trust Engine work together to drive faster detection, more accurate investigations, and more decisive response across the attack surface.