Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Immutable Ledgers: Recording Time-Sensitive Decisions and Knowledge

In a time when everything said, whether factual, fake, or AI-created, may be recorded and posted on the internet, it’s more important than ever to ensure that what was recorded accurately represents a point in time. When someone claims you said, “I was Smoking on a flight, watching Star Wars, the best special effects movie of all time,” was that a false claim? Did they include the date and the context?
The Secure Cloud-Native Journey: Development, Deployment, and Defense

David Hendri, Solvo’s CTO & Co-founder, and David Melamed, Jit’s CTO & Co-founder, discuss the shift from traditional software security to modern cloud environments. They cover how cloud visibility, automation, and vulnerability prioritization improve security without slowing developers and share insights on future trends, including AI’s impact on cloud security.

Focusing on the WHY: Jit Enables Developers to Understand the Runtime Context for Security Issues

While code and cloud security scanners are great at identifying code flaws and cloud misconfigurations, they can bombard developers with long lists of potential security “issues” – many of which don’t introduce real risk. Whether insecure code introduces real risk depends on a number of factors, like whether it is being deployed to production, is exposed to the internet, or calls a sensitive database.

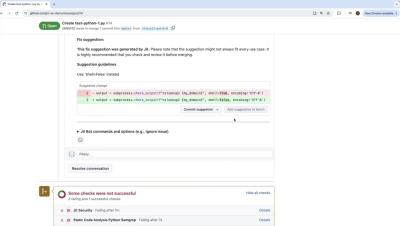
The Bug Stops Here: Using DevSecOps Workflows for Pest-Free Applications

Developers and cybersecurity have an interesting relationship. Developers have no problem with security operations just as long as they’re not involved or adding security doesn’t slow down their development cycle. Thankfully, well-documented security operations — known as DevSecOps — assist with the software development lifecycle (SDLC) and perform mostly invisibly from the developer’s perspective.

Building for the Future DevSecOps in the era of AI ML Model Development

Melissa McKay, JFrog Developer Advocate, and Sunil Bemarkar, AWS Sr. Partner Solutions Architect, discuss practical ways to mature your MLOps approach including bringing model use and development into your existing secure software supply chain and development processes. Watch to learn more and get a demo of the JFrog and Amazon SageMaker integration.

InCyber Forum Europe recap: 4 tips from DevSecOps experts

As your organization considers how to shift security left and facilitate shared responsibility for fixing issues, it can be tricky to know where to start. Which tooling will work best with your existing processes? What are the best ways to spread the word about the importance of application security? And once you’ve chosen tools, how do you actually get developers to use them?

Nucleus & Cycode Integration Delivers Unified Vulnerability Management and Application Security

As modern enterprise IT environments become more complex, the need for robust cybersecurity measures continues to grow. Because of this expanding complexity, DevSecOps functions are more common, requiring the integration of security into the application development lifecycle. Application Security Posture Management (ASPM) solutions offer a unified framework for securing the diverse application environment and merging security into the application development process.

#DevSecOps Essentials: Operating Confidently with Trusted Packages

Join JFrog’s Senior Solution Engineer, Mike Holland, and Technical Success Manager, Harpreet Singh, as they showcase the power of the JFrog Software Supply Chain platform. Designed to detect third-party components, track dependencies, and enforce compliance, this platform is essential for efficient and reliable software development. In this session, you'll learn.