Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

DevSecOps Tools for Cybersecurity Success

With DevSecOps, cybersecurity has become integrated into every phase of the software development lifecycle (SDLC). DevSecOps tools work across development, security, and operations siloes and enable these teams to work collaboratively, ensuring security vulnerabilities are addressed early and efficiently, reducing risks before they reach production.
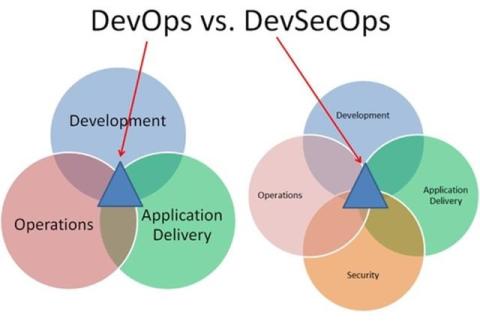
Why a solid DevOps foundation is vital for effective DevSecOps

As DevOps adoption has grown, organizations are pushing code into production faster than ever. However, the fast pace of DevOps has led many developers to view security as a bottleneck or afterthought, which means security teams need a new approach to keep up.

Jit Achieves AWS Security Competency: A Milestone in Developer-First Security Innovation

We’re thrilled to announce that Jit has achieved the AWS Security Competency, a significant milestone that underscores our commitment to revolutionizing product security for developers and security teams alike. This recognition from AWS validates our leadership in the security space and highlights the value we bring to organizations looking to embed automated security into their development workflows.

Breaking Down Jit's New Approach to ASPM

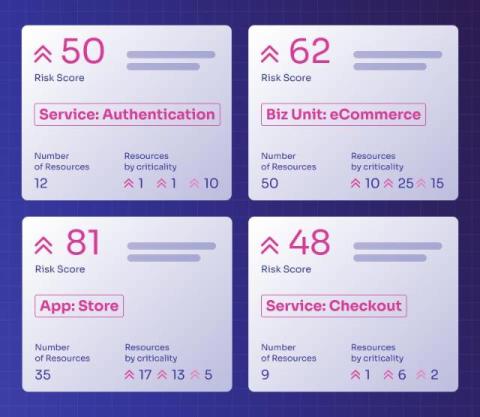
Application Security Posture Management (ASPM) emerged to address gaps in traditional application and cloud security scanners – like SAST, SCA, secrets detection, IaC scanning, CSPM, and many others – that generate noisy alerts and silo security insights across various tools. By providing a consolidated view of product security risks that are prioritized according to their business and runtime context, ASPM helps security teams understand which issues truly matter.