
|
By Steve Carter
Last month, the FBI arrested a suspect in its ongoing response to an attack on its job portal, allegedly carried out by criminal hacker and extortion group ShinyHunters. The agency said a contractor failed to apply a security patch to a third-party platform involved in the breach of its job portal, while Reuters reported that the contractor worked for Accenture and that the platform was Oracle PeopleSoft. (Fair warning: The Reuters article is behind a paywall.)
|
By Scott Kuffer
Enterprise security has a speed problem. Attackers are getting faster at finding and exploiting vulnerabilities, while many organizations still rely on ticket-based remediation, approvals, and scheduled maintenance windows. AI threatens to widen that gap considerably, exposing one of vulnerability management’s largest unchanged challenges: getting the right systems to fix the right problems before attackers exploit them.
|
By Ryan Cribelar
Last updated: October 22, 2026. This story is still developing, and we'll update this post as new details are confirmed. Two critical vulnerabilities in PHP, CVE-2026-109618 and CVE-2026-109619, are putting a large share of the web at risk. The vulnerabilities, collectively named PHP2Shell, both carry a CVSS score of 9.2, and both allow remote code execution (RCE). Security teams should treat these vulnerabilities urgently and respond accordingly.
|
By John Morton
The platform determines what is known. AI helps determine what it means. Technology solution providers across virtually every industry are racing to add AI, in some fashion, to their offerings. Vulnerability management providers aren’t immune, either. They’re racing just as fast as the rest of them, sometimes faster. These vendors are embedding copilots, assistants, and agents powered by technologies like Anthropic Claude, OpenAI GPT, and Google Gemini.
|
By Adam Dudley
The first Aviation ISAC summit, a little over a decade ago, was about forty people in a room in Miami, hosted by the Health ISAC. This year’s conference in Vancouver hosted more than five hundred: airlines, airports, OEMs, suppliers, and government, all in one place for three days. Many in the audience were new to the conference. One of the opening speakers asked first-timers to raise their hands, and a lot of hands went up around the room.
|
By Steve Carter
AI adoption is making everyone faster, including the attackers we as cybersecurity practitioners are competing with. While the attackers are getting faster thanks to AI, it’s not changing why most preventable breaches happen. That part is remaining consistent, for better or worse.
|
By Doug Drew
Anyone who has participated in a cybersecurity audit knows the drill and has likely asked the same question. “Is there a way to automate any of this?” When an auditor requests evidence that vulnerabilities are being identified, prioritized, remediated, and tracked according to policy, the automation question is a fair one.
|
By Rob Gibson
Every security team knows the feeling. The quarterly vulnerability scan completes. The report lands, with thousands of findings, color-coded by CVSS severity, neatly timestamped. And the moment it’s printed, it’s already out of date. That is the fundamental flaw at the heart of traditional exposure management: it is built around a point in time.
|
By Ryan Cribelar
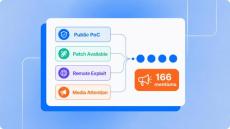
Nucleus Insights flagged 14 vulnerabilities with real-world exploitation activity that looked risky before CISA added them to KEV. The key takeaway: all 14 were later listed in KEV. Acting on those signals would have been the right call every time, just earlier.
|
By Scott Kuffer
Let me be direct about something the industry keeps dancing around: the vulnerability problem isn’t getting better. It’s getting structurally worse. The wave of AI-generated code and compression of time to exploit thanks to frontier AI models like Mythos is about to make “worse” look quaint. If your vulnerability and exposure management program is still built around scanner cycles, ticket queues, and CVSS scores, you’re not running a security program.
|
By Nucleus Security
BOD 26-04 changes how federal agencies and FedRAMP providers handle vulnerabilities. It moves away from severity-based, 30-day patching and toward risk-based prioritization. In this webinar, Bob Costello (former CIO of CISA, strategic advisor to Nucleus Security, and Chief Digital and Information Officer at The Merlin Group) and Scott Kuffer (Co-founder and CPO at Nucleus Security) explain what the directive requires, why CISA built it on the SSVC decision-tree framework, and how to put it into practice.
|
By Nucleus Security
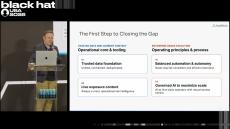
Everyone is talking about using AI to fight AI. But when it comes to vulnerability management, is that really the answer? In this presentation from Black Hat USA 2026, Nucleus Security Co-founder and Chief Product Officer Scott Kuffer challenges the industry's growing obsession with AI-first security outcomes and explains why organizations need more than autonomous agents, AI-generated prioritization, and endless vulnerability discovery to reduce risk.

|
By Nucleus Security
During our recent webinar, Co-founder and CPO Scott Kuffer explains how a text from an unexpected source brought home how AI and Claude Mythos have elevated the visibility of the vulnerability problem in the public sphere.

|
By Nucleus Security
In our recent webinar on how Claude Mythos will affect vulnerability and exposure management, guest speaker Jerry Hoff talks about what the ramifications are for discovering masses of new vulnerabilities in your environment.

|
By Nucleus Security
Artificial intelligence is transforming cybersecurity at an unprecedented pace, but is it making organizations safer or simply exposing more vulnerabilities?

|
By Nucleus Security
In this webinar, Nucleus Security CEO Steve Carter and Product Marketing Lead Tally Netzer break down the growing “exploitability intelligence gap” and what it means for modern vulnerability and exposure management programs. Drawing from six months of research and real-world vulnerability data, they explore how attacker timelines have compressed, why traditional reactive workflows are struggling to keep pace, and where organizations are missing critical signals before exploitation begins.

|
By Nucleus Security
AI is becoming table stakes in vulnerability and exposure management. In this candid webinar conversation, Chris Ray, Field CTO at GigaOm, and Will Gorman, CTO and leader of AI initiatives at Nucleus Security, challenge the assumption that more AI automatically leads to better outcomes.

|
By Nucleus Security
Nucleus R&D Engineer Ryan Cribelar assesses where internet exposure ranks amongst all of the factors involved when prioritizing vulnerabilities.

|
By Nucleus Security
R&D Engineer Ryan Cribelar explains how internet exposure is a factor in risk management related to vulnerabilities and exposures.

|
By Nucleus Security
Nucleus Security's Adam Dudley talks about the platform's place in a highly functioning CTEM approach during a joint webinar with Cycode and HackerOne.
|
By Nucleus
There are hundreds of statistics you could collect and monitor to use as guiding metrics, but that doesn't mean it's a good idea to do so. Learn the four most critical metrics to track in vulnerability management, and what they tell us about the health of your program.
|
By Nucleus
Many organizations are using outdated, highly inefficient, and time consuming VM processes that leave security personnel struggling to keep up. As the vulnerability landscape continues to evolve rapidly, the processes used to discover, track, and remediate them has failed to evolve with it.
|
By Nucleus
Vulnerability exploitation is involved in over half of breaches, making it a huge risk to organizations. And the problem only continues to balloon year over year... both in the speed at which attackers are capitalizing on exploited vulnerabilities, and in the way that technology and assets outgrow most organization's current vulnerability management programs. In this series, we're going to be breaking down how vulnerability management has grown and evolved over time, plus how to modernize your program using things like risk-based vulnerability management.
- November 2026 (2)
- October 2026 (4)
- September 2026 (4)
- August 2026 (5)
- July 2026 (6)
- June 2026 (4)
- May 2026 (4)
- April 2026 (3)
- March 2026 (5)
- February 2026 (7)
- January 2026 (4)
- December 2025 (7)
- November 2025 (4)
- October 2025 (4)
- September 2025 (8)
- August 2025 (10)
- July 2025 (5)
- June 2025 (5)
- May 2025 (5)
- April 2025 (2)
- March 2025 (7)
- February 2025 (3)
- January 2025 (3)
- December 2024 (4)
- November 2024 (5)
- October 2024 (7)
- September 2024 (4)
- August 2024 (8)
- July 2024 (4)
- June 2024 (3)
- May 2024 (2)
- April 2024 (5)
- March 2024 (2)
- February 2024 (6)
- January 2024 (4)
- December 2023 (3)
- November 2023 (5)
- October 2023 (5)
- September 2023 (1)
Nucleus is a Risk Based Vulnerability Management (RBVM) solution that automates vulnerability management processes and workflows, enabling organizations to mitigate vulnerabilities 10 times faster, using a fraction of the resources that it takes to perform these tasks today.
The only Risk-Based Vulnerability Management Platform purpose-built for the world’s most complex enterprises:
- Vulnerability Management: Mitigate vulnerabilities 10X faster, using a fraction of resources.
- Application Security: Accelerate AppSec to the Speed of Operations & ship secure code faster.
- Government: Ensure compliance and control access to data any way you choose.
- MSSPs: Manage all clients from a single platform with true multi-tenancy.
Unified Vulnerability Management.