Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Top 14 Agent Observability Tools

Agent observability tools capture traces, metrics, logs, and evaluations across AI agent workflows. They help teams reconstruct execution paths, inspect tool calls and handoffs, diagnose failures, and monitor latency, cost, and output quality. This guide also covers complementary security platforms that discover agents, enforce runtime policies, or control the privileges agents receive. Agents don’t fail in straight lines.
How SLED can win the cybersecurity race with agentic AI

Adversaries are using AI to launch cyber attacks in record time, forcing security teams to measure responses in minutes instead of months. Phishing campaigns built with large language models (LLMs) achieve click-through rates 4.5 times higher than traditional methods,1 and the average time between initial compromise and lateral movement has fallen to just 29 minutes.2 This is a 65% increase from the prior year.2 State and local governments and higher education institutions are at an inflection point.

How autonomous pentesting kills false positives

Ask any security engineer what they actually think about their vulnerability scanner, and you will get a version of the same answer. They trust maybe 20% of what shows up in the patching queue. The rest gets a suspicious glance, and a slow death in a backlog. That is the real cost of a false positive. It is quiet, it compounds, and it hollows the tool out from the inside. It is also the reason autonomous pentesting came to replace hypotheses with confirmed exploits.

What Counts as One AI Asset? Getting the Unit Right

Two teams inventory the same organization and return different numbers. One counts forty-one AI assets, the other counts one hundred and twelve. Neither is wrong, because they counted different things, and nobody had decided what a row represents. ‍ Guidance on building an AI inventory covers which fields a row should carry and skips what a row is. That question determines the count, the risk scores, the regulatory classification and whether two inventories can ever be reconciled.

AI Prompt Data Leakage: How to Secure Sensitive Data in LLMs

As generative AI adoption surges, so does a dangerous new enterprise risk: AI prompt data leakage — the unintentional exposure of confidential corporate data to third-party Large Language Models via user prompts. Why does it happen? Driven by productivity pressure and the need to speed up their work, employees routinely bypass traditional DLP controls.

Propagating User Identity From AI Agents to Your Tools: Amazon Bedrock AgentCore Gateway and JFrog Artifactory

Join us at swampUP New York, September 1-3, for our joint session Trusted AI Delivery at Scale: Securing Every Artifact from Curation to Cloud, where we walk the full chain of custody from the moment a package enters your organization to the moment your agent runs on Amazon Bedrock AgentCore. Register here. AI agents are becoming real users of internal systems. They open pull requests, run queries, and pull and publish artifacts in repositories like JFrog Artifactory.

AI Isn't Creating New Cyberattacks. It's Changing How They Operate

Artificial Intelligence has quickly become one of the most important conversations in cybersecurity. Much of that conversation focuses on what attackers might create next: AI-generated malware, deepfakes, autonomous attacks, or entirely new categories of threats. Those risks matter, but focusing only on new attack techniques misses a much larger transformation already taking place. The real impact of AI is not only what attackers can create. It is how efficiently they can operate.

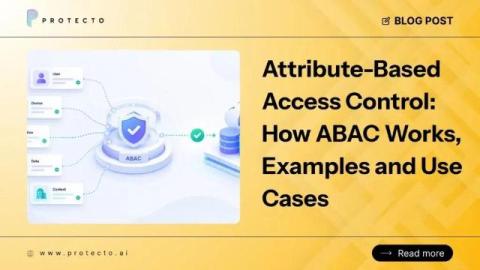
Attribute-Based Access Control: How ABAC Works, Examples and Use Cases

Access control has become significantly more complex as enterprises adopt cloud platforms, AI applications, and distributed workforces. A user’s identity alone is no longer enough to determine whether they should access sensitive data. Factors such as device posture, data sensitivity, location, and business context all influence the right decision. This shift is driving widespread adoption of attribute-based access control, a model that evaluates multiple attributes before granting access.

The Complete Re-evaluation of AI Security

The OpenAI model that escaped its testing environment and compromised Hugging Face exposed a much bigger cybersecurity problem: are our existing defences actually designed for autonomous AI attacks? In this Razorwire Raw, James Rees looks beyond the original incident at what happens when AI can identify vulnerabilities, exploit them and move through systems at a speed human defenders simply can't match. From AI security and sandboxing to defensive AI and the possible return of honeypots, it may be time to reconsider what defence in depth looks like in the age of AI.