Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Decommissioning AI Agents: What to Look For in the Tooling

Gartner predicted in mid-2025 that more than forty percent of agentic AI projects would be canceled by the end of 2027, citing escalating costs, unclear business value and inadequate risk controls. Treat the figure as a forward-looking estimate rather than a measurement, since canceled projects tend to be quietly renamed, absorbed or left to lapse rather than formally closed. ‍

Why Business Leaders Need a New Response Model to AI-Enabled Incidents

Originally published by Cybersecurity Insider. Over the past decade, cybersecurity threats have evolved from a technical issue into a key driver of business and operational risk. Artificial intelligence is accelerating that shift even further, changing the game once again. In 2026, AI in cybersecurity is multifaceted: a tool for defense and incident response, but also a powerful accelerator for attackers. AI-enabled incidents rarely stay contained within the security function.

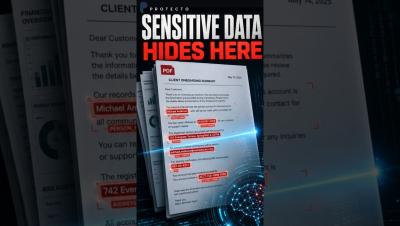
How NER Finds Sensitive Data Hidden in Documents #shorts

Sensitive data detection was much easier when information lived inside structured databases. Tables, columns, field names, and predictable data types gave security teams a clear map of where sensitive information lived. But when sensitive data moved into documents and PDFs, that map disappeared. Names, addresses, phone numbers, credit card numbers, and other sensitive information could be buried inside natural language.

Benchmaxxing: When the Benchmark Becomes the Target

Public benchmarks in AI provide important signals and allow for regression testing, directional validation of model updates, and public discussion of capabilities and limitations. But the more attention a benchmark receives, the stronger the incentive to optimize for it. Once a score becomes the goal, teams start benchmaxxing: optimizing for the benchmark rather than the capability it is meant to measure. This is a familiar problem in the AI space.

ChatGPT Security Risks for Enterprises: Real Incidents, Controls and Best Practices

Security teams often evaluate ChatGPT by examining its outputs. The greater risk, however, lies in the information employees submit before the model generates a single response. As generative AI becomes a big part of daily business operations, prompts increasingly contain confidential customer data, proprietary source code, legal documents, and strategic plans.

AI Governance in Financial Services: The Use Case Sets the Rules

An AI governance framework tells a financial institution to inventory its systems, assess risk and document decisions. Consumer protection law tells it something different and considerably harder, which is that a model unable to produce specific reasons for a credit denial cannot lawfully be used to make one. ‍ That distinction is what separates AI governance in financial services from AI governance generally.

Browser AI Events in the SOC: What to Send and What to Suppress

Browser-layer AI monitoring produces events, and the natural next step is forwarding them to the security operations center. Consider what they arrive into. Industry research for 2026 puts false positives at close to half of all alerts, with around forty-two percent going entirely uninvestigated. ‍ Browser AI events are behavioral anomaly alerts, and behavioral anomaly alerts are the category analysts already deprioritize, precisely because they are noisy by nature.