Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

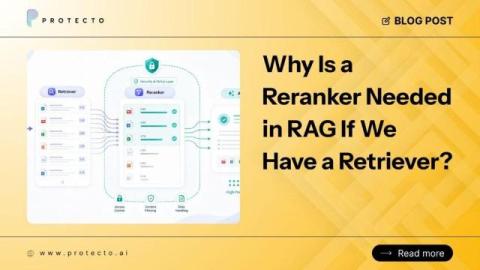
Why Is a Reranker Needed in RAG If We Have a Retriever?

Enterprise RAG pipelines have a recall stage and a precision stage. The retriever handles recall. The reranker handles precision. Skipping the reranker, or misplacing security controls around it, is where most accuracy and data exposure problems begin. The retriever’s job is to pull back every document that might be relevant. The reranker’s job is to find, from that candidate set, the documents that actually answer the question.

Report: AI Chatbots Are More Effective at Building Trust Than Human Scammers

A study has found that AI chatbots can be more effective at social engineering than human scammers, WIRED reports. The researchers looked at a form of romance scam commonly known as “pig butchering,” in which scammers spend weeks or months building a relationship with the victim before tricking them into sending money for a phony investment scheme.

Human Error Remains at the Core of AI-Enabled Social Engineering

AI is making social engineering attacks significantly more effective, according to a new report from cyber insurance firm Resilience. These attacks were behind more than 85% of losses in the first half of 2026, compared to less than 20% during H1 2024. “Losses tied to phishing, social engineering, and transfer fraud have climbed from 17.7% of incurred losses in H1 2024 to 85.3% in H1 2026, the single largest increase in the report’s five half-year comparison,” Resilience says.

Why Self-Healing Is the Only Way to Secure at Frontier AI Speed

For twenty years, the software security playbook has worked the same way. You find the vulnerability, score it, open a ticket, assign it to a human, wait for the fix, ship the patch, and prove it happened. Every step in that sequence assumes humans can review each fix individually and still keep up. Frontier AI broke that assumption. The exploit window has collapsed from weeks to hours. Attackers reason across your codebase, chain their findings, and ship exploits before a CVE is even published.

Agent Immunization: A New Model for Building Trusted AI Agents

The riskiest thing an AI agent does all day isn’t writing code. It’s shopping. Every few minutes, it reaches out for a package, an AI asset, or a tool, and pulls it in with no real way to check what’s inside. We think the fix is agent immunization: security that lives inside what an agent consumes, builds, and ships, not a wall built around it.

How Aikido finds more vulnerabilities than Claude Security at half the cost

Claude Mythos is arguably the strongest cybersecurity model that Anthropic has built. But we know that model capability is only part of what determines how well an AI vulnerability product performs. To test that, we put Anthropic’s Claude Security, which runs on Mythos, and Aikido Code Security Audit head-to-head on the exact same target to see which harness can deliver the best coverage and at what cost. Code Security Audit is part of Aikido’s AI Code Analysis suite.

What OpenTelemetry Can Actually Tell You About Your AI Agents

‍ The distance between what OpenTelemetry was built for and what AI governance is asking of it shows up in a single number. Distributed tracing descends from Dapper, the 2010 Google paper that gave the industry the vocabulary of traces and spans. Dapper sampled one trace in 1,024. That is ample for finding a latency regression, because a regression recurs and the next sample catches it.

AI Supply Chain Security: Why an SBOM Cannot Cover It

A software bill of materials works because software changes through a build. Someone bumps a dependency, the pipeline runs, the manifest updates and a scanner compares the new list against known vulnerabilities. Every part of that loop assumes a rebuild is the thing that changes behavior. ‍ AI systems break that assumption at the point it matters most. Editing a system prompt changes what a model does, swaps no dependency, triggers no build and produces no new manifest.

From AI Findings to Action: How Security Teams Should Triage AI-Discovered Vulnerabilities

Security teams didn’t need a headline to tell them that vulnerability volumes continue to be problematic. The CVE database now contains over 354,000 records. Annual disclosure rates have climbed steadily for more than a decade. And remediation backlogs have long been recognized not as an aberration, but as a fixture of the job.