
|
By Cyberhaven
A data loss prevention (DLP) team writes a rule to keep customer records out of ChatGPT. The rule catches an uploaded spreadsheet but misses the same records pasted into a prompt, because no file transfer occurred. The team adds text pattern matching to close the gap, and the rule starts flagging harmless prompts that happen to contain a name and a number. Both failures share one cause. The rule judges what the text looks like and cannot see where it came from.
|
By Franklin Nguyen
“Threat Actors Combine Automated and Hands-on Hacking Tools to Steal Sensitive Data.” Security teams read headlines like this every week. When they learn about new threats from sources like CISA Cybersecurity Alerts & Advisories, each one prompts a check on whether current tools cover it. And as these new threat vectors get published, some expose gaps that existing tools can’t cover. Teams respond by searching for products to address these risks.
|
By Gauri Manglik
A well-written AI policy is where governance starts. It gets legal, security, and the business aligned on how much risk the organization is willing to accept, and nothing else in the program works without it. Every AI policy ultimately exists to protect the data held by the organization. In today’s world, data held in information systems is the crown jewel of most organizations but the same data can put the organization at risk if it leaks, gets stolen, or is mishandled.
|
By Volodymyr Kuznetsov
At Cyberhaven, we replaced our previous LLM-based approach to document understanding with a small model that makes 83% fewer decision errors at less than 1% of the inference cost. We achieved this by breaking complex tasks into simpler decisions, using uncertainty as a training signal, and heavily optimizing our inference stack. The model produces calibrated decision probabilities while preserving multimodal understanding and generative capabilities.
|
By Franklin Nguyen
An AI support agent picks up a customer case, signs in with valid credentials, works on it in only approved systems, and closes it. I would reasonably predict that if someone were to review this workflow, it would likely come back clean, with no policy rule violation. But if we were to take a closer look, we might find that the agent did more than just close the case.
|
By Cyberhaven
Security teams built their controls around people, applications, devices, and networks. AI agents operate across all four at once. An agent can pull records from Salesforce, combine them with financial data, summarize the result with a language model, and post it to Slack, with no person touching any step. Each action may look permitted on its own, which means the risk sits in the sequence, and most tools can’t see the sequence.
|
By Bruce Chen
Data loss prevention (DLP) has been around for decades. But the way data moves today looks very different from the environment traditional DLP was built to protect. That change comes through clearly in the new Market Overview for Data Loss Prevention by Gartner. We see that Gartner describes a mature market undergoing significant evolution, with cybersecurity leaders increasingly looking for DLP that is adaptive, policy-driven, risk-based and AI-enhanced.
|
By Bruce Chen
An AI agent produces a recommendation that looks reasonable. It's accurate. The model didn't hallucinate. Can the organization trust it? That depends on questions the output can't answer: Enterprise trust requires knowing where information came from, how it moved, what happened to it, and whether the process behind the result deserves confidence. Provenance is where that trust starts.
|
By Cyberhaven
Every audit season, a governance, risk, and compliance (GRC) team pulls access reports, screenshots configurations, and reconstructs months of data handling from whatever logs survived. The package passes the audit, but the evidence is stale a week later.
|
By Nishant Doshi
Data lineage is fast becoming one of the most important ways to understand data exfiltration, for both human and agentic workflows. More and more vendors now market data lineage, each claiming their approach is superior. That makes us proud parents: what was once an esoteric technology is finally going mainstream. Cyberhaven pioneered data lineage in data security and has spent years perfecting it.
|
By Cyberhaven
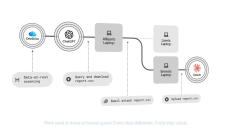
Agentic workflows move sensitive data through systems that most security tools never see. This walkthrough follows one workflow from start to finish. A user shares customer data with an agent, the agent calls Model Context Protocol (MCP) servers to enrich its analysis, and the combined dataset is saved locally and shared through email, web upload, and USB. The video runs the workflow once without protection, then runs the same workflow again with Cyberhaven in place.
|
By Cyberhaven
he video outlines how Cyberhaven's Data Security Posture Management (DSPM) provides a continuously updated, context-aware inventory of data at rest.
|
By Cyberhaven
AI changed work, Cyberhaven protects it. Cyberhaven exists to protect the way enterprises actually work today: with AI agents accessing, moving, and acting on data across every workflow. In this video, we share Cyberhaven's mission and our stance on data security for the agentic enterprise.Traditional data security, built for files at rest, wasn't built for AI agents acting at machine speed. Cyberhaven traces data through its full lifecycle and adapts protection as context changes, so security keeps pace with how work actually happens.
|
By Cyberhaven
Turn every analyst into a power user. Security investigations shouldn't take 45 minutes of tab-switching and manual querying. In this 20-minute walkthrough, Cyberhaven Director of Product Management Dave Stuart demos the Analyst Plugin, and shows how a single conversation replaces the queue.
|
By Cyberhaven
In this video, you will learn the five questions every data leak investigation must answer to be defensible — what the data is, where it originated, who accessed it, where it spread, and the fastest containment step — and why the visibility gap in most security stacks makes those questions impossible to answer instantly. You will also learn how combining DSPM baseline inventory with real-time data lineage replaces the high-stress scramble with surgical containment and audit-ready proof, so you move from "I think we're safe" to "here is the proof.".
|
By Cyberhaven
In this video, you will learn why locking down source systems like your CRM, HR database, and S3 buckets leaves your real risk surface exposed, how one regulated file fragments into CSV exports, screenshots, scripts, and AI prompts that shed their security context at every hop, and why both legacy DLP and traditional DSPM fail to act on these invisible derivatives. You will also learn how lineage-focused DSPM tracks the provenance of the data payload itself — every copy, paste, and save — so you can enforce policy on fragments instead of guessing from patterns.
|
By Cyberhaven
Autonomous AI agents are running on enterprise endpoints right now, accessing files, processing sensitive data, and executing actions outside the visibility of most security programs. This is Part 1 of Cyberhaven's four-part AI Security product launch series. What this video covers: Most AI security tools were built for browsers and SaaS apps. They cannot see agents operating at the OS level, coding assistants running in IDEs and CLIs, or MCP servers executing in the background. Cyberhaven's AI Security platform was built to close that gap.
|
By Cyberhaven
Security teams cannot govern what they cannot see. This is Part 2 of Cyberhaven's four-part AI Security product launch series, focused on Shadow AI Discovery and how Cyberhaven automatically inventories every AI app and agent running across your organization.
|
By Cyberhaven
Visibility without enforcement is just an alert backlog. This is Part 4 of Cyberhaven's four-part AI Security product launch series, covering how Cyberhaven enforces risk-based controls at the data level, not the tool level, using Data Lineage as the foundation.
|
By Cyberhaven
Knowing an AI tool exists is not the same as knowing what it did with your data. This is Part 3 of Cyberhaven's 4-part AI Security product launch series, covering Agentic AI Visibility and AI Risk IQ, Cyberhaven's evidence-based risk scoring system for every AI app and agent in your environment.
|
By Cyberhaven
Dive into our expertly curated DLP program checklist that will align with your organization's ambitious business and catapult them forward.
|
By Cyberhaven
In this guide we demystify DLP to distill the basics of DLP program development. Learn the essentials required to create scalable data security and data protection programs.
|
By Cyberhaven
Data is leaving your company in ways that didn't exist years ago-AirDrop, generative AI, and more. Legacy DLP hasn't kept up; now it's time to invest in more forward-looking solutions.
|
By Cyberhaven
DDR makes it possible to stop data exfiltration across all channels with one product and one set of policies.
- October 2026 (15)
- September 2026 (10)
- August 2026 (10)
- July 2026 (21)
- June 2026 (25)
- May 2026 (29)
- April 2026 (14)
- March 2026 (11)
- February 2026 (9)
- January 2026 (11)
- December 2025 (10)
- November 2025 (6)
- October 2025 (3)
- September 2025 (6)
- August 2025 (7)
- July 2025 (10)
- June 2025 (1)
- April 2025 (8)
- March 2025 (6)
- February 2025 (2)
- January 2025 (2)
- November 2024 (1)
- October 2024 (1)
- September 2024 (5)
- August 2024 (3)
- July 2024 (3)
- June 2024 (2)
- May 2024 (1)
- April 2024 (1)
- March 2024 (2)
- February 2024 (2)
- January 2024 (2)
- November 2023 (1)
- April 2023 (1)
Cyberhaven detects and stops the most critical insider risks to your most important data.
Let’s face it, data security products never lived up to our expectations and now that the way we work is changing they can’t keep up. Cyberhaven solves these challenges so companies can finally protect their data.
Data Detection and Response:
- Understand how data flows: See what systems store different types of data and how data moves within the company to new places and people.
- Stop data exfiltration anywhere: Block important data from leaving your control via cloud, web, email, removable storage, Bluetooth/AirDrop, and more.
- Accelerate internal investigations: Quickly understand an incident to determine user intent with a complete record of events before and during an incident.
- Detect and stop risky behavior: Instantly detect when a user handles important data in a risky way, stop them in real time, and coach them.
Trace your data to protect it like never before.