Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

What are the 5 pillars of Zero Trust? [Quick Question Ep. 4]

What are the five pillars of Zero Trust? Across Zero Trust frameworks, five control points remain consistent: users, devices, networks, applications, and data. In this episode of Quick Question, we cover how each pillar generates critical security data, and why that data often lives in disconnected tools, leaving organizations with a fragmented view.
What is Zero Trust Architecture? Why is it important? [Quick Question Ep. 3]

What is Zero Trust Architecture, and why is it important? Zero Trust is a security framework built on one core principle: never trust, always verify. In this episode of Quick Question, we explain how Zero Trust shifts security from protecting the front door to locking everything inside by default, granting access room by room based on identity, context, and authorization.

Zero Trust for AI Agents: Enforcing Anthropic's Framework

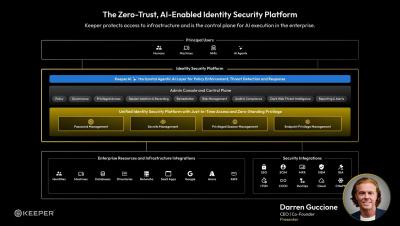
AI has changed how work gets done. Agents can plan tasks, query enterprise repositories, invoke tools, write code, call application programming interfaces (APIs), and take actions across connected systems. As they work, they create, copy, fragment, transform, and share data across workflows. A perimeter and a one-time authorization decision do not provide enough control for this operating model. An agent can chain permissions, tools, integrations, and data sources while completing a task.

Why Critical Infrastructure Needs Zero-Trust Security

Malicious cyber activity targeted remote monitoring and control technology at over 30 community water systems across Minnesota in late July 2026, and water cyber attacks were subsequently reported across at least 12 states. However, the underlying OT security weaknesses are not exclusive to the water sector.

Adopting & Implementing Zero Trust: Moving from Concept to Execution

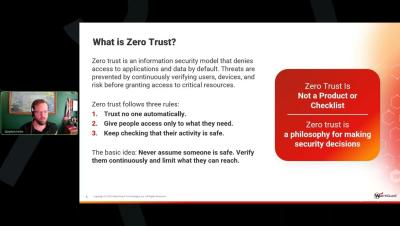
Zero Trust is often summarized as “never trust, always verify.” More precisely, it is a security model built on the premise that trust should never be granted implicitly based on where a user, device, workload, or resource sits. That makes Zero Trust much bigger than deploying a particular product or turning on a handful of access policies.

Kubernetes Zero Trust: Principles and How to Apply Them

Kubernetes trusts everything inside the cluster by default. Any pod can reach any other pod, IPs change with every rolling deployment, and one compromised container gives an attacker a path across your entire environment. Kubernetes zero trust replaces that default with a simple rule: Never trust, always verify, regardless of where a request comes from.

Future-Proof Your Network with Zero Trust

A stolen password should not open the front door to your entire network. Traditional VPNs were built for a different era. Once a user gets in, too much of the network often becomes reachable. That broad, implicit trust gives ransomware exactly what it needs: an entry point, a path to move, and room to spread.