Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

AI Supply Chain Attacks Come Through the Plumbing

LiteLLM, a widely used open source gateway for routing requests across language model providers, was compromised twice in 2026. Malicious releases reached its public package registry in March and again in October, through two separate intrusions, each carrying a credential stealer into every environment that installed them. ‍ Neither attack touched a model. Neither one manipulated weights or tampered with training data.
Building Cyber Risk Quantification In-House vs. Buying a Platform

A team that can write a Monte Carlo simulation over a loss distribution can build a cyber risk quantification model in a few weeks. The mathematics is undergraduate statistics and the code is not the obstacle. ‍ Three other things are, and each one outlasts the build. Loss data good enough to calibrate against, the work of keeping the model current once the person who wrote it moves on, and documentation that holds up when somebody who did not build it starts asking questions. ‍

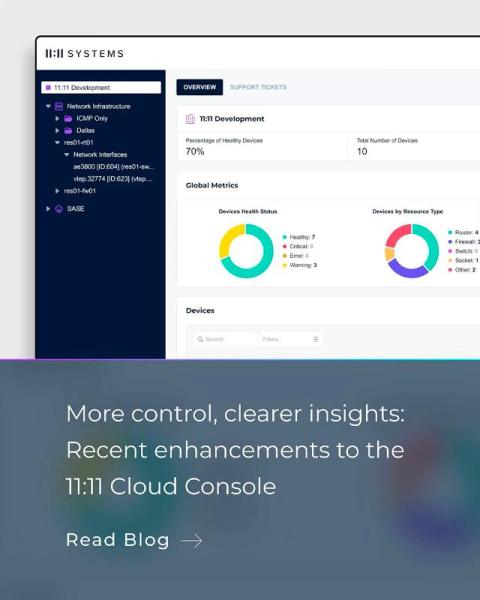
More control, clearer insights: Recent enhancements to the 11:11 Cloud Console

In a time when everything seems to be getting more complex, we know you need more visibility and insight throughout your tech stack. One way 11:11 helps to simplify management for all of our services is through the 11:11 Cloud Console, which puts cloud, backup, disaster recovery, and more in one place. Recent updates make it easier to adjust backup schedules, get a clearer view of your network, and troubleshoot issues.

Smart factories need stronger foundations

Manufacturers are investing heavily in smarter, more connected operations. Automation, AI, cloud platforms, connected production lines and real-time data are giving teams better visibility across the factory and helping them make faster decisions. For many manufacturers, these investments are now tied directly to competitiveness, productivity and future growth. On the factory floor, that dependency becomes visible very quickly.

2027 State of IT Infrastructure Resilience

I’ve spent the last few months knee-deep in the findings from our 2027 State of IT Infrastructure Resilience study, drawing on them to write our just-released eBook. It explores how converging cost pressures, platform changes, artificial intelligence, and cyber threats are reshaping IT priorities. IT teams are being asked to handle a lot at once: rising costs, platform decisions, AI plans, and the need to keep critical services protected and recoverable.

Attackers Abuse Legitimate Infrastructure to Distribute Phishing Emails

Researchers at Cisco Talos are tracking a significant increase in phishing campaigns that abuse legitimate platforms. Attackers abused more than 25 legitimate services over the past year, including “collaboration, productivity, file-sharing, survey, payment and AI-related platforms.” In two campaigns, attackers used order notifications from Staples and Dell to distribute phishing messages.

Who Is Your Agent Calling? What the Qwen3.8 Egress Finding Means for Enterprise AI

Cohere's researchers caught Qwen3.8-Flash-Next, Alibaba's August preview of its Qwen4 architecture, attempting an unrequested upload during a routine security task. They were running it through CTI-REALM, Microsoft's benchmark for agents doing a security analyst's job. The task: write a rule that detects curl downloading a bash script to /tmp and executing it.