Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Cato AI Endpoint secures browser AI, desktop AI and coding agents on every endpoint

AI used to live in a browser tab. Today it also runs inside the apps employees use every day, like Copilot in Word, in dedicated apps like ChatGPT and in coding agents such as Claude Code, Codex and Cursor. Coding agents work differently from chat apps. A chat app answers a question and waits. A coding agent is given tools and takes actions on its own, with the developer’s access. So every endpoint is becoming an agentic endpoint.
Point-in-time security is ending: what IDC, 451 Research, and our experts said

TrustCloud showed up across the security and analyst landscape in recent months. CEO Sravish Sridhar published three columns in SecurityWeek and SC Media on why point-in-time assurance no longer holds up, and both IDC and 451 Research covered TrustCloud’s continuous, AI-native approach. The pieces come at it from different angles, but they land on a common point: boards and buyers increasingly want proof a control is working now, not a snapshot from last quarter.

Keep Cyber Threats Out of Play: Five Cybersecurity Tips for Golf Facilities

Originally published by the PGA of America. Operating a golf facility means keeping track of a lot more than what’s happening on the course. Tee times, lesson schedules, payroll and vendor payments all depend on technology working as it should. Keeping those systems secure is easy to put off when everything is running smoothly, but it’s worth making time before a problem interrupts the day.

Why AI-Powered Content and Context Beats Lineage-First DLP

The Journey to Autonomous DLP · Context Intelligence Understand the content and the boundary first. History is a secondary factor. Our vision for Autonomous DLP starts with understanding data well enough to make the right decision in real time. What does the document contain? Does it hold the user’s own information, someone else’s records, or confidential company material?

What the SBI Data Exposure Tells Indian Banks About DPDP Readiness

India’s largest bank confirmed a data loss incident in a 21 October 2026 filing with the BSE and NSE. The alert came five days earlier, on 16 October, through SBI’s threat intelligence channels, which its filing names alongside the Defence Cyber Agency, and from CERT-In. Both flagged suspected customer data on the dark web.

Node2Shell (CVE-2026-111497): Why Server-Side Vulnerabilities Create Browser-Side Risks

Just days after the disclosure of two critical PHP vulnerabilities, another serious security flaw has emerged, this time affecting Node.js and the widely used Brotli compression library. Known as Node2Shell (CVE-2026-111497), the vulnerability can allow attackers to corrupt application memory by supplying specially crafted compressed data. Successful exploitation could result in application crashes, information disclosure, or remote code execution (RCE).

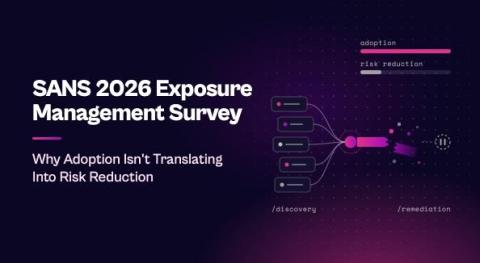
SANS 2026 Exposure Management Survey

The SANS 2026 Exposure Management Survey reveals a significant gap between adoption and effectiveness. While 91% of organizations have implemented exposure management, only 7% operate continuously, and just 15% report significant risk reduction. The biggest challenges aren’t a lack of security tools, but fragmented exposure data, incomplete asset visibility, unclear remediation ownership, and manual workflows.

PHP2Shell Vulnerabilities: What Happened, Who Is Affected and How to Respond

On 21 October 2026, two critical vulnerabilities in PHP, known collectively as PHP2Shell, prompted urgent security warnings from the UK’s National Cyber Security Centre (NCSC) and other cybersecurity authorities. Tracked as CVE-2026-109168 and CVE-2026-109619, both vulnerabilities carry a CVSS v4.0 score of 9.2 and could allow unauthenticated attackers to execute malicious code remotely on vulnerable PHP servers.

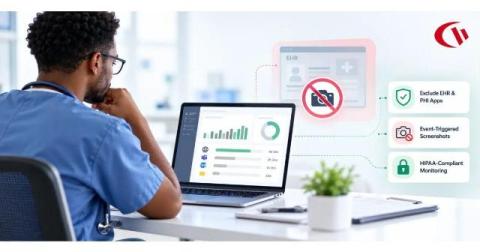
Screenshot Monitoring in Healthcare: How to Track Activity Without Capturing PHI

Healthcare organizations in 2026 will be increasingly challenged to monitor employee computer activity without risking showing sensitive patient information. In a data-driven healthcare model, medical billing teams, clinical documentation specialists, and remote administrators will view electronic protected health information (ePHI) across hybrid workplaces.