Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

FedRAMP Class B vs Class C: Which Should You Pursue?

In the past, FedRAMP has used impact levels as a sort of classification system for cloud services that wish to work with the government in some capacity. The impact levels evaluate a cloud service provider (CSP) based on the sort of information they would be handling and the service they would provide to the government. They are classified across three axes: confidentiality, integrity, and availability.
How Much Does An MSP Cost? A Real Breakdown Of Outsourced IT Support Costs

When you are comparing managed service providers (MSPs), a monthly price per user is a useful starting point, but it rarely tells the whole story. If you take for example, a standard SME business with 25 employees, they could be charged anywhere between £9000-45,000 per year for outsourced IT support, before a single extra is added. That’s the varied range most MSPs will quote for per-user fees and on its own, tells you less than it seems to.

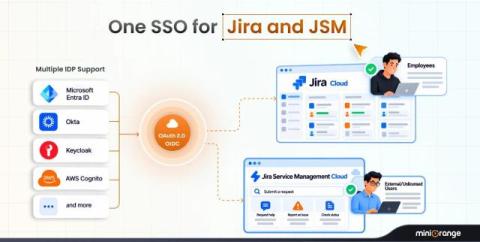
Why OAuth SSO Matters for Both Jira Cloud and Jira Service Management

Jira is rarely used by just one type of user. Primarily, teams use Jira Cloud for project management. At the same time, support teams work inside Jira Service Management (JSM), while internal employees and external users such as customers, vendors, and partners may access the JSM portal. They are all accessing the same Atlassian ecosystem, but they do not necessarily log in the same way. This is where organizations can run into a problem.

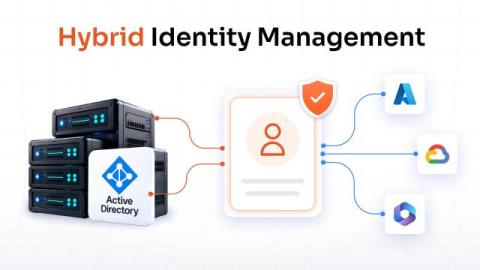
Hybrid Identity Management: Secure Access Across Cloud and On-Premises

Hybrid identity management is the practice of managing user identities and access across on-premises and cloud environments through a connected identity framework. Most organizations today operate across both. Active Directory may still manage identities for internal applications, while cloud platforms and SaaS applications handle other parts of the business. This creates a simple challenge: how do you give users consistent access when their applications and identities exist in different environments?

Not All Lineage Is the Same

Data lineage is fast becoming one of the most important ways to understand data exfiltration, for both human and agentic workflows. More and more vendors now market data lineage, each claiming their approach is superior. That makes us proud parents: what was once an esoteric technology is finally going mainstream. Cyberhaven pioneered data lineage in data security and has spent years perfecting it.

Hunting Citrix NetScaler zero-days with Corelight: Part 2

In Hunting Citrix NetScaler zero-days with Corelight, we explored how network evidence from Corelight’s Open Network Detection and Response (NDR) Platform can help identify candidate NetScaler appliances, observe DTLS use and hunt for suspicious activity.

Beyond the vault: Zero standing privilege defeats more than password attacks

Part 2 of 3 in our Rethinking Privileged Access series. Start with Part 1: The password was never the only problem. In Part 1, we drew the line between the vault-and-checkout model of legacy PAM and the session-and-Activities model of modern PAM with Netwrix Privilege Secure (NPS). One protects the password; the other eliminates the standing privilege behind it. That framing is a good starting point, but it understates the case. In Windows and Active Directory, the password is just the seed.