Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Automate Vulnerability Reporting for Auditors Without Creating More Work

Anyone who has participated in a cybersecurity audit knows the drill and has likely asked the same question. “Is there a way to automate any of this?” When an auditor requests evidence that vulnerabilities are being identified, prioritized, remediated, and tracked according to policy, the automation question is a fair one.
Agentic AI-Assisted Penetration Testing: AI Scale. Human Precision

When Mythos launched, headlines warning of its potential dangers were prolific. For security risk leaders, it felt like a watershed moment, one that signaled that AI had arrived, but simultaneously raised widespread concern about risk. Many wanted to understand how real the risk was for their organization and what should be done about it.

What CVE-2026-20079 Means for Every Network Team

On September 9, Cisco confirmed what earlier warning signs had already hinted at: a security flaw in its Secure Firewall Management Center (Secure FMC) software, the tool that configures and controls Cisco firewalls across a network, is being actively exploited. The flaw, tracked as CVE-2026-20079, received a maximum severity score of 10.0 on the CVSS scale, the industry-standard scale used to rate how serious a vulnerability is.

Your Vulnerability Backlog Is No Longer Technical Debt, It's an Attack Surface

Every security program has one: a queue of a few thousand findings, or a few hundred thousand, that nobody has worked through and nobody expects to. Most teams file it under technical debt, a cost carried on purpose, paid down when there is room, and tolerable because the interest rate stays low. That accounting held for a long time, because it rested on a single assumption: almost nothing in the queue would ever be reached, or exploited, by anyone.

Why Carbon Data Needs the Same Controls as Financial Records

Most security teams know exactly where their financial records live, who can edit them and how every change gets logged. Ask the same questions about the company's emissions data and the answers often get vague. That gap matters more each year. Greenhouse gas figures now end up in regulatory filings, investor reports and assurance reviews, which means they carry the same risks as any other disclosed number.

A UX Firm in Delaware and Designing for Fintech: Two Different Briefs

The short version Two searches show up in the same procurement folder. One looks for a UX firm Delaware founders can meet without a flight. The other looks for a team that has already shipped a regulated financial product. Those searches answer different questions, and the second one is harder to fake.

The Great Infrastructure Reset: Infrastructure Conversations Have Changed

Infrastructure conversations have changed. Today, customers are balancing rising infrastructure costs, licensing renewals, and the need for greater cyber resilience all at the same time. We’re calling this The Great Infrastructure Reset: a shift in infrastructure strategy driven by market forces that customers can’t ignore. For our partners, this creates an opportunity to lead with strategic conversations. Help customers understand what’s changing, what it means for their business, and how to build an infrastructure strategy for what’s next.

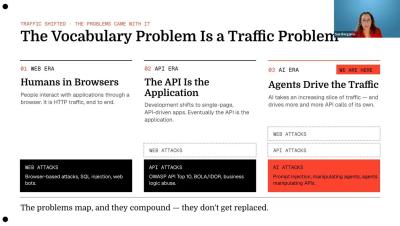
WAF vs WAAP API vs AI What Security Tools Do You Actually Need?

A straightforward framework for matching each layer of protection to the problem it actually solves. Trying to understand vendors in the modern application security space can feel a lot like trying to solve word scramble. Whether it’s remembering what the “A’s” in "WAAP” stand for, figuring out if “WAF” includes APIs, or assessing the actual function of a new AI security product, understanding what tools your team actually needs is getting harder all the time.

MDM vs. MAM: Which Mobile Management Option Fits Your Business?

Every IT team managing a mobile workforce eventually hits the same fork in the road: do you manage the whole device, or just the apps that matter? That question sits at the heart of the MDM vs. MAM debate. Getting the answer wrong can mean either locking down employee phones so tightly that people revolt, or leaving corporate data exposed on devices you barely control. Mobile Device Management (MDM) and Mobile Application Management (MAM) solve overlapping problems in very different ways.