Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Meeting the NIST AI RMF Measure Function With Monitoring Evidence

Measure carries four categories and twenty-two subcategories, and they divide cleanly by what kind of evidence satisfies them. Some ask whether something was observed. Others ask whether something was tested. Monitoring answers the first group and contributes almost nothing to the second.
Cyber Risk Quantification Integrations With GRC Platforms

Quantification integrated with a governance platform and quantification sitting beside one behave nothing alike after the first quarter. The integrated figure moves when control status moves. The standalone figure describes the date somebody last updated it. ‍ Two directions of data traffic make the difference, and most implementations build only the first one. ‍

Governing Microsoft 365 Copilot in the Enterprise

Microsoft states the position plainly. Copilot only surfaces organizational data to which individual users have at least view permissions, so it grants nobody access to anything they could not already open. What changes is that material somebody had permission to reach and never would have found now arrives in a summary. ‍ The governance work is therefore permissions work that predates the deployment.

Why Employee Morale Matters for Vendor Cyber Risk | UpGuard

Most cyber incidents trace back to people, so a vendor’s employee engagement can say a lot about its security. Brian Mackerer of Craft.co explains why procurement teams are starting to look at cyber risk alongside other signals, like employee engagement and financial stability, instead of relying on a cyber score alone. Discover more at upguard.com.

Automating Third-Party Contractor Risk in Regulated Facilities

Third-party contractors are one of the largest unmonitored compliance gaps inside regulated facilities. While internal employees go through rigorous background checks, recurring safety training, and strict access provisioning, external technicians and vendors often bypass those controls at the front desk. When an HVAC technician, specialized equipment calibrator, or electrical contractor walks onto a regulated floor with an expired certification, the host facility absorbs the regulatory and financial liability.

PHP2Shell vs. Log4j: Understanding the Risk and Exposure | Bitsight Webinar

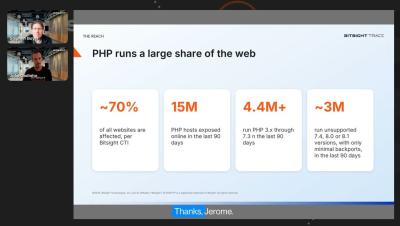
Could PHP2Shell become the next Log4j-scale cybersecurity threat? Newly disclosed critical PHP vulnerabilities are raising concerns about widespread exposure across enterprise environments and third-party supply chains. In this webinar, Bitsight cybersecurity experts examine the potential impact of PHP2Shell, share findings from Bitsight's latest exposure research, and explain how security teams can identify vulnerable assets, assess third-party risk, and prioritize remediation.

PHP2Shell Critical RCE Flaws: Exploited Within Hours of Disclosure

Last updated: October 22, 2026. This story is still developing, and we'll update this post as new details are confirmed. Two critical vulnerabilities in PHP, CVE-2026-109618 and CVE-2026-109619, are putting a large share of the web at risk. The vulnerabilities, collectively named PHP2Shell, both carry a CVSS score of 9.2, and both allow remote code execution (RCE). Security teams should treat these vulnerabilities urgently and respond accordingly.

CVE-2026-109618 and CVE-2026-109619 (PHP2Shell): Two Critical PHP Remote Code Execution Flaws

The PHP security team has announced an emergency security release for Wednesday, October 21, 2026 at 14:00 UTC. It addresses two critical vulnerabilities, both rated CVSS v4.0 9.2. The vulnerabilities are tracked as CVE-2026-109618 and CVE-2026-109619. Both bugs are described as remote code execution issues, meaning an attacker could get their own commands running on a vulnerable server. The route to disclosure was messy.

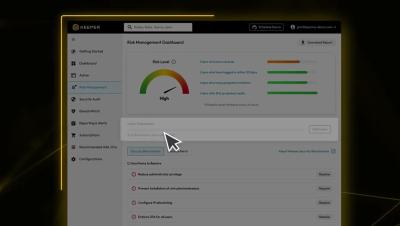
Enforcing the highest level of security in your environment with Keeper's Risk Management Dashboard

The Keeper Risk Management Dashboard is a powerful feature of the Keeper Admin Console that provides comprehensive security posture information covering end-user deployment, utilization, cloud configuration, and event monitoring. This critical data helps administrators ensure that risks are remediated and compliance is enforced effectively. The Risk Management Dashboard monitors key metrics and leverages Keeper Security's Benchmarks to enforce the highest level of security in your environment across all users and devices.

Cyber Risk Quantification Vendor Evaluation Checklist

Buying a cyber risk quantification platform means asking a vendor to defend numbers that will end up in front of a board, an auditor, or a regulator. Most evaluation calls never press that hard. The questions below are the ones that separate platforms from each other, and they are written so that any vendor can answer them, including vendors who would beat Kovrr on several of the answers.