Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

FBI Winter SHIELD's Cybersecurity Controls Are Worth a Second Look

AI adoption is making everyone faster, including the attackers we as cybersecurity practitioners are competing with. While the attackers are getting faster thanks to AI, it’s not changing why most preventable breaches happen. That part is remaining consistent, for better or worse.
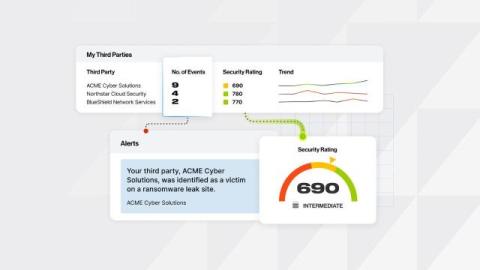
Know What's Actually Happening to Your Suppliers, Not Just When Their Names Show Up in Threat Data

A vendor can pass every questionnaire you send it and still be the reason you end up in a breach report. That's the gap most third-party risk programs live in today. According to the 2026 Verizon Data Breach Investigations Report, 48% of breaches now involve a third party, up from 30% the year before and 15% the year before that. But most organizations still manage that risk with periodic assessments and separate threat feeds. Those methods can tell you whether a supplier passed a review last quarter.

AI Agents Were Never Outside the Definition

The word agent appears nowhere in the AI Act. Some read that absence as a scope question still to be settled, and treat agentic deployments as sitting outside a regime written before they existed. ‍ On its own FAQ the Commission has answered it directly. Agents are not a separate category and the existing definitions already reach them, so nothing needs amending for the rules to apply.

The Cyber Outage That Ends Before the Recovery Does

An interruption model measures the time from failure to restoration. Systems down, systems back, multiply by revenue per hour. ‍ In an airline the outage ends well before the recovery does, and the ratio between the two is large enough to make a model keyed to restoration wrong rather than imprecise. One carrier restored connectivity in under an hour and the resulting displacement ran into the following morning. ‍

Which AI Signals Carry a Finding and Which Only Size It

A correlation rule joins several telemetry sources and fires when they agree. Guidance on writing them concentrates on thresholds, ordering and tuning for noise. ‍ The decision that determines whether a rule works is upstream of all of that. Each source in a rule plays one of three roles, and treating them interchangeably is what produces a rule that misses real events or fires on ones nobody can act on. ‍

The Cyber Loss Where the Stolen Records Belong to Other Companies

A breach response begins with a record count and a notification assessment. How many individuals, in which jurisdictions, under which statute. ‍ Some organizations hold almost no personal data and enormous quantities of other companies' commercial confidences. An insurer's claims files contain policyholders' loss histories, control failures and settlement amounts. The statutory machinery may not engage at all, and what engages instead is a contract portfolio. ‍

A Strategic Framework for Third-Party App Risk Management

Third-party code now accounts for 66% of the most dangerous, long-lived vulnerabilities across application portfolios, according to Veracode’s 2026 State of Software Security Report. For AppSec and engineering leaders, that stat tells a familiar story: shrinking release cycles, expanding open-source dependency footprints, and mounting regulatory pressure.

Is AI Helping Attackers or Defenders More? Cybersecurity Leaders Weigh In UpGuard

The barrier to entry for cybercrime is dropping fast. SPOILER: AI has a whole lot to do with it. Cyber attackers can now generate deepfakes, automate reconnaissance, and send out thousands of tailored phishing emails in the time it used to take to write one. Defenders are fighting back with AI of their own, catching threats earlier and shrinking the window attackers have to work with. Where do you land? Comment for attackers or for defenders and tell us why.

Cyber Loss When the Company Is Someone Else's Fourth Party

Third-party risk content is written from the customer's side. Assess your provider, tier your vendors, understand your concentration. ‍ A technology provider is on the other end of every one of those assessments, and its own incident propagates outward through contract rather than inward through remediation. The instinct is that the contracts therefore determine the loss. They determine the smaller half of it. ‍