Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Cyber Loss When the Inventory Itself Perishes

An outage is normally modeled as deferred revenue. Production stops, orders wait, operations resume and some of the backlog is recovered by running longer. ‍ Where the inventory perishes, none of that applies. The stock is destroyed during the incident, restoring the systems does not bring it back, and running longer afterward produces new product rather than recovering the old. ‍
The AI Marking Deadline That Applies Only to Systems Already Running

Transitional relief normally works one way. A new rule arrives, existing products are carved out or given years, and anything built afterwards complies from the start. ‍ The marking obligation for synthetic content inverts that. Article 50 has applied since 2 August 2026, and a targeted transitional period gives extra time to systems that were already on the market rather than to new ones.

Reading AI Use From the Browser When the Network Sees Nothing

A session to a sanctioned AI provider looks the same on the network whichever account it ran under and whatever was in it. Transport encryption means a proxy sees a connection to an approved domain and a payload size. ‍ Which is fine until somebody asks whether an exposure is reportable. The question turns on three facts the network never held, and none of them can be reconstructed from a log afterward. ‍

Cyber Loss in Rail and Signalling

Cyber risk in transport is usually framed around a collision. Signals manipulated, a train sent onto occupied track, an accident caused deliberately. ‍ Signalling is built to make that outcome unavailable. Any failure forces the system into its most restrictive state, so a compromise produces a halt rather than a crash. The loss is the halt, and rail is unusual in already having a published price for one. ‍

Cyber Loss When the Stolen Asset Is a Trained Model

A trained model is expensive to produce, cheap to copy and impossible to recall. Where one is taken, the organization still holds it, and the loss is not that the asset is gone. ‍ What ends is exclusivity. Lost exclusivity is a different quantity from a destroyed asset, it carries no notification obligation, it appears in no breach cost dataset, and most estimates therefore put it at zero by omission rather than by judgment. ‍

How to Evaluate and Choose the Best TPRM Software in 2026

Evaluating third-party risk management (TPRM) software in 2026? Every platform says it tracks your vendors. What a demo will not show you is whether it finds those vendors on its own, including the AI tools and shadow IT nobody logged, or waits for you to type them in. This video follows one vendor from the day it shows up in your environment through five criteria for judging any TPRM platform, and the question to ask a vendor on each one.

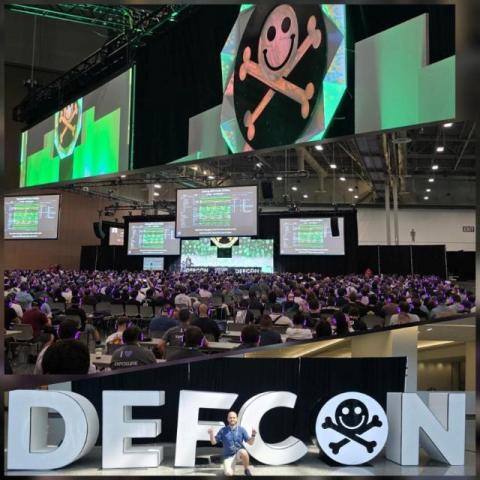
DEF CON 34: Lessons Beyond the Conference

Being part of the cybersecurity community means more than simply following the news or reading security research. It is about getting involved, having conversations, sharing experiences, discussing problems, and learning from peers who face similar operational challenges. Of course, all of this comes with an investment of time, energy, and a full day of travel to reach one of the world’s largest hacking conferences: DEF CON in Las Vegas.

The Cyber Risk Inputs That Move the Answer Most

A cyber loss model has dozens of inputs and every one of them can be argued about. Record counts, downtime costs, control effectiveness, secondary loss factors, event likelihoods. ‍ A few of them determine the answer and the rest barely move it. Knowing which is which tells you where estimation effort belongs, and more usefully which disagreements about the model are not worth having. ‍

Reconciling an AI Risk Estimate Against What Truly Happened

A model produces a figure, an event happens, and somebody asks whether the figure was right. It is the obvious question and it has almost no published answer, because the comparison is harder than it looks. ‍ A single realized loss cannot falsify a distribution. If a model puts a one percent chance on exceeding a threshold and the threshold is exceeded, the one percent case occurred, which is what the model said would sometimes happen. ‍

A Practical Guide to Enterprise IT Risk Assessment

Enterprise IT environments now span cloud platforms, SaaS applications, endpoints, third-party services, and AI tools, creating more opportunities for disruption, security incidents, and operational failure. IBM’s Cost of a Data Breach Report 2026 puts the global average cost of a data breach at $4.99 million, while Verizon’s 2026 Data Breach Investigations Report found that 31% of breaches started with vulnerability exploitation and 48% involved a third party.