
Mountain View, CA, USA
2012
  |  By Abi Tyas Tunggal
Every quarter, your board asks the same question, just phrased differently: Are we more secure than we were last time? A point-in-time assessment can't answer it, because it shows where you stood on the day someone ran it, not which way things are moving. Security posture monitoring is the correct response to give to the board. This guide answers the three questions behind every board pack: what goes in front of the board, where the number comes from, and how you show it moved.
  |  By Lance Turner
Mistaking a lack of alerts for a lack of threats is a dangerous assumption. But in the world of dark web exposure, silence is rarely a sign of safety; it’s a blind spot. Relying on external alerts to discover your vulnerabilities means you are reacting far too late. Here are five questions you should answer that turn that assumption into something you can measure. If you answer "no" or "not sure," treat it as a blind spot that a dark web scan will address.
  |  By Lance Turner
Most attack surface management (ASM) evaluations start with a name already on the table: a vendor from a G2 grid, an analyst shortlist, an inbound email, or a renewal conversation. Before you commit to a proof of concept (POC), you need to know how it compares. This page provides a capability matrix across 10 ASM vendors, followed by an honest section on each. UpGuard makes one of the platforms on this list, so every section, ours included, covers where the product isn't the right fit.
  |  By Cassy van Eeden
UpGuard Vendor Risk was built around the idea that third-party risk management (TPRM) works better when continuous risk intelligence and full lifecycle workflow execution live in the same system. That commitment has earned recognition from one of the most respected analyst firms in the industry. The IDC MarketScape model assesses vendors on both current capabilities and future strategies.
  |  By Lance Turner
Most brand protection solutions rely on one assumption: scam activity happens on the open web. Security teams focus on catching fake domains, social profiles, marketplace listings, paste sites, and dark web forums. While that covers a lot of ground, it leaves out a major risk: the official app stores.
  |  By Lance Turner
Most people don't hesitate to run a free security scan because they doubt it'll find anything. They hesitate because they don't know what the results will look like. Will it be 40 pages of raw data without context? A sales pitch disguised as a report? We'll walk through it screen by screen so you know exactly what to expect before entering a domain.
  |  By Cassy van Eeden
Analyzing vendor evidence is a massive undertaking, which is why more third-party risk management (TPRM) tools now offer AI capabilities that let teams upload evidence and get a faster read on a security assessment. When these capabilities come up in a vendor evaluation, the conversation almost always narrows to one question: how accurate are the AI results? A tool can answer every individual question correctly and still leave you exposed.
  |  By Lance Turner
Apple's 2025 App Store Transparency Report states that the company blocked over $2.2 billion in fraudulent transactions and removed roughly 59,000 apps for bait-and-switch tactics: publishing one thing to gain approval, then swapping in something else once the app goes live. The year before, fraud accounted for 38,315 of Apple's 82,509 total app removals, roughly 46%, making it the second-largest removal category that year. Google's numbers point in the same direction.
  |  By Lance Turner
Security leaders who already use the NIST Cybersecurity Framework often assume it covers AI, but it doesn't. The Cybersecurity Framework (CSF) protects the confidentiality, integrity, and availability of the systems around a model. Outcome risk from model decisions is a different job.
  |  By Lance Turner
Most security stacks still find out about stolen credentials the hard way: when an attacker logs in with them. Sometimes the first warning sign is a customer complaint or a call from law enforcement. Dark web monitoring services for business close that gap by watching underground sources for any exposure tied to your domains, employees, code, and brand, so you can reset access before someone else gets there first.
  |  By UpGuard
The shadow AI user is notoriously hard to observe. This elusive creature hunts in incognito tabs and leaves almost no trace on the approved tools list. In this episode of Cyber Risk in the Wild, a looming deadline draws one employee into the open, and the pride’s AI policy is put to the test. UpGuard User Risk uncovers the shadow AI and unsanctioned SaaS your teams are using, blocks risky uploads and pastes in the browser, and redirects people to approved AI tools in the moment.
  |  By UpGuard
The shadow AI user is notoriously hard to observe. This elusive creature hunts in incognito tabs and leaves almost no trace on the approved tools list. In this rare footage, a looming deadline draws one employee into the open, and an unapproved AI tool is only a few keystrokes away. Even the stealthiest hunter can be stopped, though. UpGuard User Risk uncovers shadow AI across your workforce and redirects people to approved tools in the moment.
  |  By UpGuard
How many red flags does your security program have? UpGuard CPO Daniel Bradbury calls out a few big ones we’re seeing right now, from banning ChatGPT to reporting a single security score to the board. If any of them hit close to home, the next UpGuard Summit is where we’re showing you how to turn those red flags green. It’s our free virtual event for security leaders, GRC practitioners and IT teams, and every session is recorded if you can’t make it live.
  |  By UpGuard
Most cyber incidents trace back to people, so a vendor’s employee engagement can say a lot about its security. Brian Mackerer of Craft.co explains why procurement teams are starting to look at cyber risk alongside other signals, like employee engagement and financial stability, instead of relying on a cyber score alone. Discover more at upguard.com.
  |  By UpGuard
We found more than 16,000 Supabase databases sitting wide open, and over half held personal data like names, phone numbers and passwords. The organizations behind them ranged from a valet service to a government consulate, and in many cases the owners never checked the settings AI wrote. What is the Supabase data exposure? Anyone visiting these sites could read the data in their databases. Many belong to vibe-coded apps, where AI coding tools often handle the database setup.
  |  By UpGuard
The barrier to entry for cybercrime is dropping fast. SPOILER: AI has a whole lot to do with it. Cyber attackers can now generate deepfakes, automate reconnaissance, and send out thousands of tailored phishing emails in the time it used to take to write one. Defenders are fighting back with AI of their own, catching threats earlier and shrinking the window attackers have to work with. Where do you land? Comment for attackers or for defenders and tell us why.
  |  By UpGuard
Would you bet your next audit on an AI summary you can't trace back to the evidence? See what good AI should actually deliver for TPRM teams: check-level depth, full citations, and a decision trail that holds up under review. Want to learn more? Check out our Interested in finding out more about UpGuard?
  |  By UpGuard
62% of security leaders can't tell their board whether they're actually getting safer. See how Threat Posture turns thousands of external signals into one board-ready narrative, with the evidence trail attached. Want to learn more? Check out our Interested in finding out more about UpGuard?
  |  By UpGuard
One customer expected 20 approved apps. User Risk found over 80 running underneath. See how the new Action Center turns that discovery into a prioritized list your team can act on. Want to learn more? Check out our Interested in finding out more about UpGuard?
  |  By UpGuard
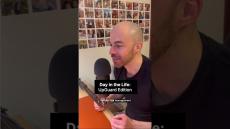
Ed Kost, Content Strategist at UpGuard, gave us a day in the life. Turns out there's a lot more to a cybersecurity content strategist than vendor risk management. We hire talented people and let them be themselves, which is how you end up with someone like Ed. Every UpGuardian brings a little something extra to the team. UpGuard helps organizations manage third-party risk (TPRM) and monitor their attack surface. But great security work starts with a team of people worth spending your day with.
  |  By UpGuard
You understand the risks that third party vendors pose to your business, and you're ready to do something about it. What are the capabilities you need to understand your cyber risk, manage your vendors, and avoid data breaches?
  |  By UpGuard
Perhaps your organization is looking to make a transition from traditional IT operations and development practices to DevOps, or you're looking to realign your career path with DevOps to position yourself more favorably to future opportunities. Whatever your motivations are, this eBook will provide you with foundation knowledge for boosting your career with DevOps.
  |  By UpGuard
The fact that one has to "make a case" for Microsoft in the DevOps sphere puts them at a disadvantage, especially competing against major open source options with large community bases and proven performance. But, moving forward, one can expect the gap between Microsoft and other tools to close further, as they continue pressing their business in this direction.
  |  By UpGuard
ServiceNow® customers optimizing their IT service delivery and management processes require deeper context and detail level behind IT asset changes--information the leading help desk automation and incident reporting platform does not provide. In this report you'll learn how UpGuard fills this visibility and awareness gap, keeping ServiceNow® in line with the true state of your environment.
  |  By UpGuard
Cybersecurity is officially dead. Worldwide spending on security-related hardware, software and services rose to $73.7 billion in 2016 from $68.2 billion a year earlier, according to researcher IDC. This number is expected to approach $90 billion in 2018.
  |  By UpGuard
Selecting a security provider is no easy feat-it includes months of designing a company's security strategy, evaluating different solutions, budgeting accordingly, and assuring stakeholders the investment will pay off by keeping their business safe.
  |  By UpGuard
DevOps and ITIL should be compared with an eye towards the problem you're trying to solve, with a focus on the tangible benefits you and your team would see from using each.
  |  By UpGuard
With the enterprise so dependent on technology and digitized assets, how can it prevent data-related disasters from sinking the business? The answer is by taking a new approach to managing cyber risk as a function of business risk at large. McKinsey calls this "Digital Resilience", but it can simply be thought of as conducting business safely in today's connected environments.
  |  By UpGuard
Software engineering is changing and DevOps is at the heart of it. An organization's ability to be responsive to the business requires better collaboration, communication, and integration across IT.
  |  By UpGuard
There is no doubt that the DevOps movement has gone mainstream. When even IBM and HP are dedicating sites to it there is no longer any question. If we were to place it on the Gartner Hype Cycle even the most devoted proponents would have to admit that it's rapidly approaching the "Peak of Inflated Expectations".

A better, smarter way to protect your data and prevent breaches. Our products help security, risk and vendor management teams take control of cyber risk and move faster with confidence.

UpGuard gathers complete information across every digital surface, stores it in a single, searchable repository, and provides continuous validation and insightful visualizations so companies can make informed decisions.

UpGuard then aggregates this information into an industry standard cyber risk score called CSTAR. The CSTAR score is a single, easy-to-understand value representing an organization's aptitude in monitoring compliance, tracking unwanted change, and detecting vulnerabilities in their infrastructure.

Businesses depend on trust, but breaches and outages erode that trust. UpGuard is the world’s first cyber resilience platform, designed to proactively assess and manage the business risks posed by technology.