Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

PHP2Shell Didn't Break the Internet (Yet)

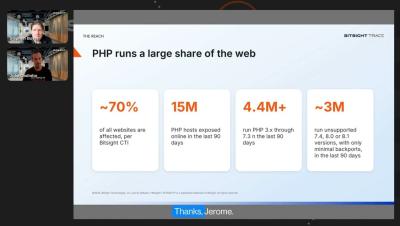
PHP2Shell (CVE-2026-109618 and CVE-2026-109619) arrived with predictions of a Log4Shell-scale mass exploitation event. Panic was visible, many rushed to update or even disconnect systems from the Internet until a patch was applied. PHP runs a large share of the web and the vulnerable ranges were reported to cover every branch from 5.4 to 8.5, which are essentially the majority of versions we can see deployed in the internet installed base.
AI-accelerated Vulnerability Discovery Demands Rethinking Vulnerability Management Practices

Enterprise security has a speed problem. Attackers are getting faster at finding and exploiting vulnerabilities, while many organizations still rely on ticket-based remediation, approvals, and scheduled maintenance windows. AI threatens to widen that gap considerably, exposing one of vulnerability management’s largest unchanged challenges: getting the right systems to fix the right problems before attackers exploit them.

PHP2Shell vs. Log4j: Understanding the Risk and Exposure | Bitsight Webinar

Could PHP2Shell pose a cybersecurity risk on the scale of Log4j? Newly disclosed critical PHP vulnerabilities are raising concerns about widespread exposure across enterprise environments and third-party supply chains. With millions of potentially affected systems and limited patching options for legacy PHP versions, security teams face a complex remediation challenge.

Third-Party Cyber Risk: The Regulatory Trends Reshaping Your Program

As U.S. and EU regulators increase scrutiny of third-party cyber risk, organizations face growing pressure to demonstrate effective vendor oversight, continuous monitoring, and risk management. In this Bitsight webinar, Jake Olcott, VP of Government Affairs and former legal counsel to the House Homeland Security Committee and Senate Commerce Committee, explores the regulatory developments shaping third-party risk management (TPRM) heading into 2027.

The CIO Answers for AI They Never Approved

When an AI system misfires inside a large company, the question that follows is who was responsible for it. The answer usually lands on the CIO, and frequently the CIO had no part in choosing, approving or deploying the thing that failed. ‍ This gets described as a governance problem, which undersells it. Governance implies a process that exists and performs badly.

Why AI Text Detectors Fail and What to Use Instead

Somebody in the organization will eventually propose running documents through an AI text detector. The instinct is reasonable and the method is the one approach the published evidence rules out, for reasons a security or risk function should understand before the policy gets written. ‍ The organization that built the most widely used language model tried this and withdrew its own tool after six months. Its reason was accuracy, and the figures it published before withdrawing explain why. ‍

The Best Identity Security Vendors for AI Agents

Every major identity vendor shipped an agent offering during 2026, and the datasheets converge on the same three claims. Agents get first-class identities, permissions are scoped, and access is governed. ‍ The question that separates them is narrower. When the engineer who built an agent leaves the company, what happens to the agent? The answers differ enormously, and they differ for reasons that trace back to what each vendor was originally built to do. ‍

Introducing Bitsight MCP and AI Mode: Cyber Risk Intelligence Built for the Agentic Era

AI is changing how attackers find and exploit weaknesses, and how security teams respond. As teams bring AI into more of their work, the data and context behind it becomes just as important as the model itself. Today, Bitsight is expanding how customers can use our industry-leading intelligence through three experiences: AI Mode, Bitsight MCP, and Bitsight Skills.

Building Cyber Risk Quantification In-House vs. Buying a Platform

A team that can write a Monte Carlo simulation over a loss distribution can build a cyber risk quantification model in a few weeks. The mathematics is undergraduate statistics and the code is not the obstacle. ‍ Three other things are, and each one outlasts the build. Loss data good enough to calibrate against, the work of keeping the model current once the person who wrote it moves on, and documentation that holds up when somebody who did not build it starts asking questions. ‍

AI Supply Chain Attacks Come Through the Plumbing

LiteLLM, a widely used open source gateway for routing requests across language model providers, was compromised twice in 2026. Malicious releases reached its public package registry in March and again in October, through two separate intrusions, each carrying a credential stealer into every environment that installed them. ‍ Neither attack touched a model. Neither one manipulated weights or tampered with training data.