Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

One Loss Distribution, Two Very Different Charts

A cyber loss model produces one distribution. How that distribution gets drawn changes what a reader can see in it, and the conventional projection hides the part most decisions depend on. ‍ The two views below contain identical data. One of them is close to unreadable for anything except the extreme tail, and the difference is worth understanding before the next time somebody asks what the number means. ‍
Top 14 Agent Observability Tools

Agent observability tools capture traces, metrics, logs, and evaluations across AI agent workflows. They help teams reconstruct execution paths, inspect tool calls and handoffs, diagnose failures, and monitor latency, cost, and output quality. This guide also covers complementary security platforms that discover agents, enforce runtime policies, or control the privileges agents receive. Agents don’t fail in straight lines.

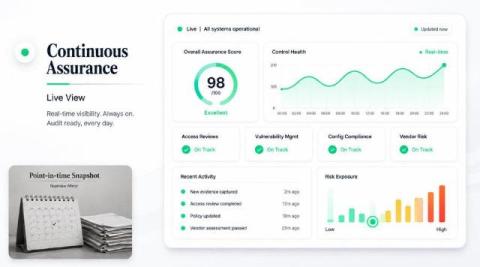
Legacy GRC can't keep up. Cyber risk assurance can.

Enterprise security teams need to secure a risk surface that is constantly changing. However, the tools in their stack were built to check only a fraction of that risk. For confirmation, they rely on static snapshots and annual attestations. I now see this as the defining problem in GRC. When 451 Research (S&P Global) initiated coverage of TrustCloud in this space, they described a clear and growing divide.

What You Need to Know about the CareCloud Data Breach

CareCloud, Inc. is a publicly traded healthcare technology company headquartered in Somerset, New Jersey. The company provides electronic health records, medical billing, practice management, and revenue cycle services to more than 45,000 healthcare providers across the United States. Because it stores patient records and billing information on behalf of hospitals, doctors' offices, and other medical practices, CareCloud holds sensitive data belonging to millions of patients.

What You Need to Know about the Microsoft Azure Employee Data Breach

A threat actor using the alias TheHatman is selling employee databases allegedly stolen from the Microsoft Azure cloud environments of some of the world's largest companies. Beginning on July 31, 2026, the cybercriminal posted a series of listings on underground forums advertising data dumps from at least nine major organizations, claiming the records were downloaded directly from corporate Azure tenants using compromised credentials.

Emerging Threat: (CVE-2026-21580) Confluence Privilege Escalation via Unauthenticated Stored XSS

CVE-2026-21580 is a stored cross-site scripting vulnerability in Atlassian Confluence Data Center and Server, which the vendor advisory groups together with a privilege escalation component and a security misconfiguration weakness. An attacker persists crafted HTML or JavaScript on a vulnerable instance, and that payload executes later in the browser of whichever user views the affected content. The vulnerability carries a CVSS 4.0 base score of 8.6.

Living Off the Land Attacks: Detection and Response Guide

The most popular advice about living off the land attacks is also the least useful when it stands alone: hunt for suspicious PowerShell, block LOLBins, and alert whenever a signed Microsoft binary behaves unexpectedly. Those controls have value, but they don't solve the operational problem. PowerShell, WMI, certutil.exe, and bitsadmin.exe are legitimate administrative utilities, and attackers abuse them precisely because security teams can't remove them without disrupting normal work.

Penetration Testing Options Worth Knowing

Penetration testing has turned into one of those services every business claims to offer, but the actual delivery varies wildly. Some firms hand you an automated scan with a logo slapped on the report. Others put a named, accredited tester on your network who explains exactly what they found and why it matters. For businesses, charities and schools weighing up who to call, the accreditation behind the tester matters as much as the report format. Here are eight providers worth knowing, starting with a CREST-accredited option built around direct access to the people doing the work.

How to Develop Vulnerability Assessment Skills Through Cybersecurity Courses

This process is a vital part of digital protection because it helps organizations identify technical flaws before unauthorized users exploit them. Experts who develop accurate evaluation skills examine computers, networks, software and settings to determine where security upgrades are required. Cybersecurity courses offer structured information plus hands-on practice to help students learn evaluation methods, analyze results and suggest specific safety protocols.