Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

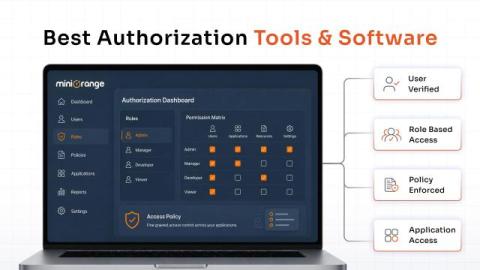
What Are the Best Authorization Tools and Software in 2026?

Stolen or misused credentials are the second most common way for attackers to get in, according to the latest Verizon Data Breach Investigations Report (DBIR). The consequences can be severe, with the average cost of a data breach reaching a record high of $10.22 million in the United States, according to the IBM Cost of Data Breach Report. A major driver behind these security incidents is that engineering teams confuse authentication and authorization quite frequently.
Cyber Threat Intelligence for Fintech: A Sector Built for Speed, Targeted for the Same Reason

UK fintech is one of the country's fastest-growing sectors, but its reliance on APIs, partnerships, and real-time data makes it a prime target for cybercriminals. This blog explores why fintechs are so exposed, what the latest UK data reveals about breach costs and supply chain risk, and how cyber threat intelligence helps firms grow securely.

Shai-Hulud was the best thing to happen to supply chain security

npm launched Package Provenance in late 2022. For two years, adoption averaged 20-50 packages per week. Followed by Trusted Publishing in 2024. Blog posts were written. CISA advisories were issued. The line barely moved. Eventually Trusted Publishing with OIDC was made Generally Available in July 2025 Then Shai-Hulud hit. Weekly adoption jumped to 430 packages. In 18 months, cumulative adoption grew 3.4x.

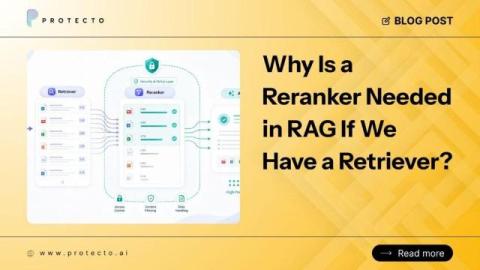
Why Is a Reranker Needed in RAG If We Have a Retriever?

Enterprise RAG pipelines have a recall stage and a precision stage. The retriever handles recall. The reranker handles precision. Skipping the reranker, or misplacing security controls around it, is where most accuracy and data exposure problems begin. The retriever’s job is to pull back every document that might be relevant. The reranker’s job is to find, from that candidate set, the documents that actually answer the question.

Introducing JFrog Platform Federation: One Control Plane for Synchronizing Every Site in Your Software Supply Chain

It’s 2 p.m. on a Tuesday. Your primary region goes down. Your software artifacts have been syncing to your Disaster Recovery site the way they were designed to, but your projects, permissions, and security policies were never part of the package. Instead of flipping the lights back on, your platform team is scrambling to manually reconstruct governance while builds grind to a halt across every other region.

Donation Forms Attract Card Testing Attacks

A charity notices something odd in its payment dashboard. Hundreds of one dollar donations attempted overnight. Almost all declined. A handful approved. Nobody donated anything. The organization was being used as a validation service. Donation forms have become a preferred target for card testing, and the reasons are structural rather than accidental. Here is how the attack works, why nonprofit payment pages are disproportionately attractive, and what actually stops it.

PoshC2 Explained: Capabilities, Indicators, and Detection

PoshC2 version 6.0, an open-source command and control framework, is notable for its robust capabilities in managing compromised hosts. Accompanying its release, a comprehensive list of Indicators of Compromise (IoCs) and a dedicated GitHub repository have been provided. These resources are designed to assist cybersecurity teams in detecting PoshC2, especially when deployed with its default settings, which less sophisticated attackers often utilize.

What Is Noise Reduction in SIEM and Security Monitoring

A SOC analyst starts a shift with a queue full of alerts. The first few investigations reveal repeated authentication failures from the same service account, blocked network scans from a known internal scanner, and endpoint events that three different sensors reported separately. Somewhere in that queue may be a real compromise, but the analyst has to work through the noise before finding it.

Human in the Loop: How to Tell If the Review Is Real

Human oversight is the only control in an AI program that can stop working while producing exactly the same evidence as when it worked. A failed encryption control throws errors. A monitoring pipeline that breaks stops delivering alerts. A review step that has become a formality still generates approvals, timestamps and sign-offs, and the compliance file looks identical. ‍ The asymmetry makes the design question secondary to the measurement one.