Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Building AI agents in Tines Stories: tips and tricks for advanced builders

This is the second in a two-part series on AI agents in Tines Stories. Part one covers the foundations: when to use agents, how to configure them, how to write prompts that work, and how to build securely. This post goes deeper on the patterns that separate robust, well-built agents from just good enough ones.
Episode 19 - The Cap on Inference: Proving How Network Data Quality Drives AI Security ROI

In this episode, host Richard Bejtlich sits down with Corelight Co-founder and Chief Strategy Officer Greg Bell to unpack groundbreaking research that quantifies exactly how data quality impacts AI-driven security automation. Moving past qualitative industry hype, Greg shares hard evidence from an empirical experiment pitting leading AI agents against real-world Capture the Flag (CTF) challenges and incident response report writing. The findings reveal a dramatic truth: basic firewall and flow logs place a hard cap on inference, throttling an LLM's capacity for deep insight.

Building Trust in AI for Cybersecurity | Arctic Wolf

Cybersecurity has reached a turning point. As defenders embrace AI, the question is not simply whether it is powerful, but whether it can be trusted to deliver real value. The Arctic Wolf Aurora Superintelligence Platform brings together trusted AI, real-world data, and human expertise to help transform security operations with reliability, governance, and results.

AI-Powered Cybersecurity at Machine Speed | Arctic Wolf

AI is accelerating cyberattacks, pushing security teams to their breaking point. Arctic Wolf helps organizations get ahead and stay there with the Aurora Superintelligence Platform, combining AI that is built in, not bolted on, with human validation and 24x7 security operations. See how Arctic Wolf helps protect more than 10,000 customers.

Find and Fix Risky Firewall Rules | Reach Security Demo

A firewall rule set to allow any source to any destination can stay live for months. It cancels out the rules beneath it and lets traffic pass unchecked. That kind of drift sets off no alarm. It builds up between quarterly reviews, while small teams govern 50 or more firewalls and hundreds of rule changes a week. Reach Network Security Assurance finds these controls, shows how long each has been open, ties the finding to real exposure, and guides the fix.

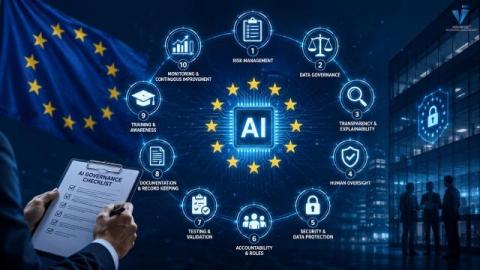
EU AI Act Readiness: 10 Controls Every Organization Should Implement in 2026

This is for compliance and security leaders who already know the EU AI Act applies to them and need a concrete control set for where the law actually stands today — not a summary written before the rules changed. Awareness is done; 2026 is the year of implementation, and the rules just moved. On 29 June 2026 the Council of the EU gave its final green light to the Digital Omnibus on AI — the package that resets several of the dates compliance teams have been building toward.

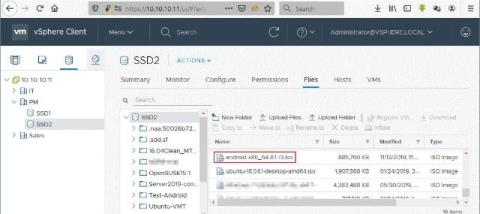
Installing Android on VMware ESXi: A How-To Guide

Android is a very popular and prolific operating system on mobile devices such as smartphones and tablets. Most of the time, there is no practical reason to install Android on a physical computer, but there may be some cases when you need to run Android on a virtual machine (VM), for example, when developing applications for Android and testing them. Fortunately, you can install Android on VMware Workstation, VMware Player, VMware ESXi, and VirtualBox.

A Guide to Firewall Management: How to Set Up Proper Firewall Rules

Firewalls remain one of the most foundational controls in any security program. Nearly every organization has at least one, and in many cases, hundreds. Despite widespread deployment, firewalls are frequently a source of unintended exposure rather than protection. The reason is almost always in how firewall rules are maintained over time, not the technology itself.

Benchmarking 13 AI models on rediscovering known CVEs

TL;DR Every frontier model launch now comes with the same cybersecurity claim: it finds vulnerabilities. But does it work on a real bug in a real repository, or just on a curated example? Of the dozen models you could pick, which is worth trusting with code review? And since the strongest models cost ten times or more per run than the cheapest, what does that extra spend actually buy you in bugs found?