Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Not Making It Easy for Attackers Also Starts with Catching What Slips Through

Security is built on the small decisions we make each day. That’s why Cybersecurity Awareness Month 2026 focuses on the habits that make life harder for attackers—such as using strong passwords, enabling multi-factor authentication (MFA), recognizing and reporting scams, and keeping software updated. However, security awareness must also address the risks that arise when employees introduce new applications and services into their work.
Rai Expands: WatchGuard's Agentic AI Digital Workforce Is Now Available

At IMPACT North America, WatchGuard showcased a simple idea with significant implications for managed security: the next phase of cybersecurity AI is not only about helping people work faster. It is about expanding what the security operation itself can do. Today, that next evolution of Rai is generally available. Rai is WatchGuard’s agentic AI Digital Workforce, built specifically for MSPs and embedded in WatchGuard Cloud.

Stopping destructive commands in AI agents

An engineer gives a coding agent a routine task: clean up an old test deployment. The request sounds harmless, and the environment is cluttered with unused cloud resources, stale branches, and temporary credentials that should have been removed weeks ago. The agent gets to work. It lists resources, identifies old infrastructure, and finds a deployment command. Then it sees a naming pattern that appears to connect the test environment to production.

The NSA said wildcard certificates are bad. Everyone uses them anyway.

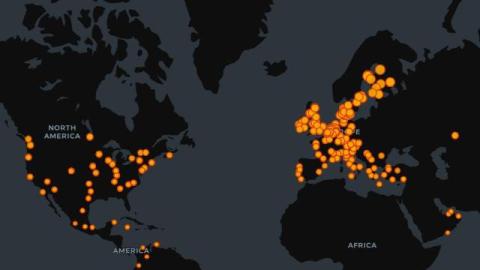
In October 2021 the NSA published an advisory titled “Avoid Dangers of Wildcard TLS Certificates.” It reiterated what security consultants had been saying for years: don’t use wildcard certificates. Single-name certificates per host are safer. Five years later, we counted the certificates that are actually used. One in three domains has a wildcard on it. For.bank domains, where you need a security review just to register, it’s four in five. Operators aren’t careless.

Emerging Threat: (CVE-2026-107406) NetScaler ADC and Gateway Remote Code Execution via SAML

CVE-2026-107406 is a memory overflow vulnerability in NetScaler ADC and NetScaler Gateway, classified as CWE-119. Successful exploitation leads to remote code execution or denial of service. The vulnerability carries a CVSS v4.0 base score of 9.5 (Critical). Attack vector is network, and neither privileges nor user interaction are required.

Seemplicity + Miggo: Runtime Detection, Closed Risk

Most application-layer attacks slip past EDR, WAFs, and CNAPP because none of them watch what an app actually does at runtime. Miggo’s ADR platform does, detecting behavioral deviations agentlessly via DeepTracing and eBPF. With the new integration, those runtime detections flow directly into Seemplicity, where they’re correlated with cloud, code, and identity findings, deduplicated, and routed to the right owner.

Why Businesses Should Review Tax Incentives When Purchasing New Technology

Innovating through technological purchases is an effective means of enhancing efficiency, boosting productivity, and ensuring competitiveness in dynamic market environments. But it should be noted that apart from the direct cost of technology, its financial implications might include tax savings as well. There are various tax incentives offered by the government depending on the type of technological investment that a firm makes. It is necessary to analyze these tax incentives prior to a decision to make such investments to ensure wise management of resources.

5 patch essentials: The SMB benchmark for patch management

If you're the entire IT team at your company, you probably wear more hats than your title suggests. Between helpdesk tickets, network maintenance, and strategic projects, patch management often gets pushed to the background—and it probably wins your attention only after an incident or an audit. The problem is, threats don't wait for a quiet day. New vulnerabilities are piling up and exploit windows are shorter than ever.

Why IGA leaders choose Identity Manager, in their own words

The most experienced identity governance leaders don't need to experience the wrong platform before they understand what to look for. They recognize early that a mature identity governance and administration (IGA) program requires real customization, hybrid support that doesn't degrade over time and vendor investment in both on-premises and software as a service (SaaS), and they choose Identity Manager by One Identity from the start, renewing for the same reasons they first signed.
Sponsored Post

Endpoint Central through the AV-Comparatives lens

Getting certified by AV-Comparatives is not straightforward. The organisation runs one of the most thorough independent endpoint security evaluations available. Vendors must comply with comprehensive security software evaluations to receive unbiased feedback regarding their products and feature updates.