Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Modern Data Security Should Be Anchored To Your Data's Lineage

New AI tools appear every day. The novelty and utility they bring, along with the constant pressure to be more productive, pull employees toward them to get work done faster. The intent is good but the effect can range from problematic to damaging, because while there are rules in place for sanctioned tools, there are none for the ones that quietly show up in between.
iGaming Fraud Prevention: How to Protect Player Accounts Preemptively Without Adding Friction

iGaming fraud prevention does not have to mean applying more security checks broadly across the player journey. For player account takeover, the better objective is to obtain enough reliable risk context early enough to reserve additional checks for the accounts and access attempts that actually warrant them. The commercial stakes are growing alongside the market. U.S. iGaming revenue reached $10.73 billion in 2025, up 27.6% year over year, according to the American Gaming Association.

The Great Infrastructure Reset: Infrastructure Conversations Have Changed

Infrastructure conversations have changed. Today, customers are balancing rising infrastructure costs, licensing renewals, and the need for greater cyber resilience all at the same time. We’re calling this The Great Infrastructure Reset: a shift in infrastructure strategy driven by market forces that customers can’t ignore. For our partners, this creates an opportunity to lead with strategic conversations. Help customers understand what’s changing, what it means for their business, and how to build an infrastructure strategy for what’s next.

WAF vs WAAP API vs AI What Security Tools Do You Actually Need?

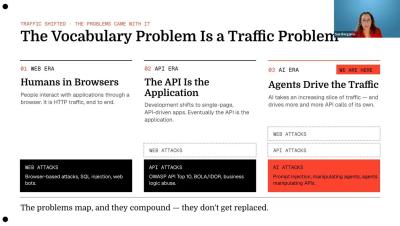
A straightforward framework for matching each layer of protection to the problem it actually solves. Trying to understand vendors in the modern application security space can feel a lot like trying to solve word scramble. Whether it’s remembering what the “A’s” in "WAAP” stand for, figuring out if “WAF” includes APIs, or assessing the actual function of a new AI security product, understanding what tools your team actually needs is getting harder all the time.

MDM vs. MAM: Which Mobile Management Option Fits Your Business?

Every IT team managing a mobile workforce eventually hits the same fork in the road: do you manage the whole device, or just the apps that matter? That question sits at the heart of the MDM vs. MAM debate. Getting the answer wrong can mean either locking down employee phones so tightly that people revolt, or leaving corporate data exposed on devices you barely control. Mobile Device Management (MDM) and Mobile Application Management (MAM) solve overlapping problems in very different ways.

AI Governance for Public Bodies, and Who Shares the Obligation

A public body running a high-risk AI system owes a fundamental rights impact assessment under Article 27 before first use, with the results notified to a market surveillance authority. The obligation is real and it is not yet in force. ‍ Regulation (EU) 2026/1744, in force since July 2026, deferred the section of the Act containing Article 27 to December 2027 for standalone high-risk systems and August 2028 for those embedded in regulated products.

Vulnerability Management: A Complete Guide to the Process and Lifecycle

If your vulnerability management program runs on a fixed scan-and-patch cadence, whether monthly, quarterly, or tied to a compliance deadline, you are measuring your response time against an attacker timeline that continues to accelerate. Vulnerability management remains a foundational security discipline. It identifies real, exploitable flaws and gives teams a structured way to prioritize and remediate them.

CISO Risk Intel Brief: Tokens, Policy, and the Edge Under Siege

The week’s material risk is not a single CVE. It is the identity and policy control plane. In seven days, CISA confirmed active exploitation against Cisco Identity Services Engine, Check Point VPN and management servers, F5 BIG-IP Access Policy Manager when used as an OAuth authorization server, and Arista’s on-prem VeloCloud Orchestrator. These products issue tokens, enforce network policy, or orchestrate SD-WAN.

The New CISO Ep. 151 - Sean Murphy | Complacency Kills: Why More Discomfort Might Fix Your Burnout

Sean Murphy spent more than twenty years in the CISO chair and walked away from it while things were going well. In this episode of The New CISO, he returns to talk with Steve Moore about trading the operational seat for a field CISO role at F5 — and why getting too good at the job was the warning sign.