
|
By Rohan Kar
Two critical PHP vulnerabilities have been disclosed, potentially exposing millions of web servers to remote code execution. Cloudflare has already responded by deploying emergency WAF protections. For Reach customers using Cloudflare WAF, Reach Drift automatically detected the new rules and confirmed they were enabled and configured to block malicious traffic.
|
By John Dominguez
Security information and event management, or SIEM, remains one of the foundational technologies in the security operations center. Gartner defines SIEM as a configurable system of record that collects, aggregates, and analyzes security event data from on-premises and cloud environments to support threat detection, investigation, and response, along with compliance requirements.
|
By John Dominguez
If you're comparing vendors, our guide to the top Exposure Assessment Platforms in 2026 looks at how leading platforms approach discovery, prioritization, and remediation.
|
By John Dominguez
Security controls change constantly. Firewall rules are modified, endpoint exclusions are added, identity policies are adjusted, and temporary exceptions appear as teams respond to new business and operational requirements. Some of those changes are expected. Some turn out to be harmless. Others quietly weaken the defenses organizations depend on. Detecting that a configuration changed is really important for security teams, but it’s just the beginning of the investigation.
|
By John Dominguez
If your vulnerability management program runs on a fixed scan-and-patch cadence, whether monthly, quarterly, or tied to a compliance deadline, you are measuring your response time against an attacker timeline that continues to accelerate. Vulnerability management remains a foundational security discipline. It identifies real, exploitable flaws and gives teams a structured way to prioritize and remediate them.
|
By CP Morey
Security posture is one of the most used yet misunderstood concepts in cybersecurity. For some, it means being audit-ready. For others, it’s shorthand for how many tools are deployed across endpoints, identities, and cloud environments. But in practice, posture is something deeper. It’s the ability of your environment to withstand real-world threats, not just meet compliance requirements. Strong posture doesn’t just reflect what’s present.
|
By CP Morey
Zero Trust is often summarized as “never trust, always verify.” More precisely, it is a security model built on the premise that trust should never be granted implicitly based on where a user, device, workload, or resource sits. That makes Zero Trust much bigger than deploying a particular product or turning on a handful of access policies.
|
By Reach Security
Twelve months of production telemetry reveal the scale, causes and security impact of configuration drift, pointing to firewall and EDR tool risk.
Featured Post
Network security protects the nervous system of modern businesses. Highly connected and widely distributed throughout the corporate body, it keeps applications regulated, tools performing, and operations stable when functioning well. But like the human nervous system, it is vulnerable to drifting away from an optimal state and becoming weaker, leaving it open to attack. While the human nervous system is affected by stress, lack of sleep, and poor nutrition, digital network security is prone to accidental misconfigurations, ungoverned rule changes, and controls that drift away from their intended state.
|
By John Dominguez
An Exposure Assessment Platform (EAP) discovers assets, identifies exposures such as vulnerabilities and misconfigurations, prioritizes them with threat and business context, and helps drive remediation. Gartner formalized EAPs as a distinct market in November 2025, and the category has quickly become the technology backbone of Continuous Threat Exposure Management (CTEM) programs.
|
By Reach Security
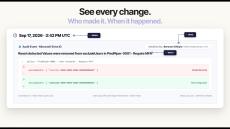
Reach's Drift History capability enables security teams to see every security control that was changed, who made the change, and when it happened. See the full story and context behind every security control change, prioritize action, and automatically fix misconfigurations with Reach.
|
By Reach Security
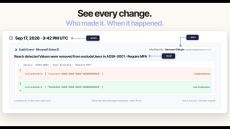
Reach's Drift History capability enables security teams to see every security control that was changed, who made the change, and when it happened. See the full story and context behind every security control change, prioritize action, and automatically fix misconfigurations with Reach.
|
By Reach Security
Garrett Hamilton, co-founder and CEO of Reach Security, joined Jonathan Brucato, Vice President of Cyber Defense at ECI. In this clip, Garrett walks through Reach Everywhere with a ransomware detection as the example: what the controls on that host look like, and what changed in the weeks before. In the full episode.
|
By Reach Security
CrowdStrike Falcon provides powerful endpoint detection and response capabilities. But as environments scale and changes are made, CrowdStrike security controls can change and drift away from security baselines. This can create open doors in your defenses that fast-moving AI-powered adversaries can find and exploit. Reach analyzes your CrowdStrike Falcon security controls and takes rapid action to close these doors to attackers. Reach finds and fixes control misconfigurations, activates unused capabilities, and detects and remediates configuration drift.
|
By Reach Security
Every security team has a source of truth for its assets and its identities. Very few have one for how those assets are protected. Here Garrett explains what that source of truth has to look like and why it has to be deterministic. Garrett joined Ed Amoroso of TAG Infosphere for a wider conversation on AI, security controls, and assurance. The full interview covers.
|
By Reach Security
Reach brings autonomous defense to the security controls organizations already own. AI-powered attackers can find and exploit misconfigured controls, configuration drift, and unpatched vulnerabilities in minutes. Reach helps defenders find and close those gaps first. It mitigates vulnerabilities with compensating controls, autonomously finds and fixes misconfigured security controls, and stops configuration drift.
|
By Reach Security
Reach Security has raised more than $50 million in Series B funding, led by Top Tier Capital Partners, with participation from Ballistic Ventures, In-Q-Tel, M12 (Microsoft’s venture fund), Artisanal Ventures, and existing investors.
|
By Reach Security
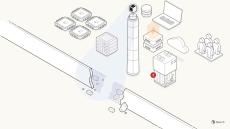
Your defenses have weaknesses. Misconfigured security controls, configuration drift, and unpatched vulnerabilities all open doors for fast-moving AI-powered attackers. Slam the door shut on attackers with Reach's security controls source of truth.
|
By Reach Security
Point an AI model at a security stack it doesn't fully understand and you get confident, wrong answers faster. Reach gives your AI a source of truth for security controls. The MCP Server connects MCP-compatible AI tools directly to Reach. The Public API brings Reach findings and evidence into SIEM, ticketing, and GRC workflows. The MCP Server is intentionally read-only, so your team decides when recommendations become actions.
|
By Reach Security
Every security configuration has a backstory. Drift History takes you down memory lane. See what changed, when it changed, who made the change, and how your team responded along the way. Then fix what still needs attention.
- October 2026 (9)
- September 2026 (11)
- August 2026 (6)
- July 2026 (14)
- June 2026 (12)
- May 2026 (8)
- April 2026 (10)
- March 2026 (7)
- February 2026 (9)
- January 2026 (15)
- December 2025 (15)
- November 2025 (20)
- October 2025 (3)
Reach helps you get the most from your existing security stack by uncovering exposure, misconfigurations, and weaknesses that tools often miss. Using AI agents, it prioritizes and drives remediation based on real exposure, reducing operational costs and enabling measurable, preventive action, all from the leader in AI-Native Exposure Management.
Expose and eliminate hidden risk within your security stack:
- Threat Exposure Management: Reach identifies exposure that is actually reachable, like those on end-user devices that enable ransomware delivery. By focusing on real exposure, it helps you prioritize actions that measurably reduce risk.
- Security Posture Management: Weak controls create protection gaps like those that allow session hijacking or lateral movement. Reach helps you strengthen your posture by continuously validating whether your security controls are working as intended.
- Configuration Management: Misconfigurations leave systems open to attack. Reach finds these weaknesses across your stack and recommends precise, context-aware fixes that simplify remediation and reduce friction for your team.
AI Agents for Security Architects.