Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

From MSP to Strategic Advisor: Lead with Risk

The MSP landscape is evolving. Customers increasingly expect more than technology management, they want trusted partners who can help them understand, reduce, and manage cybersecurity risk. WatchGuard's upcoming “Provider to Advisor: The MSP Shift Toward Risk Leadership” webinar explores exactly this opportunity.
Best Shadow AI Governance Tools for Enterprises: Buyer's Shortlist

Security teams already know employees use generative AI. The harder problem is buying the right platform before unsanctioned apps move sensitive data outside your visibility and control. UpGuard research found 81% of employees and 88% of security leaders use unapproved AI tools, and 45% of workers find a workaround when their employer blocks an app. That last number should shape your buying criteria more than the first two. Demand doesn't disappear when you block it. It moves somewhere you can't see.

Introducing App Store Threat Detection: Visibility Where Brand Monitoring Couldn't Reach

In January 2024, Craig Raw, the developer of the real Sparrow Wallet, a Bitcoin wallet app, warned that a fake version of his app was live on the Apple App Store. He reported it repeatedly, but the listing stayed up. By August 2025, three people had lost a combined $1.8 million to it: Jalen Delgado (about $120,000 in May 2025), James Ramirez (about $875,000 in July 2025), and Christopher Ellis (about $840,000 in August 2025). All three are now suing Apple. The complaint, Ramirez, et al. v.

Autonomous Pentest Findings: Unauthenticated Kill Switch

Some of the most dangerous vulnerabilities in modern web apps are the default features left switched on where they were never meant to be reachable. The first entry in our Findings from the AP series looks at an exposed actuator endpoint. On paper, this finding started the same way most do: an HTTP endpoint returned a 200. Nothing about that response looks unusual by itself. It’s the kind of line that gets logged, categorized, and moved past in most automated scans.

Emerging Threat: (CVE-2026-67281) MikroTik RouterOS Unauthenticated File Read via WebFig

CVE-2026-67281 is an unauthenticated file read vulnerability in WebFig, the web-based management interface in MikroTik RouterOS. A newly allocated session on the /jsproxy path retains a stale, uninitialized principal pointer that WebFig then uses for file authorization decisions. The vulnerability carries a CVSS v4.0 base score of 8.7 (High). A CVSS v3.1 base score has not been assigned in the CVE record at the time of writing.

The Ultimate API Security Guide: Everything You Need to Know to Protect Your APIs

APIs power modern software. They connect apps, move data, and run agentic AI workflows. But every API is also a door into your systems. Attackers know this. They target APIs more than any other layer today. This guide breaks down API security from the ground up. You will learn what it means, why it matters, and how to protect your APIs against real-world threats. We cover risks, the OWASP API Security Top 10, best practices, tools, and use cases. Let’s get started.

Cyber Threat Intelligence for Insurance: The Supply Chain Risk Insurers Can't Ignore

A strong internal security score means little if the brokers, claims processors, and software vendors an insurer depends on are the weak link. This blog breaks down where insurance supply chain risk sits and what to do about it.

Twitter Brand Impersonation: How Security Teams Detect Fake Accounts and Phishing on X

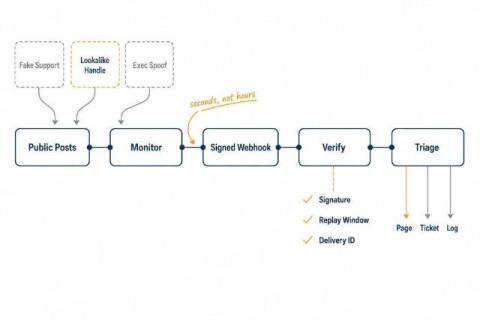
Most brand impersonation starts in public. A lookalike support handle appears, replies to real customers under your official account, and links to a credential-harvesting page. By the time it reaches a takedown vendor's weekly report, the damage window has been open for hours.

How Enterprises Vet Vendors: A Digital Contact Card Case Study

Every large company works with dozens, sometimes hundreds, of outside vendors. From software providers to marketing agencies to hardware suppliers, enterprises depend on a wide network of partners to keep operations running smoothly. But before any vendor gets a seat at the table, they go through a process that can feel like a job interview crossed with a background check. This process is called vendor vetting, and it exists to protect the enterprise from risk, wasted money, and reputational damage.