Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

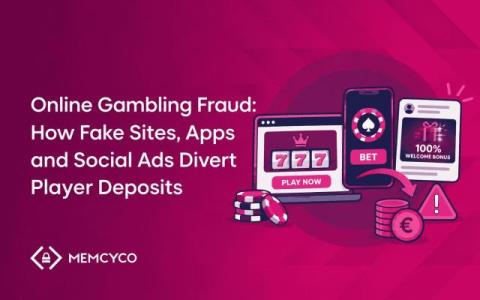
Online Gambling Fraud: How Fake Sites, Apps and Social Ads Divert Player Deposits

Online gambling fraud includes more than bonus abuse, payment fraud, account takeover and suspicious withdrawals on a genuine betting platform. Fake gambling sites, cloned apps and deceptive social ads can capture players before they reach that platform, diverting registrations, credentials and deposits into an attacker-controlled or unlicensed environment.

When scanners miss the attack: how Cloudflare Client-Side Security protects storefronts

A modern storefront can look perfectly healthy while malicious JavaScript works underneath: siphoning affiliate revenue, hijacking searches and clicks, tampering with analytics, or asking a remote server what to execute next. Pages load, products appear, and checkout works — yet the browser may be quietly doing something the site owner never authorized. That is the blind spot our Client-Side Security machine learning (ML) model is built to expose.

Top 7 API Security Tools for Banks and Fintechs in 2026

Every digital banking transaction today, whether it’s a fund transfer, a loan approval, or a balance check through a fintech app, runs through an API. API security for banking means protecting these connections from attacks that go far beyond simple hacking attempts: fraud rings probing for account access, bots automating fake transfers, and partners quietly overstepping the access they were given.

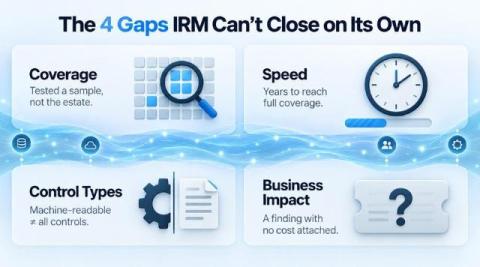
Four gaps IRM was never built to close

A buyer’s checklist for the IRM gaps a ServiceNow program leaves open. Many teams deploy IRM, watch the assessments come back clean quarter after quarter, and reasonably conclude they are covered. Months later, the greatest risk turns out to have been outside the sample. It may have changed the week after the review, or lived in a control type nobody tested, or lacked context or prioritization to see its importance.

From Encrypted Mobile Traffic to Payment Manipulation

How KomodoSec’s AigentX Penetration Tester reverse engineered client-side encryption, turned the bypass into reusable Burp tooling, and used that access to validate a real business-logic flaw in a production mobile application. Client-side secrecy failed. Server-side trust became the real vulnerability. THE CHALLENGE A mobile app with TLS, certificate pinning, and a second encryption layer.

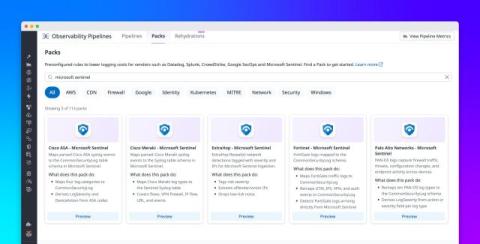
Transform and route security logs to Microsoft Sentinel tables using Observability Pipelines

Microsoft Sentinel is Microsoft’s cloud-native SIEM for detecting, investigating, and responding to threats across your environment. To query security data and run analytics rules, Sentinel expects telemetry data in specific table schemas. But firewall, VPN, and network detection logs arrive in vendor-specific formats, making source-specific mappings difficult to maintain as environments grow.

CrowdStrike Accelerates Real-Time Data Classification with On-Device AI

Modern data security depends on understanding sensitive data as it is created, accessed, and moved in real time directly on the endpoint. In addition to identifying predefined patterns such as credit card numbers or Social Security numbers, organizations must protect unstructured information including documents, chat logs, support tickets, AI prompts, medical records, and free-text fields.

AI anxiety is showing up on the org chart

Accelerating security solutions for small businesses‍ Tagore offers strategic services to small businesses. A partnership that can scale‍ Tagore prioritized finding a managed compliance partner with an established product, dedicated support team, and rapid release rate. Standing out from competitors‍ Tagore's partnership with Vanta enhances its strategic focus and deepens client value, creating differentiation in a competitive market.

The cache miss that made our agent faster

Accelerating security solutions for small businesses‍ Tagore offers strategic services to small businesses. A partnership that can scale‍ Tagore prioritized finding a managed compliance partner with an established product, dedicated support team, and rapid release rate. Standing out from competitors‍ Tagore's partnership with Vanta enhances its strategic focus and deepens client value, creating differentiation in a competitive market.

More Vulnerabilities Are Being Found Than Ever Before. That's Good News.

If you've glanced at a vulnerability tracker lately, the numbers look alarming. The Forum of Incident Response and Security Teams (FIRST) now projects roughly 66,000 CVEs will be published in 2026; up from a February forecast of 59,427 and closing in on 70,000 by some counts. That would follow a record 2025, which finished at roughly 48,000 disclosed CVEs, itself a sharp climb from about 40,000 the year before. It's tempting to read that curve as a sign that software is getting worse. It isn't.