Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

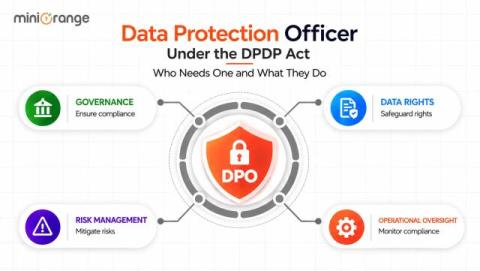
Data Protection Officer Under the DPDP Act: Who Needs One and What They Do

Not every organization that processes personal data has to appoint a Data Protection Officer. Under India's Digital Personal Data Protection Act, 2023, this duty applies only to Significant Data Fiduciaries (SDFs), a category the government assigns based on the scale and sensitivity of the data an entity handles. So before you assume your business needs a data protection officer, it helps to know exactly where this obligation begins and ends.
Best practices: How to implement Kerberos authentication correctly in your AD environment

Authentication configuration issues, especially those tying into Kerberos, are a big call driver for the Active Roles by One Identity Support team. When Kerberos requirements are met, Integrated Windows Authentication typically attempts Kerberos before falling back to NTLM. Due to expected IIS functionality, we will see multiple HTTP requests which trigger authentication repeatedly.

Employee Investigations: How to Close the Digital Evidence Gap

Your DLP flags a sensitive file transfer. Your SIEM identifies unusual activity. Your EDR detects an event on an employee’s endpoint. Your security tools did their job. They told you something happened. But now comes the harder question: What actually happened? That is where many employee investigations encounter a visibility gap.

Protecting Assets from Cyber-Physical Attacks

Our digital and physical worlds are now closely linked. This connection brings incredible efficiency, but it also creates new vulnerabilities. When digital systems control physical infrastructure, a security failure can have real, tangible consequences. Protecting your assets today means having a strategy that tackles threats in both these areas at the same time.

Why Retired IT Equipment Can Become a Cybersecurity Blind Spot

The security team at a mid-sized insurer spent eighteen months hardening everything that faced the internet. They rotated credentials, tightened their identity provider, and ran tabletop exercises until the incident playbook felt routine. Then a contractor bought a pallet of decommissioned laptops at a regional auction and found four of them still booting into a cached domain profile. Nothing had been breached. The data simply walked out through the loading dock, on equipment the company had already stopped thinking about.

AI Governance as a Condition of Writing Coverage

Insurers are subject to AI governance rules and they are also the party asking other organizations AI governance questions as a condition of coverage. More than twenty states have adopted the model bulletin that turns AI oversight into an operational requirement for carriers, and those same carriers now send AI questionnaires to their corporate insureds. ‍ The sector facing both is well covered. What follows from it is not, and it produces something an insured can use. ‍

Two Reporting Clocks on One AI Product, Only One Running

An AI product sold in Europe is described as facing two incident reporting duties. One under product security rules and one under AI rules, with different triggers and different deadlines. ‍ Only one of them is running. Article 14 of the Cyber Resilience Act has applied since 11 September 2026. The AI duty moved, and coverage published in the last few weeks still describes it as live. ‍

AI governance monitoring: how to prove your program is actually working

Ask a governance lead which of their AI controls actually ran last Tuesday at 2:14 p.m., when a specific agent touched a specific dataset, and the answer usually arrives as a policy document, an org chart, and a shrug. That gap between the controls a program claims to have and the controls that actually fired when an agent acted is where AI governance quietly fails. Policy documents describe intent. Model monitoring tracks accuracy and drift.

MovieReaper Malware: From Movie Download to Malware Infection

MovieReaper is a malware family first observed in September 2026 that combines remote-access trojan and loader functionality in a modular, multi-stage framework. It targets x86-64 systems and is built to reach remote machines, install additional components, persist across reboots, and exfiltrate data while resisting analysis through anti-sandbox, anti-VM, and AV-evasion features.