Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Bitdeer Extends Its Infrastructure Strategy From Bitcoin Mining to Full-Stack AI Cloud and Model Studio

Every mining cycle returns to the same unromantic question: what does one megawatt earn after the electricity bill? As hashprice narrows the margin on mining hardware, AI workloads offer power-rich operators another source of revenue. Bitdeer's move into full-stack AI Cloud is therefore less a change of identity than a change in how infrastructure gets paid.
AI for Career Development: From Skill Assessment to Professional Growth

Most professionals don't have a clear picture of how their skills compared to what employers are actually looking for. This is a gap that career coaching has traditionally tried to fill, but the process was often slow and based on limited information. AI now makes it possible to assess your skills accurately and get direct, data-backed guidance on what to improve. In this article, we'll look at how AI is changing skill assessment, professional growth, and the broader career development process - from the moment you evaluate your abilities to the moment you land a role that actually fits.

Security Interviews Should Leave Room for What Remains Unknown

An incident story can sound impressively clear once everyone knows how it ended. The suspicious login becomes an obvious warning, the escalation looks inevitable, and the response appears to follow a straight path. A security interviewer needs to look earlier in the story, when the candidate had incomplete information and still had to choose what to do.

List of Best VMware Alternatives in the UAE

If you're a CIO in the UAE, you've probably had at least one conversation this year about what happens after VMware. Broadcom's licensing changes shook up a lot of long-term customers, and plenty of IT teams here are quietly running the numbers on what a move would cost. The good news is you're not short on options. The tricky part is that "VMware alternatives" in the UAE cover two different paths, and mixing them up leads to messy decisions.

How to secure Exchange Server beyond the CVE-2026-62911 fix

Remote access has always been a core part of how on-premises Exchange works. Users need OWA to read their email from outside the office. Their devices need Autodiscover to set themselves up automatically. Keeping both reachable means keeping Exchange accessible from the Internet, and that opens up more of the server than most organisations realise. CVE-2026-62911 is the latest example. Microsoft released the fix on August 11, 2026.

What is SLH-DSA? Hash-Based Post-Quantum Digital Signature Guide

SLH-DSA is NIST’s standardised post-quantum digital signature algorithm (hash-based). It generates quantum-resistant signatures, ensuring signatures are not changeable and that they will not be forged, even when later superseded by schemes like RSA and ECDSA, which are susceptible to attacks by quantum computers. Organisations are studying it today because large-scale quantum computers could, in the future, crack the algorithms that currently underpin most digital trust.

CVE-2026-67401: SQL Injection in cPanel's EmailTrack Puts Shared Hosting Environments at Risk

A critical SQL injection vulnerability has been identified in cPanel & WHM’s EmailTrack functionality. The vulnerability was disclosed by cPanel on September 8, 2026, affecting every supported release line. It allows an authenticated cPanel account holder with mail related privileges to ultimately achieve root-level code execution on the underlying host.

Cineworld Glitch Purportedly Allows Users To See Member Card Details

On 17 September 2026, users on X (formerly Twitter) posted that payment details belonging to other individuals had appeared on the Cineworld app under their personal accounts. On 17 September 2026, users on X (formerly Twitter) posted that payment details belonging to other individuals had appeared on the Cineworld app under their personal accounts.

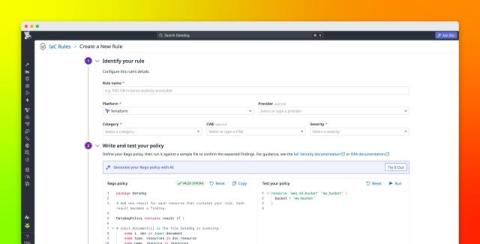
Enforce custom rules in Datadog IaC Security scanning

Infrastructure-as-code (IaC) security scanning can catch common misconfigurations before deployment, but every organization also has internal requirements that a default rule catalog cannot cover. For example, teams may need to enforce required tags, approved instance types, or naming conventions. With custom rules for Datadog IaC Security, security and platform teams can define these requirements as Rego policies and run them alongside Datadog’s default rules during IaC scans.