Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Verizon Sends New Smishing Warning

Verizon has renewed its warnings to customers about the threat of smishing, a social engineering approach that relies upon texts as opposed to other communication channels like the email used in phishing. The smishing problem may be smaller than the phishing problem, or the robocall nuisance, but it represents a comparable threat that organizations should address in their risk management process.
Contextual Data Analysis: A Game Changer in UEBA

As cyber threats continue to evolve, it's becoming more challenging for organizations to protect themselves from security threats. To stay ahead of cybercriminals, companies need advanced security tools like UEBA that can help detect anomalous behavior patterns that may indicate a security threat. However, the effectiveness of these tools largely depends on the quality and accuracy of the data they analyze.

Cybersecurity Asset Inventory in Your Home

Back in 2015, we published an article about the third party risks that are introduced into a home network. Now, eight years later, it is a good time to revisit the landscape of the home network. If we think about the technology in most homes in 2015, it was fairly sparse, consisting only of a router with an internet connection. The speed of most home internet connections was well below 100Mbps.

TA569: SocGholish and Beyond

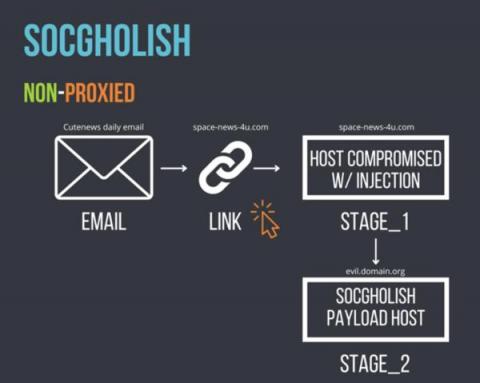
TA569 is a prolific threat actor primarily known for its deployment of website injections leading to a JavaScript payload known as SocGholish. In the past few months, Proofpoint researchers have observed changes in the tactics, techniques, and procedures (TTPs) employed by TA569. Changes include an increase in the number of injection varieties, as well as payloads deviating from the standard SocGholish “Fake Update” JavaScript packages.

Key Insights Into Gartner Report: How to Select DevSecOps Tools for Secure Software Delivery

With the advent of complex technology ecosystems like agile development processes, cloud-native platforms, and the rising use of open-source software, the importance of continuous Security and compliance has increased more than ever. As a result, leaders in the software industry must advise their teams to incorporate developer-friendly security tools into their DevSecOps pipelines.

How to find and manage privileged accounts in Active Directory

When it comes to securing Active Directory, the first place to start is usually getting a handle on what currently exists - getting a ‘lay of the land,’ so to speak. In Active Directory, the admincount attribute can play a role in identifying privileged accounts. It’s not without its faults, however. In this blog, we will explore the admincount attribute in more detail and potential uses it may have for determining which accounts may have or had privileged access.

Weekly Cyber Security News 25/05/2023

A selection of this week’s more interesting vulnerability disclosures and cyber security news. For a daily selection see our twitter feed at #ionCube24. If you are not familiar with Capita, they are one of the big contractor firms that the UK state tends to tender for projects. They don’t have a great reputation, and going by the latest fiasco, it has been shredded.

Colliding with the Future: The Disruptive Force of Generative AI in B2B Software

Over the past few months, our collective fascination with AI has reached unprecedented heights, leading to an influx of information and discussions on its potential implications. It seems that wherever we turn, AI dominates the conversation. AI has captivated the imaginations of tech enthusiasts, researchers, and everyday individuals alike. At the tender age of 11, I received my very first computer, the legendary ZX Spectrum. Looking back, it's hard to believe how much has changed since then.