Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

4 Easy Steps To Secure Mobile Field Work

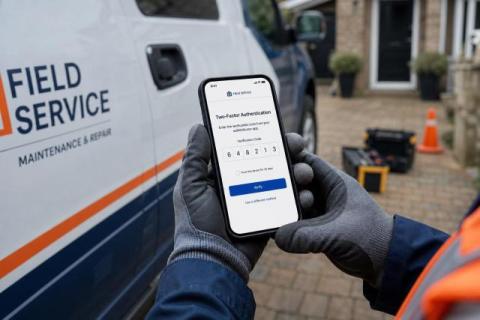
A field tech at a customer site can log into a scheduling app, pull up an invoice, and snap a site photo in under five minutes while connected to open Wi-Fi. That mobile device holds customer addresses, signed work orders, access codes, account credentials, and job-site photos. Unlike an office workstation that sits behind a firewall and never leaves the building, a field device moves through unfamiliar networks and high-risk physical spaces daily.
Guide to Agentic AI Governance

Agentic AI governance is about keeping powerful, autonomous AI systems aligned, safe, and accountable as they act on our behalf. It’s now a certainty that AI agents will be deployed enterprise-wide. So, we need to look more deeply into those agents, figure out where they are, how to find them, and fully understand what they are doing in deployment so we can prevent attacks. The most dangerous agentic attacks will not look like attacks at the layer where they originate.

How to Build a Durable AI Governance Program: A 3-Pillar Framework

AI adoption inside the enterprise has outpaced the governance built to contain it — 57% of employees have used AI tools for work without telling their manager. Policies get written and committees get formed, but exposure keeps accumulating, because data governance, AI oversight, and security are almost always run as three separate programs. In this video, Kovrr breaks down the three pillars that need to connect, and what separates a durable AI governance program from a documented one.

How agentic AI works inside your tools: A practical example with Acronis Service Desk

Author: Alexander Ivanyuk, Senior Director, Technology For many MSPs, AI still looks like an extra tool outside the real workflow: open a chatbot, paste in a ticket, ask for help, copy the answer back and continue working. It may save a few minutes, but it also creates more steps and more places where context can be lost.

How to Secure Agentic Coding Tools: Cursor and Claude Code

Cursor and Claude Code now read source code, install packages, and push commits with much of the access a senior engineer has, and often with less oversight. Give an agent a prompt to fix a bug, and it may pull a private API key from a config file, pass a customer record into its context window, or send a snippet of proprietary logic to a third-party model provider to reason about the fix. Security teams built policy for developers typing code by hand.

What is AI harness engineering?

Harness engineering is the practice of building the layer, including code, that turns an AI model from a text generator into an agent that can take actions. In short, an AI agent is a model plus a harness. The model decides what to do next, and the harness makes it happen, connecting the model to tools, context, external systems, and validation. In a lot of practical work, and especially in security work, the harness decides the quality of the output more than the choice of model does.

Who's Accountable When an AI Agent Makes the Wrong Call?

On a Tuesday morning in Q3, a procurement agent at a mid-market manufacturer approved a $340,000 payment to a vendor account. The vendor name matched the approved-vendor list. The invoice format matched the standard template. The agent verified both, cross-checked the amount against historical purchase orders, and released the payment through the treasury API within eleven minutes of the invoice arriving. No human touched the transaction.

Top 17 Agentic AI Security Solutions

Agentic AI security solutions help teams discover, govern, monitor, and control AI agents, copilots, LLM apps, MCP servers, and autonomous workflows. For security and DevOps leaders, they matter because agents can act across production systems. This guide compares leading tools and explains how to choose the right fit. AI agents are moving from assistants to actors.