Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

What Mythos Means for Your Vulnerability Management Team

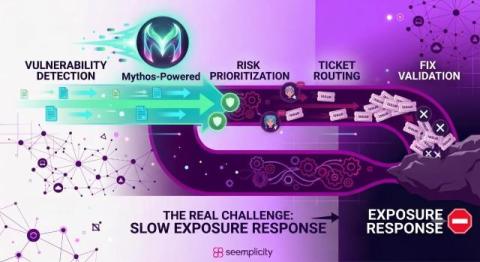
Modern exposure management has evolved beyond vulnerability scanning and alert volume into a discipline focused on measurable risk reduction. As the exposure management market matures, security leaders are adopting cyber exposure management platforms that unify signals across vulnerability, cloud, application, and attack surface tools to prioritize what truly matters.

Episode II: Attack of The Claudes

Two weeks after Hugging Face disclosed an AI-driven intrusion into part of its production infrastructure, Anthropic said it had found three incidents from its own cyber evaluations. Hugging Face traced its compromise through a data-processing pipeline, where a malicious dataset abused a remote-code dataset loader and a template-injection issue in a dataset configuration.

How AI Governance Reduces Security Risks

AI governance reduces security risk by enforcing least-privilege access, protecting the data and credentials AI systems handle and making every AI action auditable. This matters because most organizations deploy AI faster than they can govern it. Employees adopt unsanctioned tools, and autonomous AI agents are created under existing user identities. Each one adds unmonitored machine identities that expand your attack surface – the exact gap that governance closes.

EU AI Act Compliance Roadmap: What Enterprises Must Document and When

The EU AI Act reached a turning point this summer, and the headlines got it half right. Obligations for high-risk AI systems were postponed to December 2027 under the Digital Omnibus, adopted in June 2026. The transparency rules under Article 50 were not postponed, and they apply from August 2, 2026. ‍ Enterprises reading spring 2026 guidance are working from a timeline that no longer exists, and enterprises reading the headline about a delay may believe nothing is due.

The API Security Gap Behind Recent Supply Chain Breaches

Most coverage of software supply chain attacks focuses on the entry point: the poisoned package, the compromised maintainer account, the malicious commit. That’s the part that makes headlines, but it’s rarely the part that causes the damage. A malicious package sitting on a developer’s machine doesn’t exfiltrate anything by itself.

Many New Technologies, Products, and Tools for Modern Protection Programs in New York, New Jersey, and Florida

A lot of buyers still start with the most visible layer of protection: cameras, guards, or a front desk presence. The real gap usually sits behind that first impression. If doors, credentials, visitor flow, and response routines are loose, the rest of the program ends up documenting problems instead of preventing them.

The AI notetaker you can't see in the participant list

For about three years, the governance question around AI meeting assistants had a convenient property: you could see them. The tool joined the call as a named participant. It appeared in the attendee list. Everyone in the meeting had at least the theoretical opportunity to object, and a security team reviewing an incident could reconstruct which meetings had been recorded by looking at who else was in them.

Paul Maritz: Partner Cloud in the AI era | Acronis Accelerate Event

How is the AI era creating new opportunities for service providers through partner cloud? In this keynote from Acronis Accelerate, technology investor, former Acronis Chairman, and former VMware CEO Paul Maritz explores how service providers can turn local infrastructure into a cost advantage and competitive edge as customers increasingly require partner infrastructure for compliance and data sovereignty. Learn how Acronis Cyber Frame, built specifically for service providers, is a natively integrated solution that enables SPs to deliver infrastructure services (VMs, storage, networking) with integrated backup, DR, security and RMM.

How Regulated Data Leaks Through AI, One Paste at a Time

A support coordinator has a difficult letter to write. The customer record is open in one tab, a consumer AI assistant in another, and the deadline is this afternoon. She selects the record, copies it, pastes it into the prompt box, and asks for a polite draft. Thirty seconds later she has a good letter and a regulatory problem, and nobody in the organization knows about either. ‍ The sequence below traces that single action through to its consequences.