Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

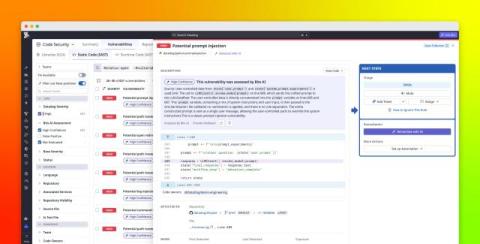
Detect vulnerabilities in LLM applications with Datadog's AI-native SAST

AI coding tools help developers build and deploy LLM applications quickly, but this speed comes with new security risks. Traditional static application security testing (SAST) tools that are pattern based weren’t designed to detect LLM-specific issues such as prompt injection sinks and exposed system prompts. These vulnerabilities often don’t become apparent until applications are already running in production, when remediation is more difficult and expensive.
From signals to systemic risk: Building Risk AI

Security and engineering teams contend with a constant stream of signals about vulnerabilities, incidents, misconfigurations, identity risks, control gaps, and other findings across their environments. But an individual finding’s severity does not always reflect its potential organizational impact.

Agentic First Security -- Customer Brown Bag - August 20th, 2026

Join Jeremy Powell, CISO of Sumo Logic, to learn how AI-powered agents are reshaping modern security operations. Discover the key principles, governance, and best practices for building an agentic security program that enhances analyst productivity, accelerates threat response, and strengthens organizational resilience.

Give your agents capabilities

Accelerating security solutions for small businesses‍ Tagore offers strategic services to small businesses. A partnership that can scale‍ Tagore prioritized finding a managed compliance partner with an established product, dedicated support team, and rapid release rate. Standing out from competitors‍ Tagore's partnership with Vanta enhances its strategic focus and deepens client value, creating differentiation in a competitive market.

From all-or-nothing to task-based OAuth consent

Since June, developers have created thousands of third-party OAuth apps on Cloudflare, with more than a million authorizations since. OAuth makes delegated access possible. It lets applications act on a user’s behalf without asking them to handle long-lived credentials or hand over a password. That model works well when an application can describe its access needs with a small set of scopes. Developers use OAuth for SaaS integrations, internal tools, CLIs, and agents.

Is a SOC 2 Report Enough to Assess a Cloud Vendor?

A vendor sends over a SOC 2 report. It lands in the queue, someone reads the cover page, sees the auditor's name and a clean-looking opinion letter, and marks the assessment complete. The reviewer moves on to the next vendor. Multiply that by a few hundred vendors a year, and it becomes less of a decision and more of a reflex.

Report: One-Quarter of Breaches Are Enabled by AI-Driven Attacks

A new report commissioned by IBM has found that one in four breaches is now AI-enabled, up 56% from last year. “Most AI-driven attacks reported in the study targeted critical infrastructure sectors (62%), with financial services and energy organizations experiencing the highest concentration, raising the risk of broader systemic disruption,” the report says. “Financial services breaches were reported to cost on average $6.3 million, while energy breaches cost on average $5.2 million.

The Rise of the 'Non-Human Insider': When AI Agents Become the Threat

For years, cybersecurity has had a familiar villain: the external attacker. The hacker breaking through the firewall, stealing credentials or exploiting an unpatched vulnerability. It is the scenario we have trained for, built defenses around and spent decades trying to prevent. But the next major breach may not begin with someone breaking into your environment at all, it may begin with an AI agent that already has access.

What is Security Posture Management and Why is it Important?

Modern organizations don't operate from a single server room anymore. Today's enterprise environment spans dozens of cloud services, SaaS applications, APIs, AI agents, and non-human identities, all of which are continuously changing. A quarterly security audit is no longer a safety net, but now considered a gap.

451 Research report: How agentic AI is redefining identity security

In the short time that AI agents have been a part of the enterprise, they have upended many of our bedrock assumptions about the nature of identity, access, development, and work itself. At 1Password, we’ve been in the trenches of the agentic revolution; we’ve seen its positive impact on productivity, and the serious concerns it raises about security.